Why Smart Contract Security Is Failing at the Exact Moment Institutions Need It Most
Most 2025 smart contract exploits were preventable. Discover what the data reveals about security maturity and how enterprises must change.

2025 marked a structural inflection point for crypto.
Institutional engagement shifted from limited experimentation to sustained, production-level deployment. Tokenized treasuries and real-world assets moved beyond pilots and into balance sheets. Stablecoins continued to expand as a settlement and liquidity layer, increasingly embedded in payments, treasury operations, and market infrastructure.
For what that shift means in practice, see our guide to institutional smart contract security.
This transition fundamentally changed the context in which crypto systems operate. Capital on-chain in 2025 was no longer primarily speculative. It was operational, regulated, and accountable to institutional risk frameworks.
With that shift came a higher bar.
Institutions do not optimize for novelty or speed alone. They optimize for reliability, predictability, and provable controls. Systems that custody, route, or settle value are expected to behave deterministically, with clearly defined failure modes and measurable assurance.

And yet, despite this maturity, exploits continued.
Throughout 2025, smart contract losses did not slow in proportion to adoption.
Protocols grew larger. Capital pools deepened. Systems became more interconnected.
But exploit frequency and impact remained stubbornly persistent.
This creates a structural mismatch.
On one side, institutional capital is moving on-chain with expectations shaped by traditional finance, payments infrastructure, and other mission-critical systems. These environments assume deterministic behavior, strict controls, and provable safeguards.
On the other side, too many crypto systems still rely on late-stage reviews and reactive defenses.
That gap is no longer acceptable.
When experimental capital is at risk, failure is tolerated as part of innovation. When operational capital is at risk, failure is treated as a control breakdown.
Institutions do not budget for preventable exploits. They do not view loss events as “learning experiences.” They expect systems that custody and route value to meet reliability standards comparable to banking, exchanges, or critical infrastructure.
In practical terms, tolerance for failure has gone to zero.
Security expectations have fundamentally changed.
The question is no longer whether exploits will occur. The question is whether they should have been possible in the first place.
For most of 2025’s incidents, the answer was no.
And that is the problem.
What the 2025 Exploit Data Actually Shows
To understand whether these failures were inevitable or preventable, we conducted a structured review of every major 2025 EVM smart contract exploit that fell within scope. Not anecdotes. Not selective examples. A comprehensive analysis of real production incidents and real financial losses.
The findings were consistent.
Most losses did not stem from novel cryptographic breaks or sophisticated zero-day techniques. They originated from familiar engineering failures, the kinds of issues that have existed in software systems for decades.
The most common vulnerability classes were:
Logic and state transition errors
Accounting and precision flaws
Access control gaps
Broken or unenforced invariants

In other words, contracts behaved exactly as written, just not as intended.
These were not attacks that required extraordinary creativity. They were valid execution paths that violated economic assumptions the protocol never formally enforced.
The largest incidents of the year illustrate the pattern.
Balancer lost approximately $121 million due to asymmetric rounding and precision drift inside pool math. A deterministic accounting flaw compounded over many small swaps until value leakage became material.
GMX lost roughly $42 million when user-controlled receiver logic enabled cross-contract reentrancy, bypassing routing safeguards and breaking price integrity assumptions.
Cork lost around $12 million after missing access control in Uniswap V4 hooks allowed attackers to inject fabricated deposits and mint unbacked derivatives.
BetterBank lost $5 million because reward logic validated token addresses but not authorized liquidity pairs, allowing attackers to mint incentives from unauthorized pools.
These were not edge cases. They were design and validation gaps.
Each exploit followed a clear path from assumption to failure: code shipped → assumption untested → invariant violated → value extracted.
This is where the preventability analysis becomes critical.
Across the 50 in-scope exploits reviewed, Olympix would have prevented 49. That represents approximately 98 percent of incidents and roughly $247 million in losses that could have been stopped before deployment.
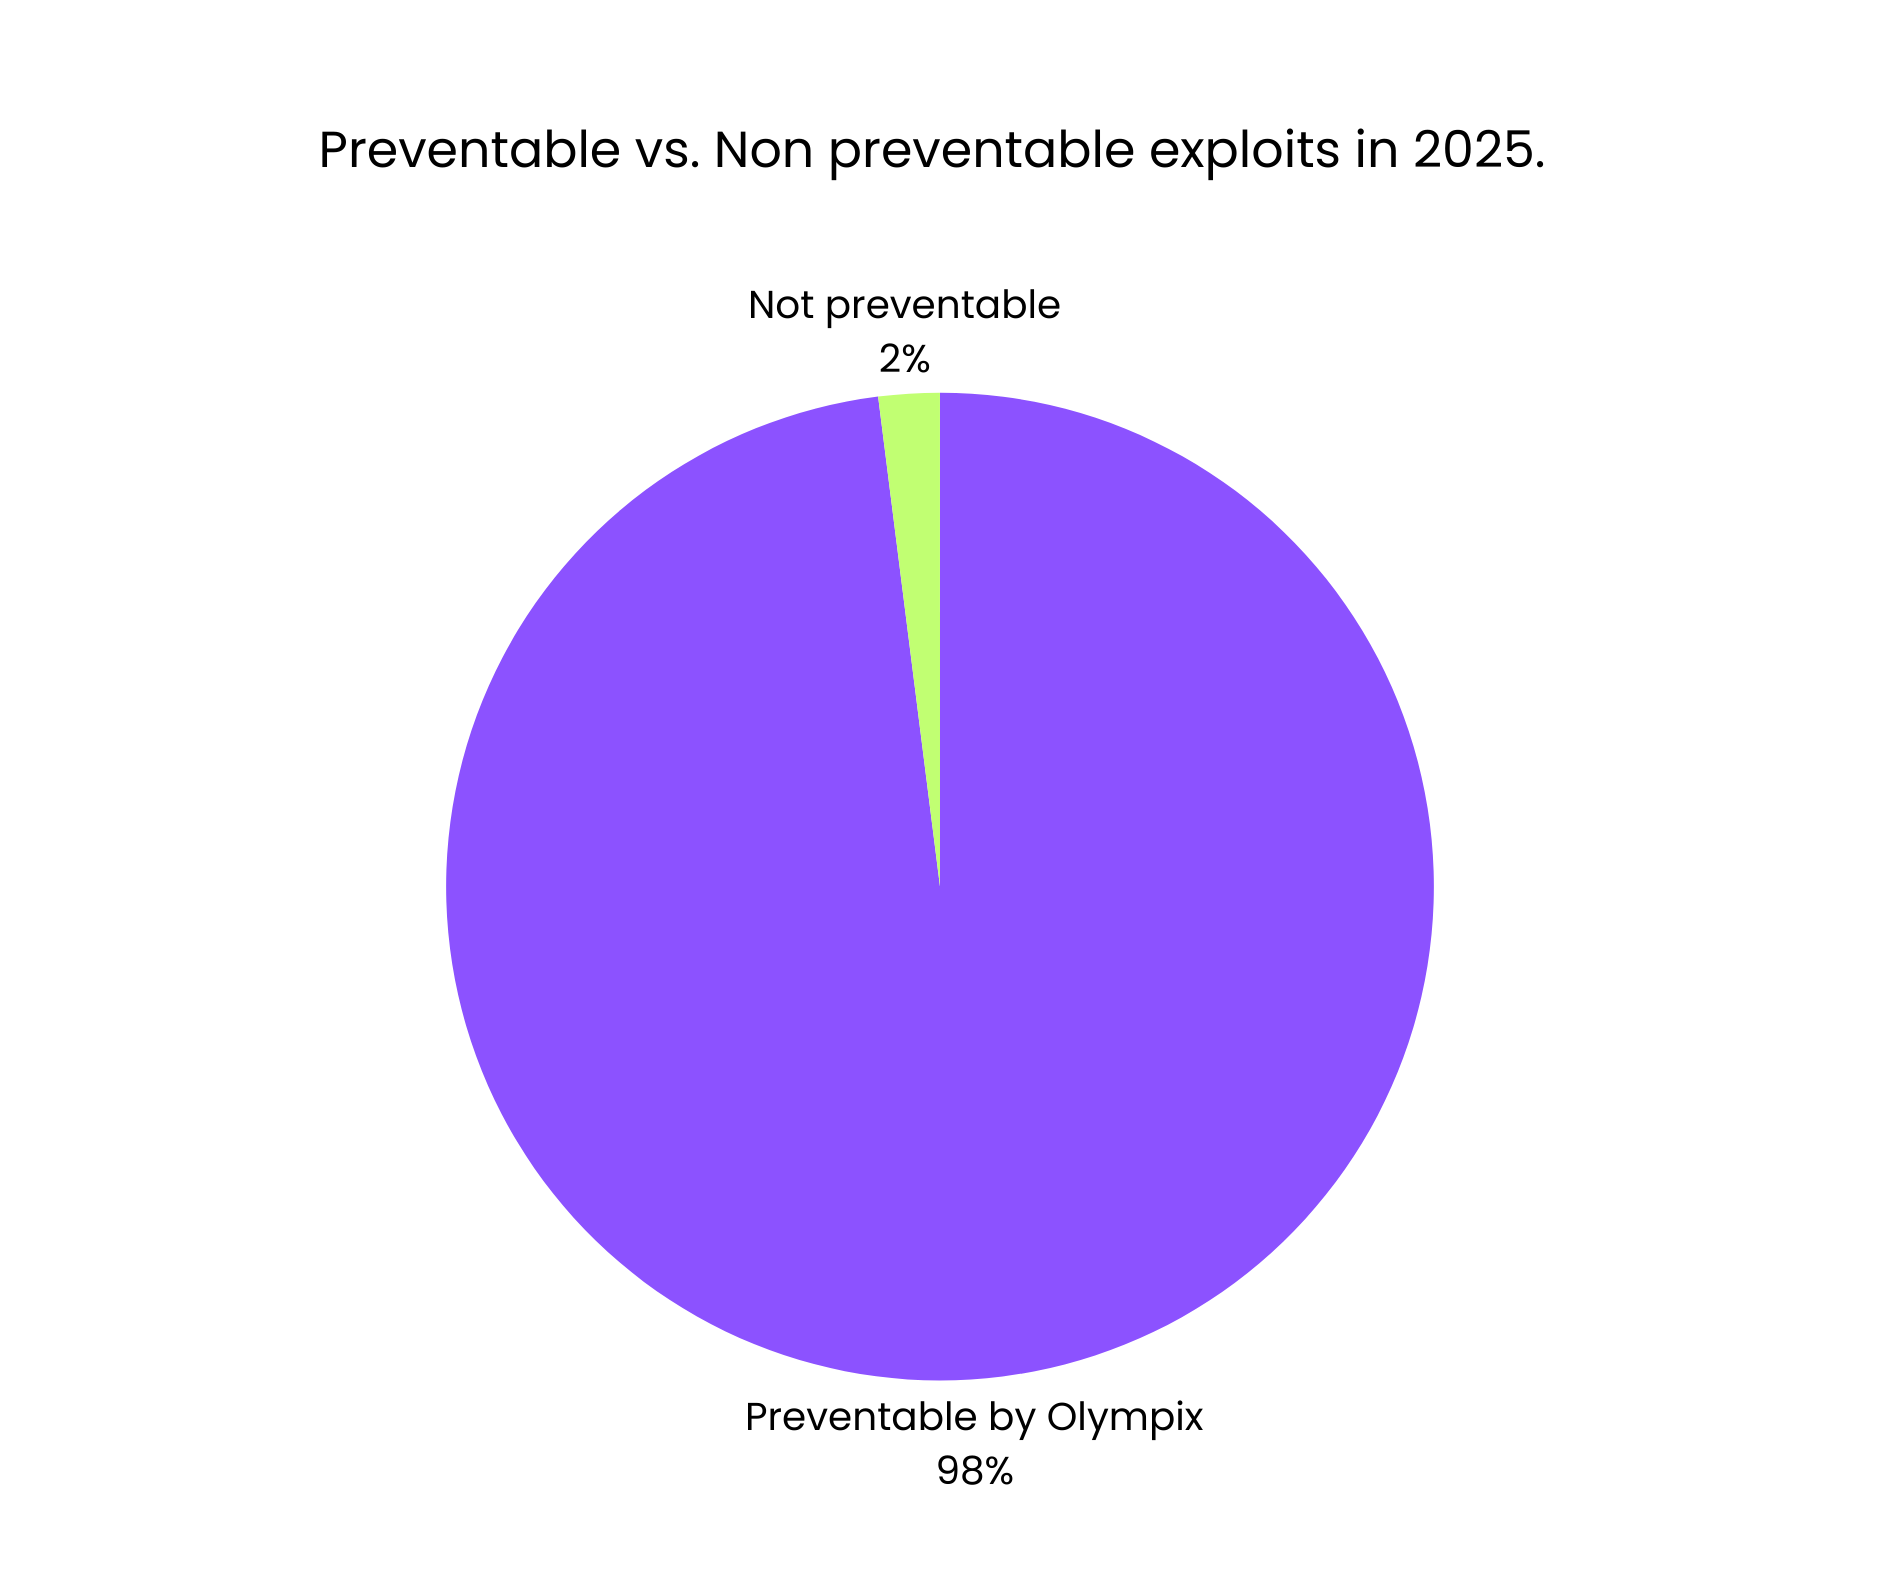
Preventable, in this context, does not mean “might have been caught with more diligence.” It means the vulnerable logic was already present in the codebase and detectable through deterministic testing during development.
The risk was knowable. It simply was not measured early enough.
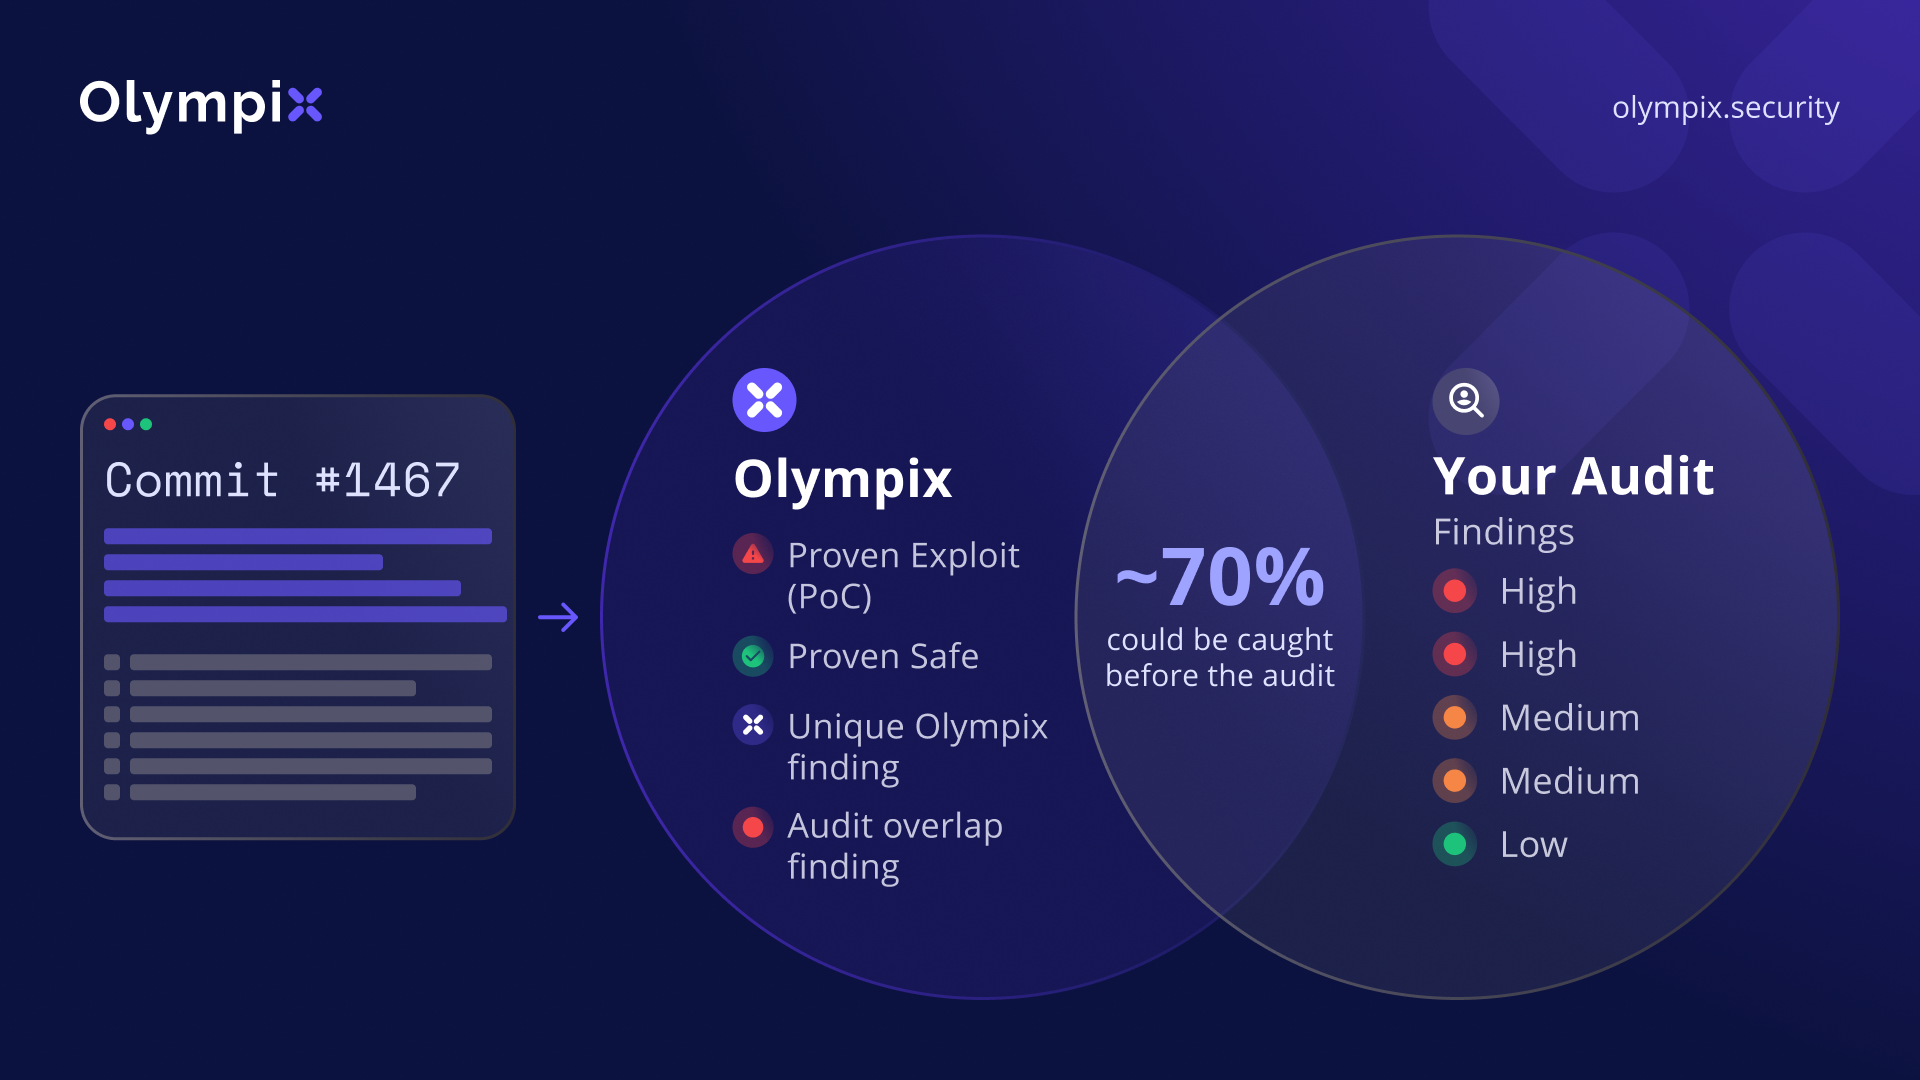
The conclusion is not that teams lacked effort or audits, since most affected protocols had undergone multiple reviews. An audit covers what reviewers examine within a fixed scope, and the vulnerable paths sat outside what anyone checked before capital was at risk.
Once an exploit surfaces those paths in production, remediation becomes slower, more expensive, and sometimes impossible without disruptive migrations.
The data points to a systemic issue. Security is still being treated as a late-stage checkpoint, when it must function as a continuous, development-stage control.
And at institutional scale, that difference determines whether losses are routine or rare.
Why the Current Smart Contract Security Model Falls Short
These findings point to a larger structural issue.
The prevailing security framework is misaligned with how risk actually manifests in smart contracts.
Audits remain necessary but insufficient. An audit covers what a team of reviewers examines within a fixed scope, and the execution paths that drained protocols in 2025 often sat outside it. Even when an auditor does identify a flaw, remediation can require redesign, migration, or risky patchwork changes in production.
Monitoring and incident response sit even further downstream. They are reactive controls. They detect failure while it is already occurring, when capital is already exposed and losses are already unfolding on-chain.
Neither layer was designed to prevent vulnerabilities from shipping in the first place.
The result is predictable. Discovery happens late. Blast radius increases. Recovery becomes expensive, public, and often irreversible.
For institutions operating under fiduciary and regulatory expectations, this model is insufficient. Prevention must occur earlier, during development, where risk can still be eliminated rather than contained.
Security Standards Must Match the Value at Risk
Other high-risk industries solved this problem years ago.
When software controls aircraft, medical devices, rail systems, or nuclear infrastructure, “best effort” testing is not considered acceptable. Manual reviews, spot checks, and late-stage audits are not treated as primary safeguards.
Those sectors rely on formal methods, deterministic testing, and mathematically grounded verification.
Not because it is elegant, but because failure is unacceptable.
In aerospace, defense, and critical financial systems, teams are expected to prove certain behaviors cannot occur. Security is not inferred from process completion. It is demonstrated through evidence.
Crypto has reached the same risk profile.
Smart contracts now custody billions of dollars, settle real financial transactions, and increasingly serve institutional participants. A single logic error can trigger irreversible loss, market contagion, and systemic impact across protocols.
Yet the dominant security practices in crypto still resemble early-stage software development: periodic audits, reactive monitoring, and probabilistic analysis layered on after deployment.
That mismatch is no longer sustainable.
If digital assets are to support institutional capital at scale, they must be held to the same assurance standards as other mission-critical systems.
Security must move from “review and respond” to “verify and prevent.”
From Probabilistic Review to Deterministic Assurance
Formal methods are not a new concept. They are a class of techniques used to mathematically specify, analyze, and verify system behavior before failure occurs.
At their core, formal methods answer a different question than traditional security tools.
Most security reviews ask: “Did we find any obvious issues?”
Deterministic testing asks: “Can this system ever enter an invalid or unsafe state?”
For smart contracts, this distinction matters.
Smart contracts execute deterministically. Given the same inputs and state, they will always produce the same outcome. There is no uncertainty at runtime. Every execution path is fixed, and every state transition is defined in code.
Security validation must reflect that reality.
Deterministic testing focuses on:
Explicitly defining protocol invariants, such as value conservation, authorization boundaries, and pricing correctness
Systematically exploring execution paths and state transitions, not just individual functions
Searching systematically for concrete counterexamples, executions that break an invariant, rather than sampling for likely bugs
This approach shifts security earlier in the development lifecycle.
Instead of relying on late-stage audits to discover vulnerabilities after architectural decisions are finalized, deterministic testing validates correctness while code is being written, when risk can still be removed rather than mitigated.
In practice, this means integrating invariant enforcement, mutation testing, and formal validation into continuous integration pipelines. Security becomes repeatable, measurable, and enforceable, rather than advisory.
For institutional systems, this is the expectation, not an optimization.
As smart contracts increasingly underpin financial infrastructure, deterministic assurance is not an advanced technique. It is the minimum standard required to operate at scale.
Why AI Security Engineers Are Not the Answer
AI has meaningfully improved developer productivity. It accelerates code generation, test writing, and even vulnerability discovery. Many teams now use AI-assisted scanners and automated reviewers as part of their workflow.
However, there is a growing misconception that AI alone can substitute for rigorous security engineering.
It cannot.
Most AI-based tools operate probabilistically. They identify patterns, flag anomalies, and estimate risk based on historical data and learned behavior. This approach is useful for prioritization and triage, but it does not provide guarantees.
And guarantees are exactly what financial infrastructure requires.
A probabilistic system can tell you that something is likely safe, but it cannot hand you the concrete execution that breaks it.
That distinction is critical in deterministic environments like smart contracts.
When a contract controls millions or billions of dollars, “probably secure” is not a defensible risk posture. Institutions require concrete evidence about specific failure modes, not a sense that they appear unlikely.
The 2025 exploit data reinforces this reality. Most incidents were not novel or creative edge cases that required intuition to uncover. They were straightforward logic and invariant failures that could have been deterministically detected with systematic validation.
AI may help surface symptoms faster, but it does not replace deterministic evidence.
In practice, AI should be treated as an assistive layer, not a foundation. It can accelerate reviews, expand coverage, and support engineers. But it cannot replace explicit invariants, formal reasoning, and deterministic testing.
Security for financial systems cannot depend on statistical confidence alone. It needs deterministic evidence, meaning a reproducible counterexample whenever an invariant can be broken.
Used as a supplement to rigorous engineering, AI makes teams faster and safer. Used as a substitute, it leaves them learning about risk the way the industry did in 2025, after deployment.
Security Maturity Requires Evidence, Not Probability
The data from 2025 makes one point unmistakably clear.
Smart contract security did not fail because the industry lacks tools, talent, or effort. It failed because the paths attackers used sat outside what reviews covered, and nothing searched them systematically before deployment.
Most exploits originated from logic that was valid, deployed, audited, and live. By the time issues surfaced, the cost of correction was high and the blast radius unavoidable. This is not a tooling gap. It is a maturity gap.
As digital assets move deeper into institutional balance sheets, tolerance for probabilistic security will continue to decline. Financial systems are expected to provide guarantees, not confidence intervals. That expectation already exists in other high-risk industries, and it is now being applied to onchain infrastructure.
Security cannot remain a downstream control.
It must become a development-time discipline.
That shift requires deterministic validation, explicit invariants, and continuous verification as code is written, not after value is at risk.
How Olympix Fits In
Olympix was built to support this next stage of security maturity.
Our deterministic security tools are designed to identify logic flaws, invariant violations, and exploitable assumptions during development, before deployment and before audit. The same failure patterns that drove the majority of 2025 losses are systematically detectable when security is integrated early.
If your organization is building or securing financial infrastructure on EVM, now is the moment to reassess how risk is discovered and when.
Find vulnerabilities before they ship, not after.
Explore Olympix’s deterministic security platform and see how shift-left verification changes the economics of smart contract risk.
👉 Learn more or request a demo at olympix.security
More from the blog
See every article →



See what Olympix finds on your own code
Send us a repo that's already been audited, and we'll run Olympix at the same commit and show you what comes back.