
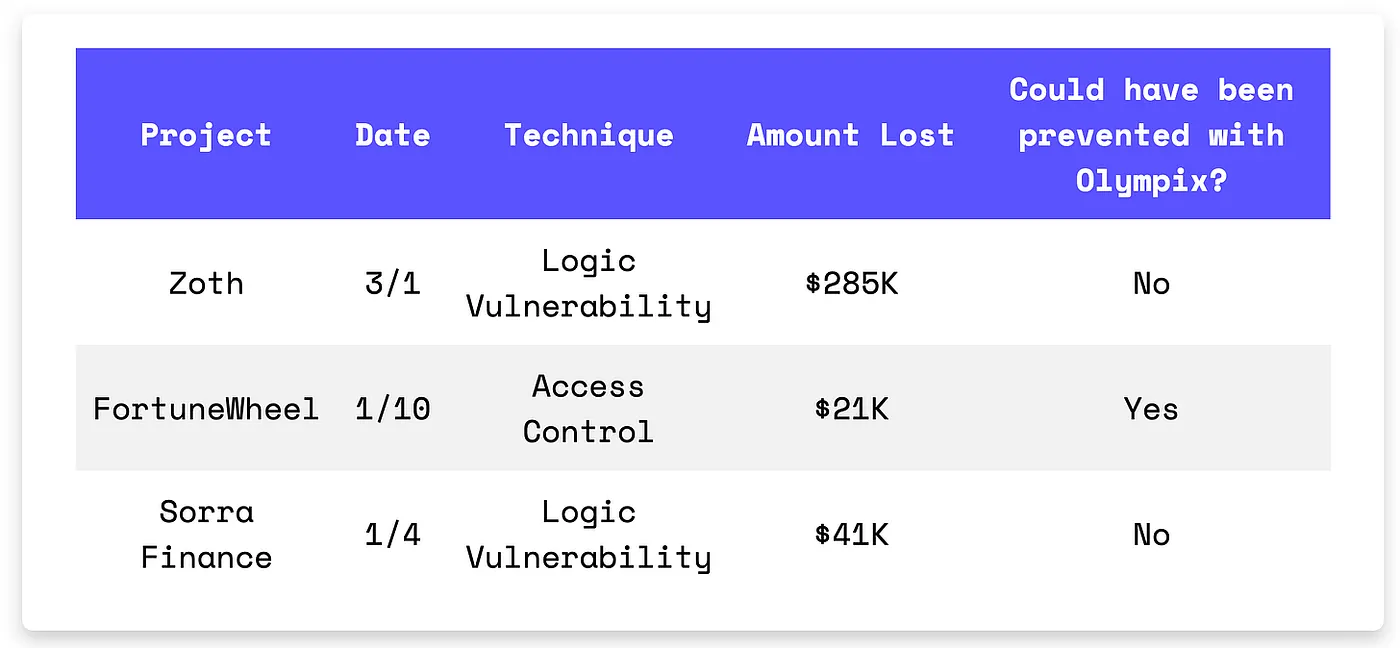
Zoth lost $285K from a faulty LTV calculation that ignored real collateral amounts. FortuneWheel leaked $21K due to missing access controls on a profit-swap function. Sorra Finance’s $41K loss came from a reward function that didn’t track previous payouts, allowing repeat claims.
On March 1, the Zoth exploit on the Ethereum mainnet resulted in a $285K loss due to a logic vulnerability. The attacker targeted a flaw in the mintWithStable() function’s Loan-to-Value calculation. The attacker first used flash loans to manipulate the exchange rate on Uniswap V3. The manipulated rate made the deposit swap for just 7,669 collateral tokens instead of 330,979. The contract looked at the initial deposit amount, not the actual collateral received, letting them mint too much ZeUSD based on the higher 330,979 number. They burned the ZeUSD and withdrew 330,979 collateral tokens, profiting $285K.

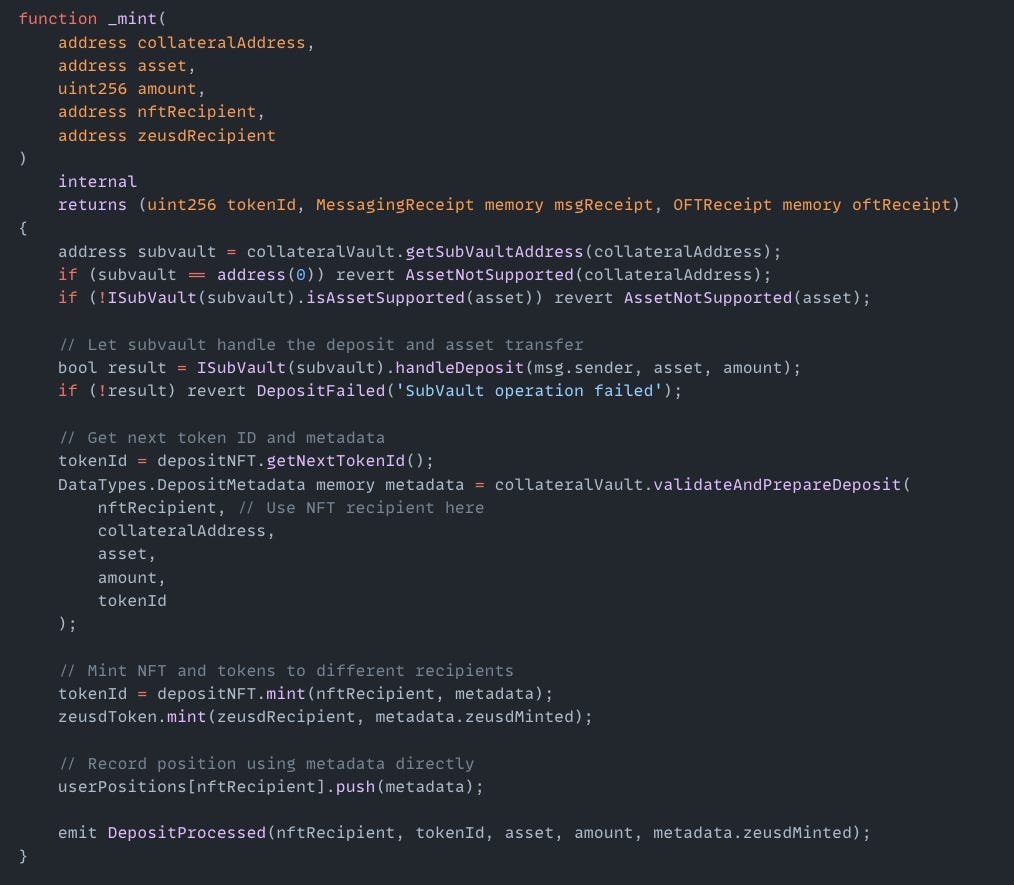
Exploited Contract: 0xe257495224eb1bd710ff18c3758c8a87cde46137
Transaction: 0xc3f70057e261af554c6acf6a372389899f0c2d7d1ebd27311e39525dee88fb39
On January 10, the FortuneWheel exploit on the Binance Smart Chain resulted in a $21,000 loss. The root cause of the exploit was that the swapProfitFees() function was missing access controls. This function swaps tokens owned by the contract to WBNB via PancakeSwap. Only admins should have access to trade with the contract’s earnings. The attacker traded WBNB for LINK externally, artificially increasing LINK token’s price in the pool. Then, the attacker called swapProfitFees() to swap the contract’s LINK back to WBNB at the higher rate, making a profit.

Exploited Contract (on BSC): 0x384b9fb6e42dab87f3023d87ea1575499a69998e
Transaction: 0xd6ba15ecf3df9aaae37450df8f79233267af41535793ee1f69c565b50e28f7da
On January 4, the Sorra Finance exploit on the Ethereum Mainnet resulted in a $41K loss. The root cause of the exploit was that the getPendingRewards() function failed to track the rewards already paid out correctly. The attacker first deposited 122,868 SOR tokens on December 21, 2024, picking a 14-day lockup (tier 0). After the lockup ended, they called withdraw() repeatedly. This function paid out 6,143 SOR tokens as rewards each time but didn’t mark them as claimed. The contract’s logic failed to subtract userRewardsDistributed[_msgSender()] properly, letting the attacker claim the same rewards multiple times.
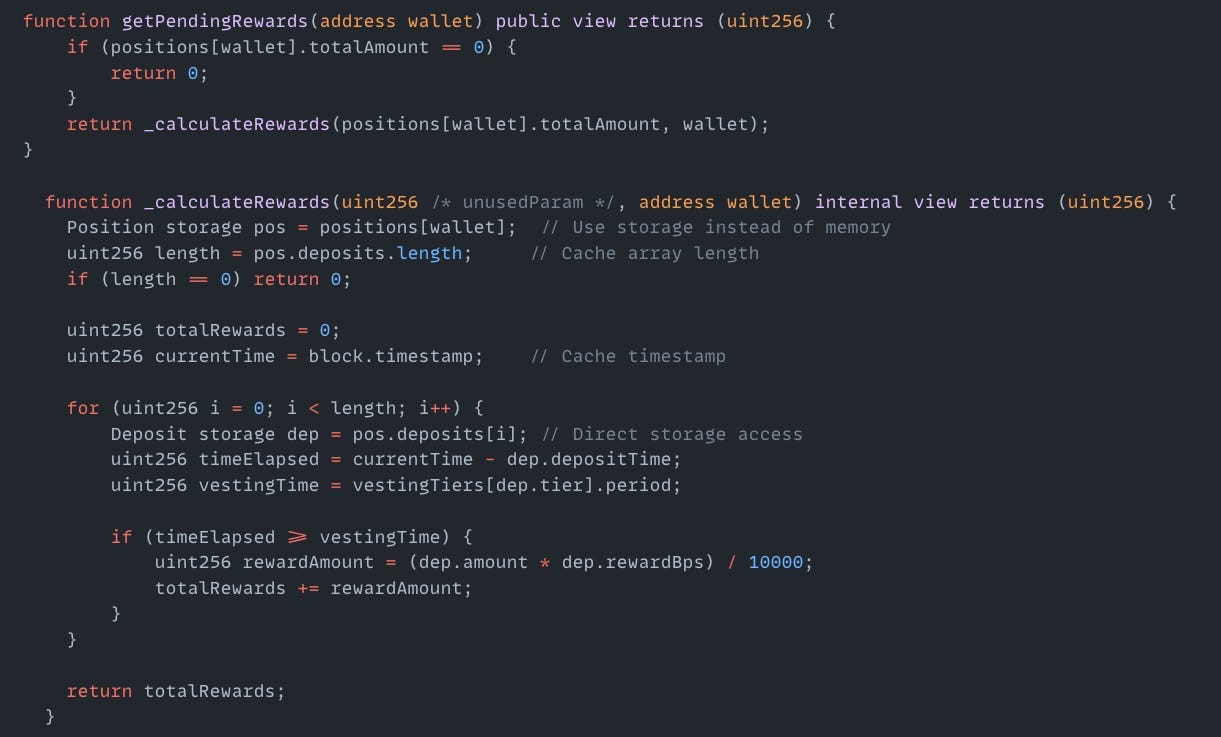
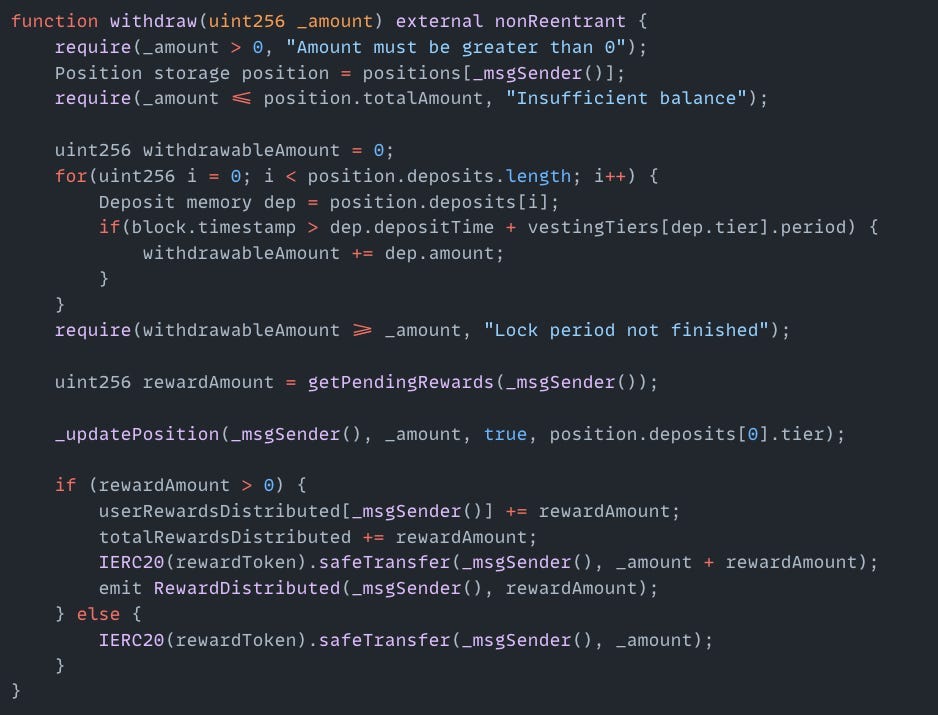
Exploited Contract: 0x5d16b8ba2a9a4eca6126635a6ffbf05b52727d50
Transaction: 0x6439d63cc57fb68a32ea8ffd8f02496e8abad67292be94904c0b47a4d14ce90d