
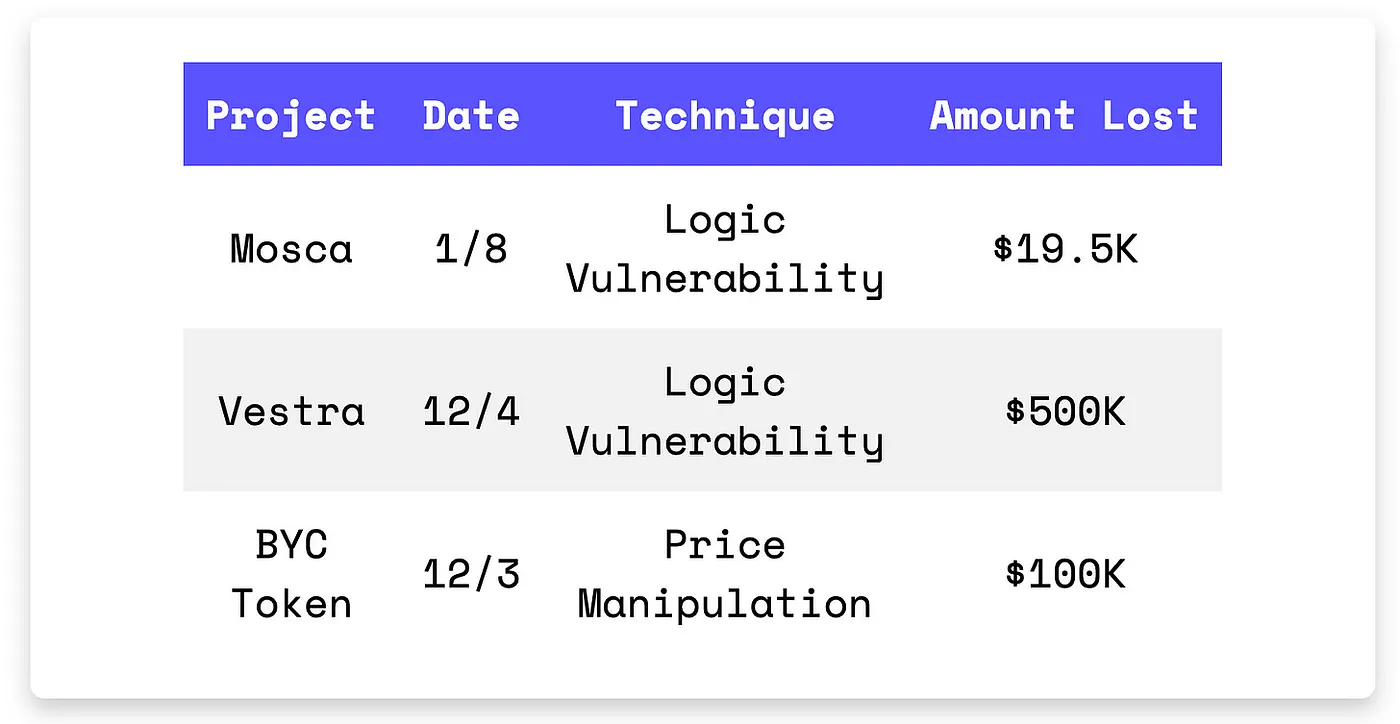
Vestra lost $500K after failing to check if staking positions were still active, allowing repeated yield withdrawals. Mosca leaked $19.5K due to a flawed state reset that didn’t clear USDT and USDC balances. BYC was manipulated for $100K when its autoBurnLiquidity() function let attackers burn supply and inflate prices.
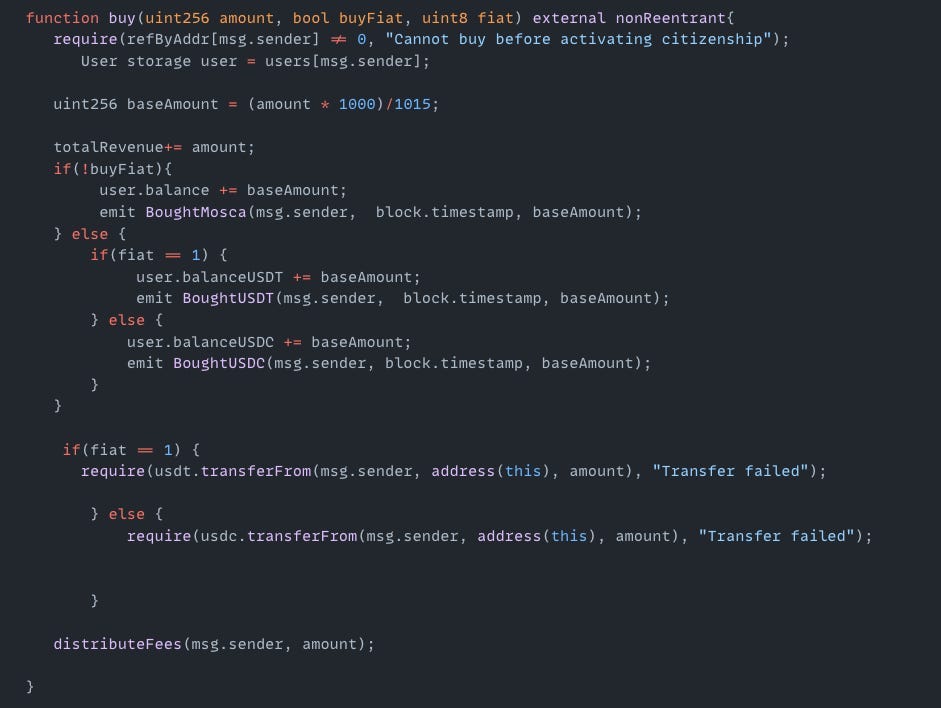
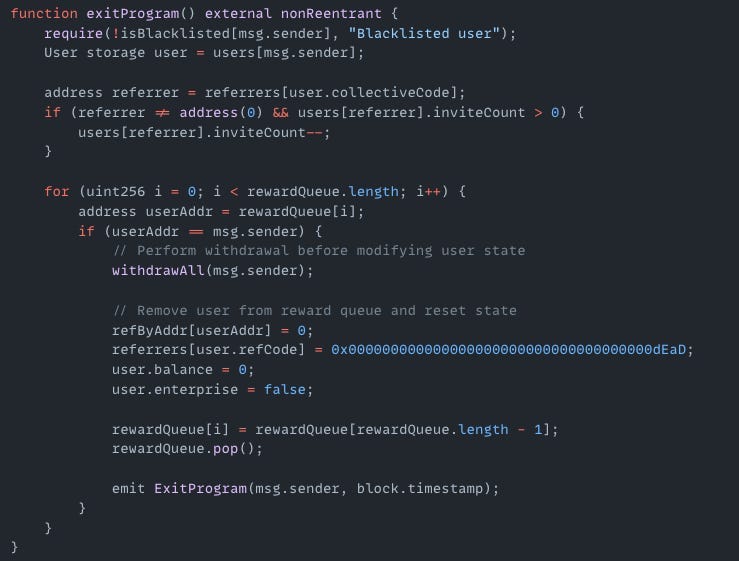
On January 8th, the Mosca exploit on the BSC resulted in a $19.5K loss. The root cause of the exploit was improper state updates in the exitProgram function. The withdrawAll() function calculated the withdrawal amount as the sum of user.balance, user.balanceUSDT, and user.balanceUSDC. However, only user.balance was reset to zero after the withdrawal, leaving user.balanceUSDT and user.balanceUSDC unchanged. The attacker manipulated this flaw by first calling the buy() function to increase their user.balanceUSDC. Next, they used the join() function to add their address to the rewardQueue. Finally, they withdrew funds using the exitProgram() function, leveraging the incomplete state reset.

Exploited Contract (on BNB): 0x1962b3356122d6a56f978e112d14f5e23a25037d
Transaction: 0x4e5bb7e3f552f5ee6ee97db9a9fcf07287aae9a1974e24999690855741121aff
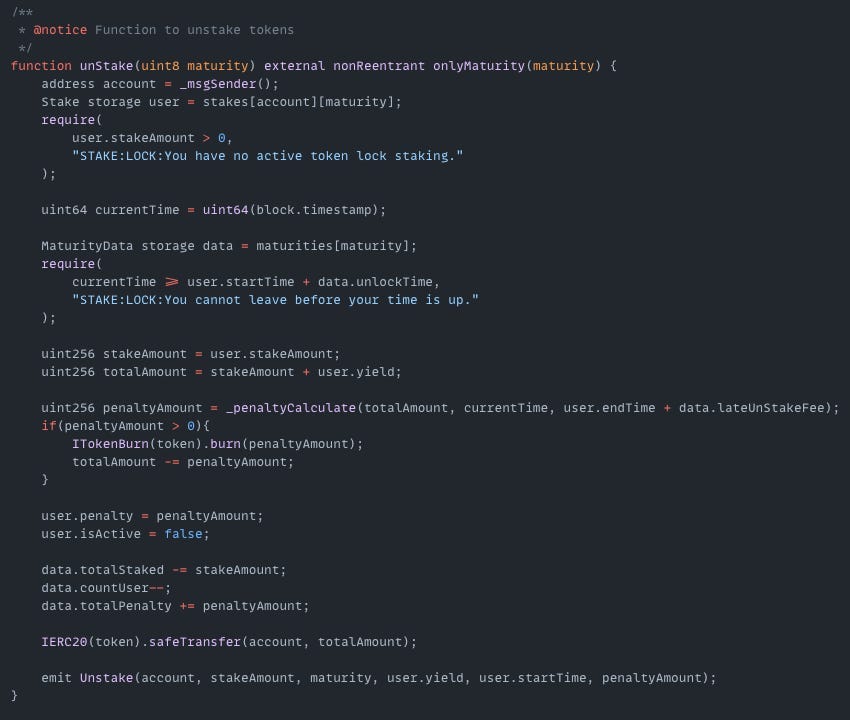
On December 4th, the Vestra exploit on the Ethereum mainnet resulted in a $500K loss. The root cause of the exploit was the unStake() function, which failed to verify if a staking position was still active before allowing yield withdrawal. This enabled the attacker to claim yield from an already unstaked position. The exploit began a month earlier when the attacker staked 500,000 VSTR tokens to earn yield after the lock period. Once the lock expired, the attacker called unStake() to withdraw 500,000 VSTR plus 20,000 VSTR in yield. However, due to the missing isActive check, the attacker continued to call unStake() on the same position, repeatedly earning 20,000 VSTR per call. To avoid depleting the staking pool, the exploiter deployed new contracts to stake 500,000 VSTR tokens each time, keeping the pool’s total balance intact while exploiting the logic flaw.
Exploited Contract: 0x8a30d684b1d3f8f36b36887a3deca0ef2a36a8e3
Transaction: 0xa0dcf9b177702c58c5d0353aff2caeab12589bce204fb2d0e62ccbf5717f1798
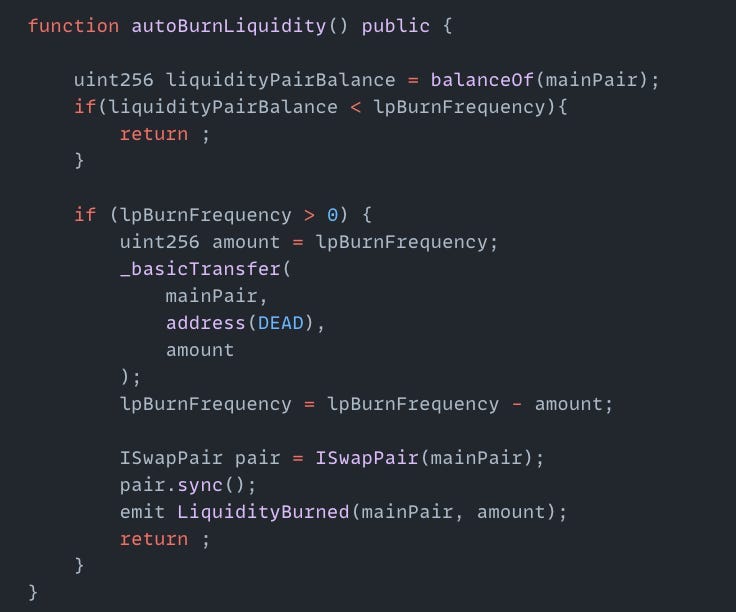
On December 3rd, the BYC token exploit on the BSC resulted in a $100K loss due to a price manipulation attack. The root cause of the exploit was that the attacker was able to burn the BYC tokens by using the autoBurnLiquidity() function reducing the total supply and artificially increasing the token price. The attacker then sold the BYC tokens at the manipulated higher price for profit.
Exploited Contract (on BNB): 0x9a69eb74060e2808344ac35bb5825051b89bbe76
Transaction: 0x177b87bd009e3b3aebb11cf2b88efc217d14fc1554a4675ee749eeb527d201ff