
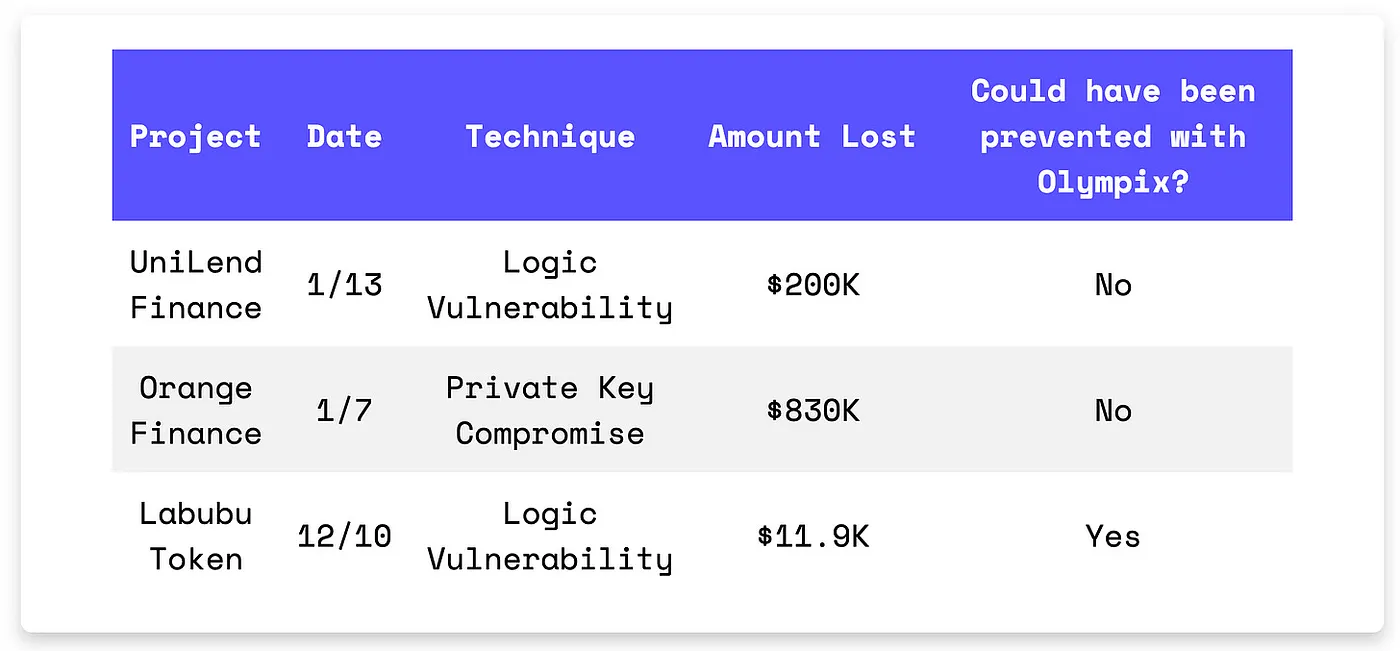
UniLend lost $200K after failing to update token balances before collateral checks, enabling multiple stETH withdrawals. Orange Finance suffered an $830K loss due to private key compromise and poorly configured multi-sigs. Labubu leaked $11.9K when attackers looped self-sending transfers to inflate balances via flawed state updates.
On January 13th, the UniLend Finance exploit on the Ethereum mainnet resulted in a $200K loss due to a sequencing flaw in the redeemUnderlying function. The function checks a user’s health factor using the pool’s token balances before updating them to reflect burned LP tokens or withdrawn collateral. This outdated pool balance check allowed the attacker to manipulate the function into believing sufficient collateral remained in the pool. By depositing 60M USDC to inflate their lending shares, the attacker withdrew stETH collateral multiple times, bypassing proper validation.
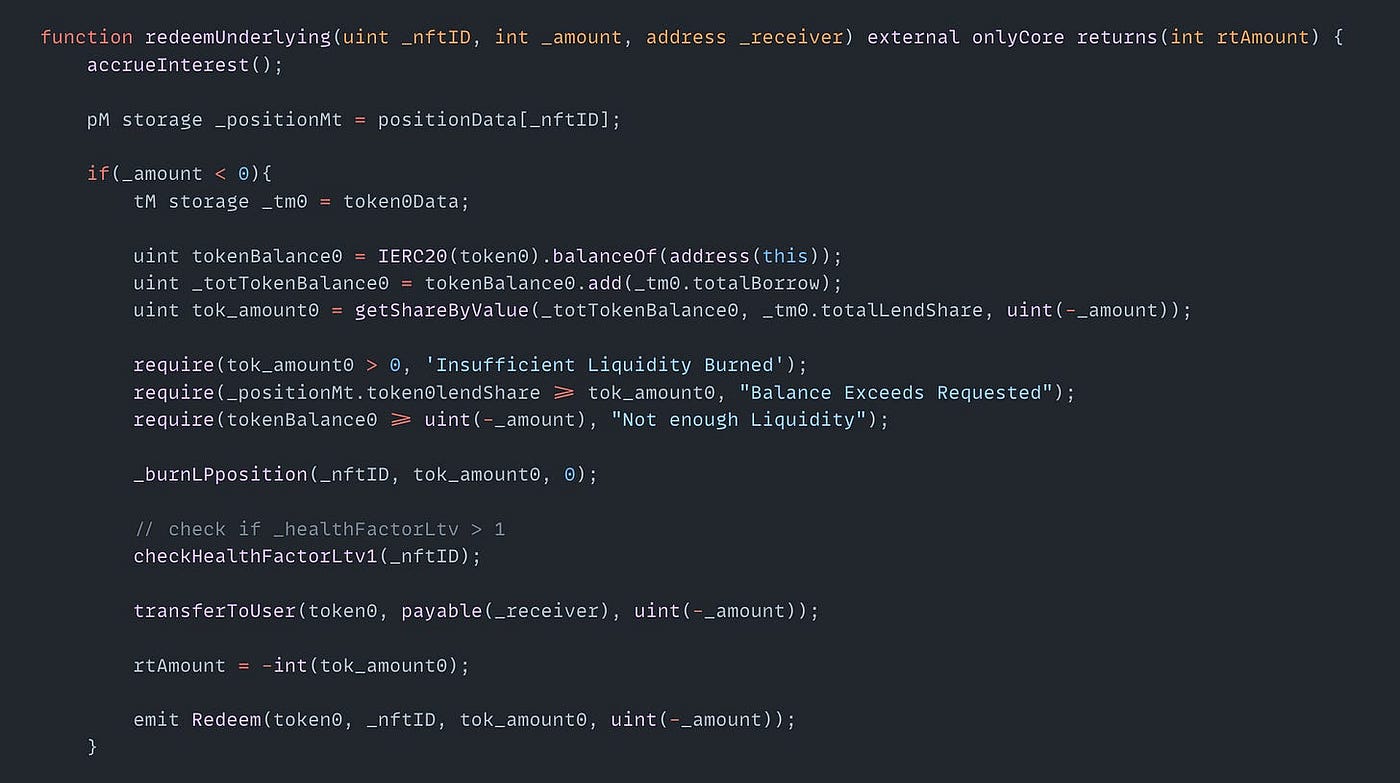
Exploited Contract: 0xc86d2555f8c360d3c5e8e4364f42c1f2d169330e
Transaction: 0x44037ffc0993327176975e08789b71c1058318f48ddeff25890a577d6555b6ba
On January 8th, the Orange Finance exploit on the Arbitrum chain resulted in a $830K loss due to a private key compromise and misconfigured multi-sig vaults. Approximately $783K of the loss came from drained deposits, while $47K was due to excessive token approvals. The stolen assets included funds from Uniswap, PancakeSwap, and Sushi liquidity pools. The Orange Finance team paused deposits and withdrawals, secured 50% of the remaining TVL on Stryke, and initiated recovery efforts with Seal 911.
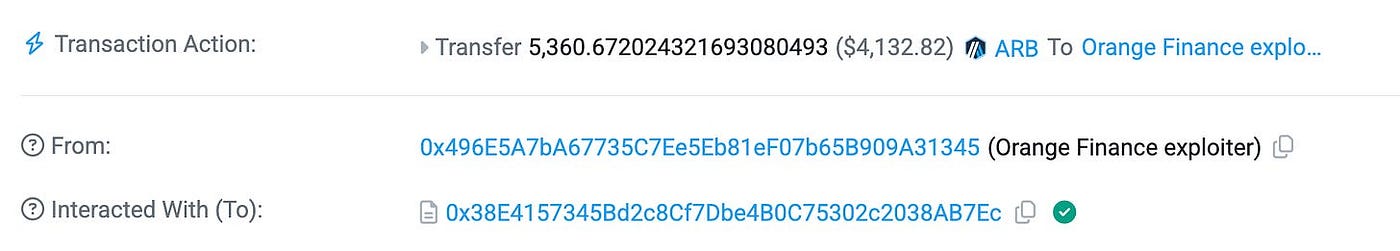
Exploited Contract (on Arbitrum): 0x38E4157345Bd2c8Cf7Dbe4B0C75302c2038AB7Ec
Transaction: 0x093673927fc38783d37717b4bd14693c29035fceff6a0c7747db21e88c4ea28f
On December 10th, the Labubu Token on the BSC resulted in a $11.9K loss. The root cause of the exploit was that the private _transfer() function allowed the attacker to use the same address as both the sender and recipient. While the sender’s balance was reduced during the transfer, the recipient’s balance was incorrectly updated by adding the transferred amount to the initial balance, effectively overriding the reduction. This allowed the attacker to repeatedly execute transfers, artificially inflating their token balance with each iteration.

Exploited Contract (on BNB): 0x2ff960f1d9af1a6368c2866f79080c1e0b253997
Transaction: 0xb06df371029456f2bf2d2edb732d1f3c8292d4271d362390961fdcc63a2382de