
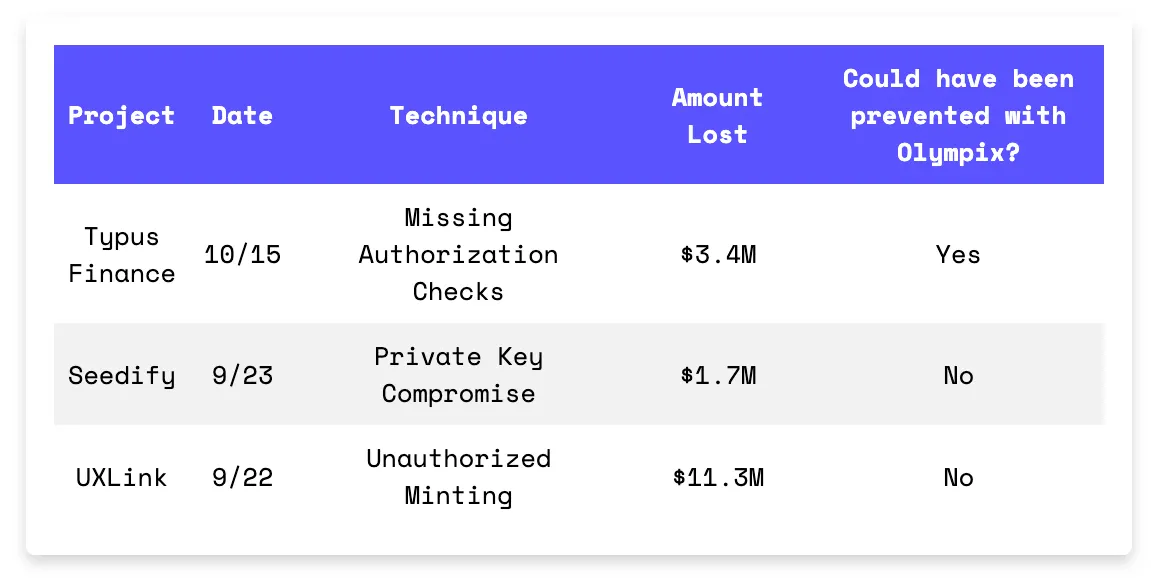
No auth check. No key hygiene. No mint controls. Three protocols got wrecked by three of the oldest failure modes in DeFi. Typus let anyone write to its oracle. Seedify leaked its remote config keys. UXLink handed out mint rights like coupons. This isn’t about complexity. It’s about discipline.
On October 15th, the Typus Finance exploit on the Sui blockchain resulted in a $3.44M loss. The root cause of the exploit was a missing authorization check in the oracle contract’s update_v2() function. This allowed unauthorized addresses to manipulate oracle price feeds without validation. The attacker updated oracle prices to artificially inflate asset values within the TLP contract. By manipulating these prices, they drained 588K SUI, 1.6M USDC, 0.6 xBTC, and 32K suiETH from the liquidity pool.
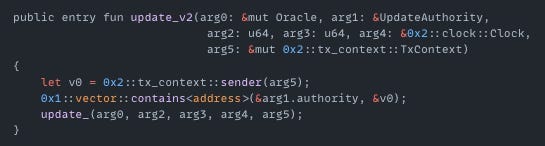
Exploited Contract (on Sui): 0xaf44818c67a878b9eba0c63186b00e80d9fc3d1e2ae02f00fa3993b0e683bff3
Transaction: 6KJvWtmrZDi5MxUPkJfDNZTLf2DFGKhQA2WuVAdSRUgH
On September 13th, the Seedify exploit across multiple chains resulted in a $1.7M loss due to a private key compromise. The attacker gained unauthorized control of the SFUND_OFTv1 contract and called the setTrustedRemoteAddress() function to configure a malicious contract as the trusted remote address. This allowed the attacker to mint SFUND tokens and make a profit.

Exploited Contract (on Base): 0x633E254585aDE6E9d40d2A4B8CC2F3769B94cb48
Transaction: 0x1dd7c101c18cd1adc80c4c68ce480862245a7223f8e5182136aed316eae54ac9
On September 23rd, the UXLink exploit on the Arbitrum chain resulted in an $11.3M loss due to unauthorized token minting. The root cause of the exploit was that the attacker gained access to minting privileges and created new UXLINK tokens outside the protocol’s whitepaper specifications. According to the UXLink team, major centralized exchanges froze the majority of the hacker’s assets and limited the damage.
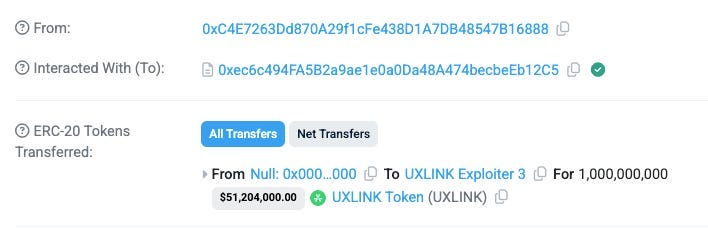
Transaction: 0x35edac40767f65d4d1382f0f55cda2f4db321313e16fe059079f0113f9cb5696