

On December 21st, the Trust Wallet exploit resulted in a $7M loss due to a Chrome extension hack. According to the developers, the attacker injected malicious code to redirect user data through the PostHog library to a malicious server. Trust Wallet acknowledged the incident and confirmed that only version 2.68 of the Chrome extension was affected. Mobile wallets and other extension versions remained safe.
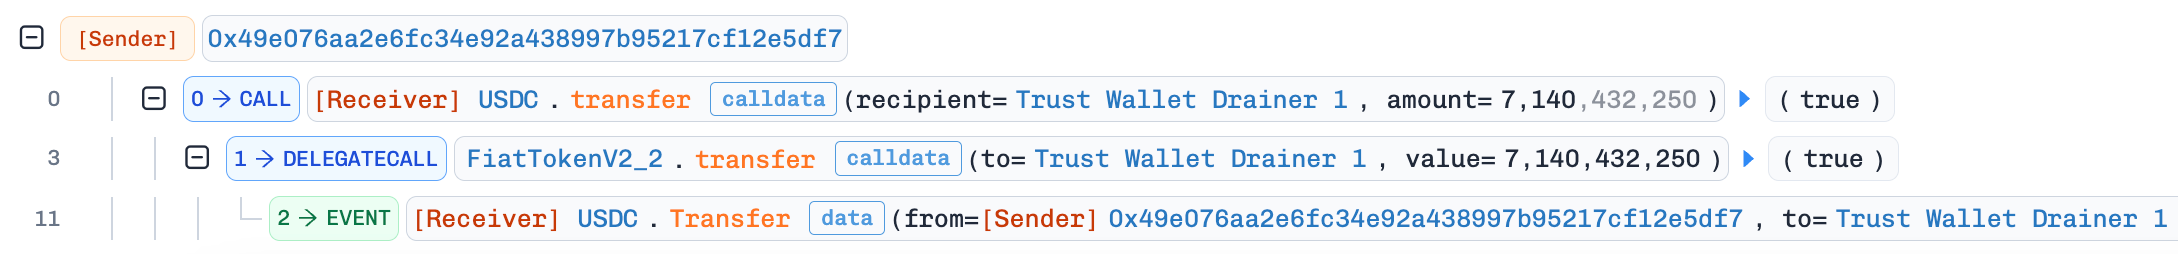
Transaction: 0x7ed83315359deef0acd92bd96320b27dc7d36238bde8d904a67623c2eb43c682
On December 19th, the Port3 exploit on BSC resulted in a $166K loss. The root cause of the exploit was a logic error that allowed the attacker to mint PORT3 tokens. The attacker called the registerChain() function with an invalid signature. Port3 had renounced token ownership, so owner() was set to address(0). Inside onlyOwnerOrOwnerSignature, verifySignature called ecrecover to validate the attacker’s signature. ecrecover returned address(0) because the signature was invalid. The code checked if recovered == authority and since both were address(0), so the check passed. This let the attacker mint 1 billion PORT3 tokens without authorization.
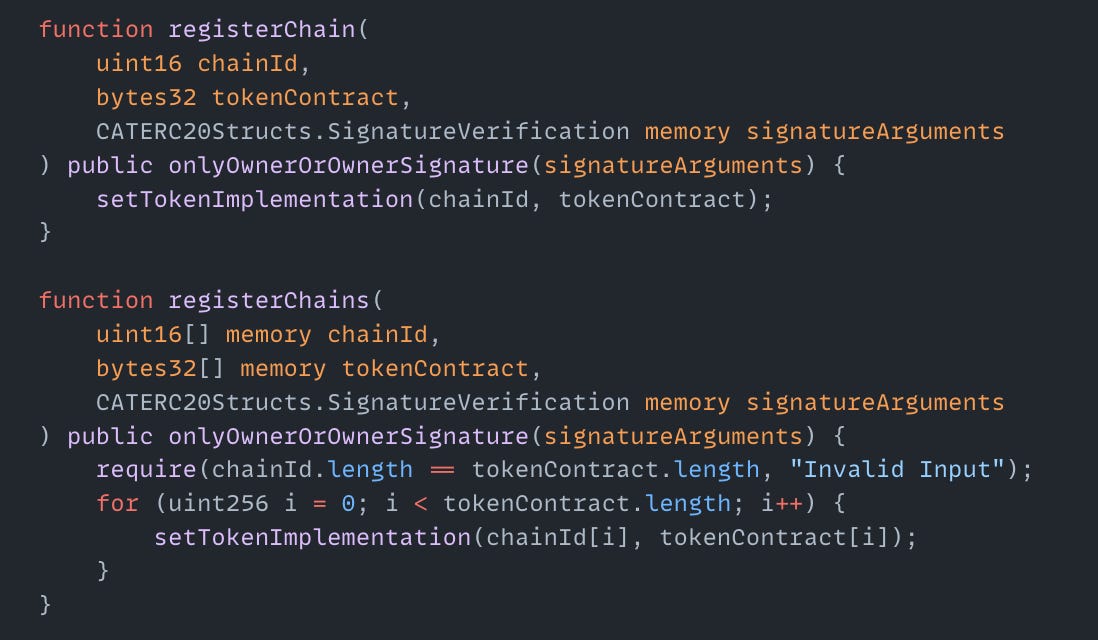
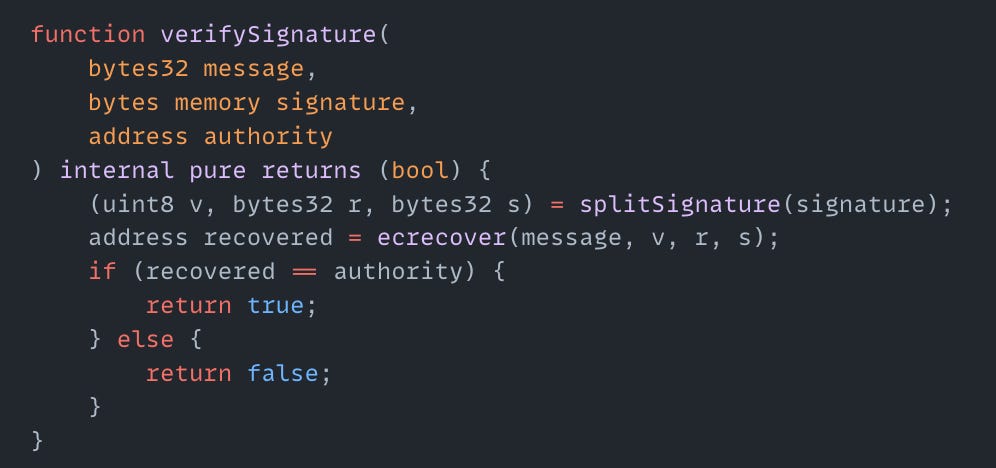
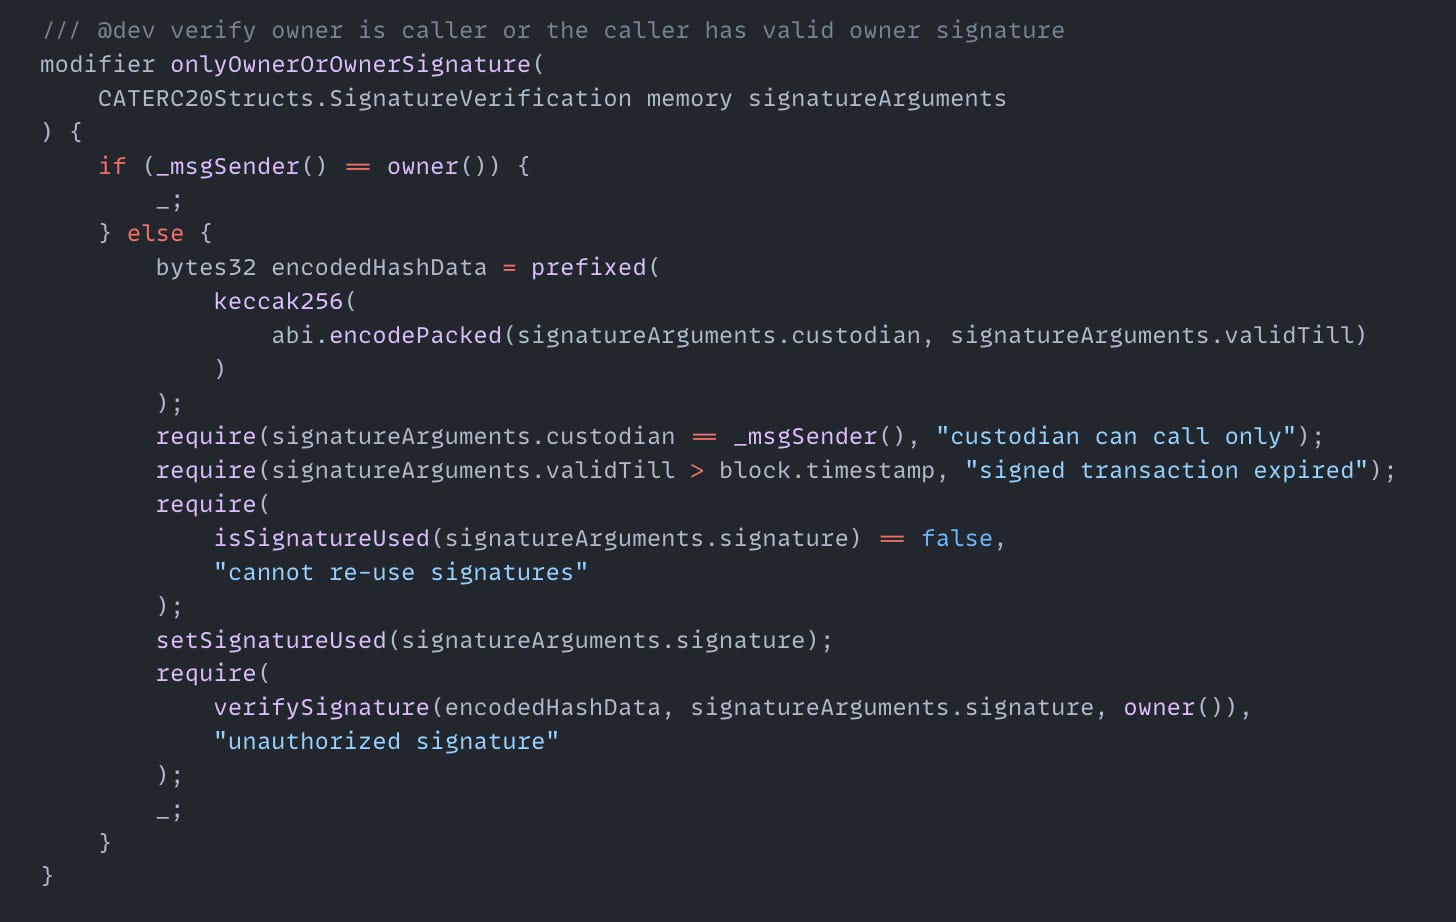
Exploited Contract (BSC): 0xb4357054c3dA8D46eD642383F03139aC7f090343
Transaction (Bridge In): 0xdd493077f364bb112728578018589890489a05e91bb644d2b7a362ea3897a178
Transaction (Register Chain): 0xfaf450571541b95f924024ac3febd5cf6c16695ce787217ca8870350309051c1
On November 20th, the Gana Payment exploit on BSC resulted in a $3.1M loss. The root cause of the exploit was a compromised owner key that gave the attacker control over a delegator contract. Using this access, the attacker drained funds using the staking mechanism. The Gana Payment protocol had launched just nine days earlier on November 11th.
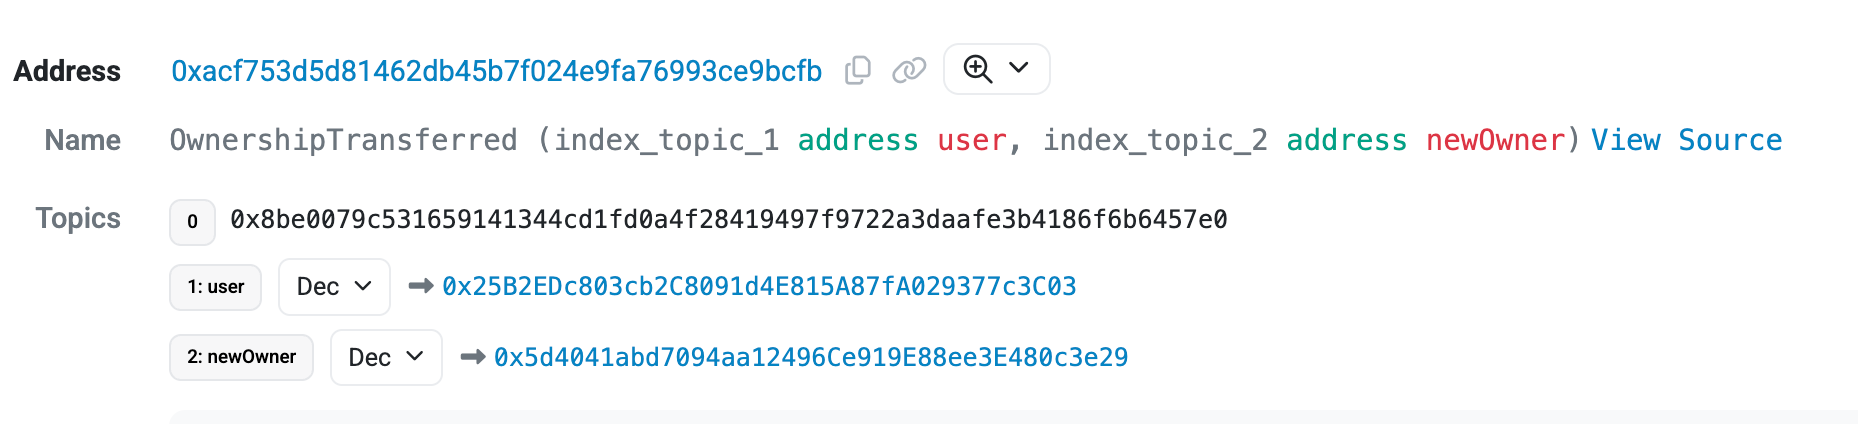
Exploited Staking Contract (BSC): 0xacf753d5d81462db45b7f024e9fa76993ce9bcfb
Transaction: 0x8f909383a91c55282a59a1568a9ca58f7e4a02d26f1918dfc5c641a99bdabda8