
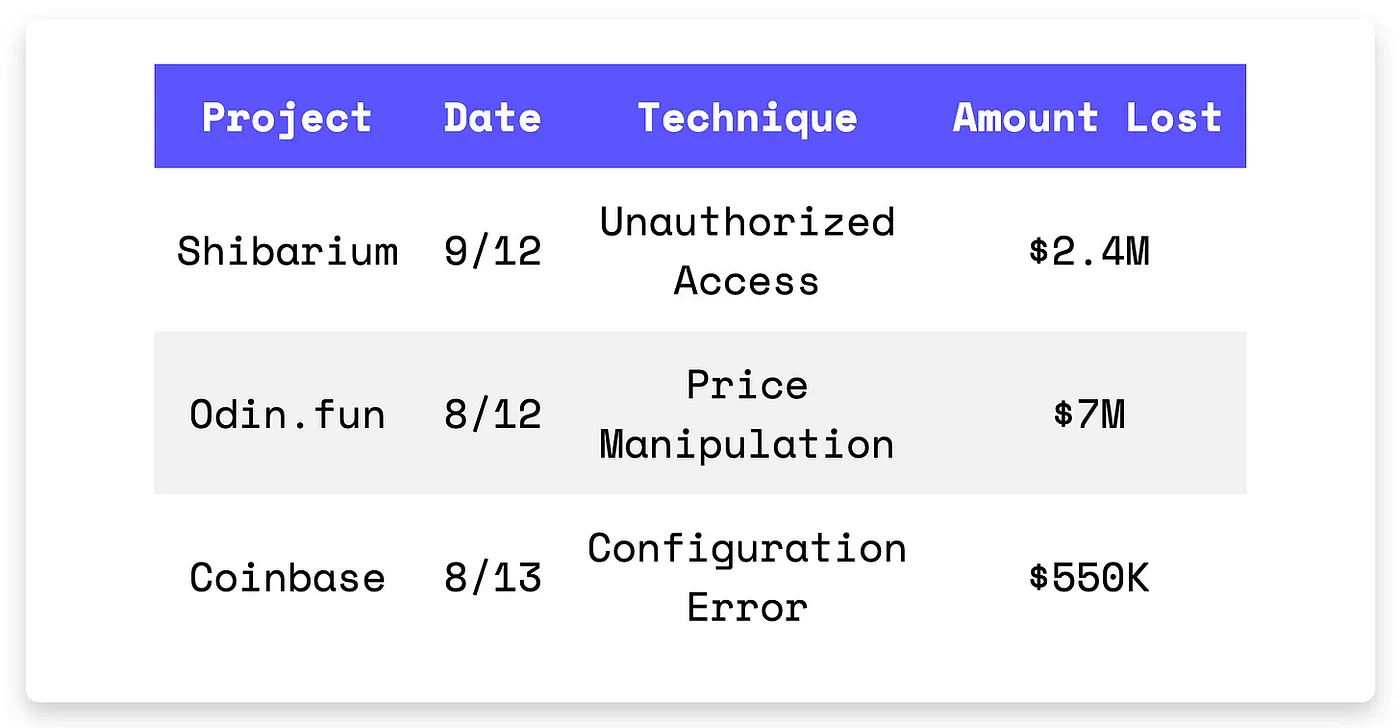
Three wildly different systems, one shared failure mode: unchecked control paths. Shibarium’s validator game was stake-to-steal. Odin.fun forgot that pools lie without oracles. And Coinbase? One misconfigured approval leaked $550K to an MEV bot. Every design makes assumptions — these three just learned what theirs cost.
On September 12th, the Shibarium exploit on the Ethereum mainnet resulted in a $2.4M loss. The root cause of the attack was that the attacker was able to control the majority of the validator signing keys to drain ETH and Shib tokens. The attacker was able to get control of the keys because the validator voting power on the network is determined by the amount of BONE token staked. By staking 4.6M BONE tokens, the attacker gained the validator control and was able to execute the withdrawals.

Transaction #1: 0xe882a83afb92d6070b848ef025ae699ec043b7c2f31b21d2a08c94306f9b817e
Transaction #2: 0x6df7dcb5dac11355926abf2d9490af031619900de2e202dc780765222101007a
On August 12th, the Odin.fun exploit resulted in a $7M loss due to a price manipulation attack. The attacker first deposited SATOSHI tokens into the BTC pool. Then traded those tokens against Bitcoin in the same pool. Because the pool priced assets only by the ratio of tokens inside it (with no external price checks), every swap reduced the visible BTC share and made SATOSHI tokens appear more valuable. The attacker then removed their liquidity and made a profit. The attacker later manipulated the ODINPEPE price as well.
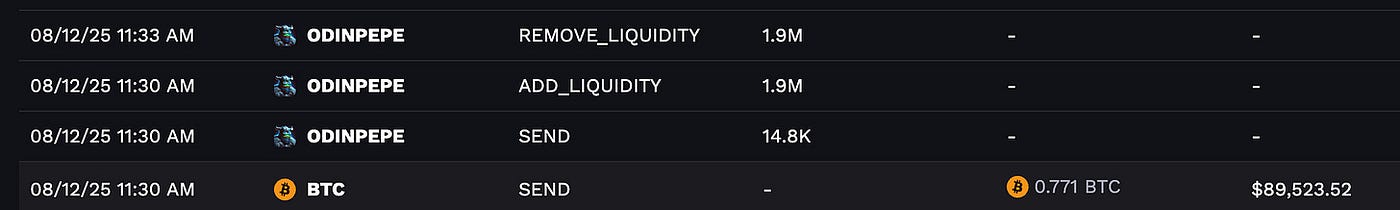
List of Transactions: https://odin.fun/user/urguz-m32zo-jlld6-pyy4l-z3c24-jv4pt-5fmll-gq2xd-6siiz-oxkao-xae?tab=activity
On August 13th, the Coinbase exploit on the Ethereum mainnet resulted in a $550K. The root cause of the exploit was a configuration error where Coinbase’s Fee wallet mistakenly granted ERC-20 approvals to 0x’s Mainnet Settler contract, a permissionless executor. An MEV bot detected the approvals and immediately called the Settler contract to drain tokens. The bot later swapped the stolen assets through Uniswap routes into ETH.

Exploited Contract: 0x382ffce2287252f930e1c8dc9328dac5bf282ba1
Transaction: 0xc1fde1d472dc682bd68c4dff005d50b360c8f8fba491c636388a25b5757e3abb