

On December 12th, the Ribbon Finance exploit on Ethereum mainnet resulted in a $2.7M loss. The root cause of the exploit was a lack of protection for the upgradeable oracle price-feed proxies. An attacker gained control of the proxy admin and replaced the price-feed implementations with a malicious contract. The attacker set arbitrary expiry prices for wstETH, AAVE, LINK, and WBTC. This caused options to settle at artificially inflated prices and allowed the attacker to make a profit.
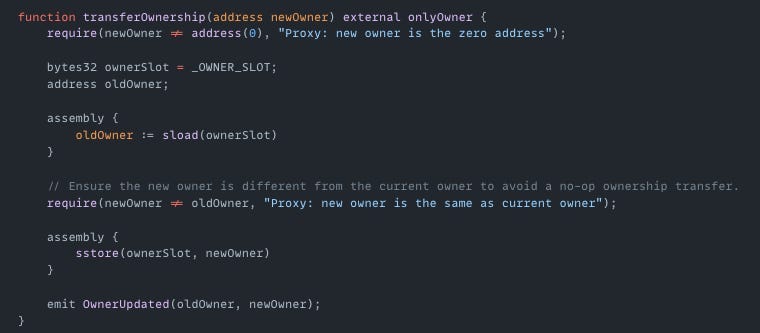
Exploited Contract: 0x9D7b3586f361e3621Bf4F099cBC9d155e8ae6B76
Transaction: 0xb73e45948f4aabd77ca888710d3685dd01f1c81d24361d4ea0e4b4899d490e1e
On December 10th, the Rari Capital exploit on the Ethereum mainnet resulted in a $2M loss. The root cause was unauthorized access to the cERC20 implementation contract. The attacker was able to borrow without triggering collateral checks. The attacker repeated these borrow operations across multiple transactions and drained liquidity from the lending pools.
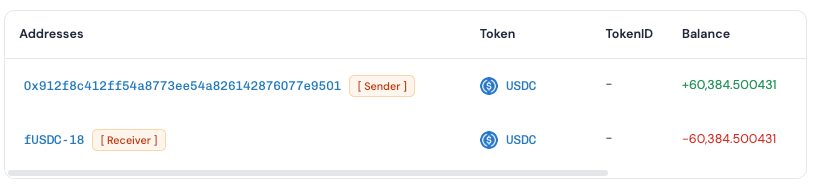
Exploited Contract: 0x67db14e73c2dce786b5bbbfa4d010deab4bbfcf9
Transaction: 0x88902bd42ef8186d457ea0462f6b352e306ea8486e92b0fcf716318904f9869e