
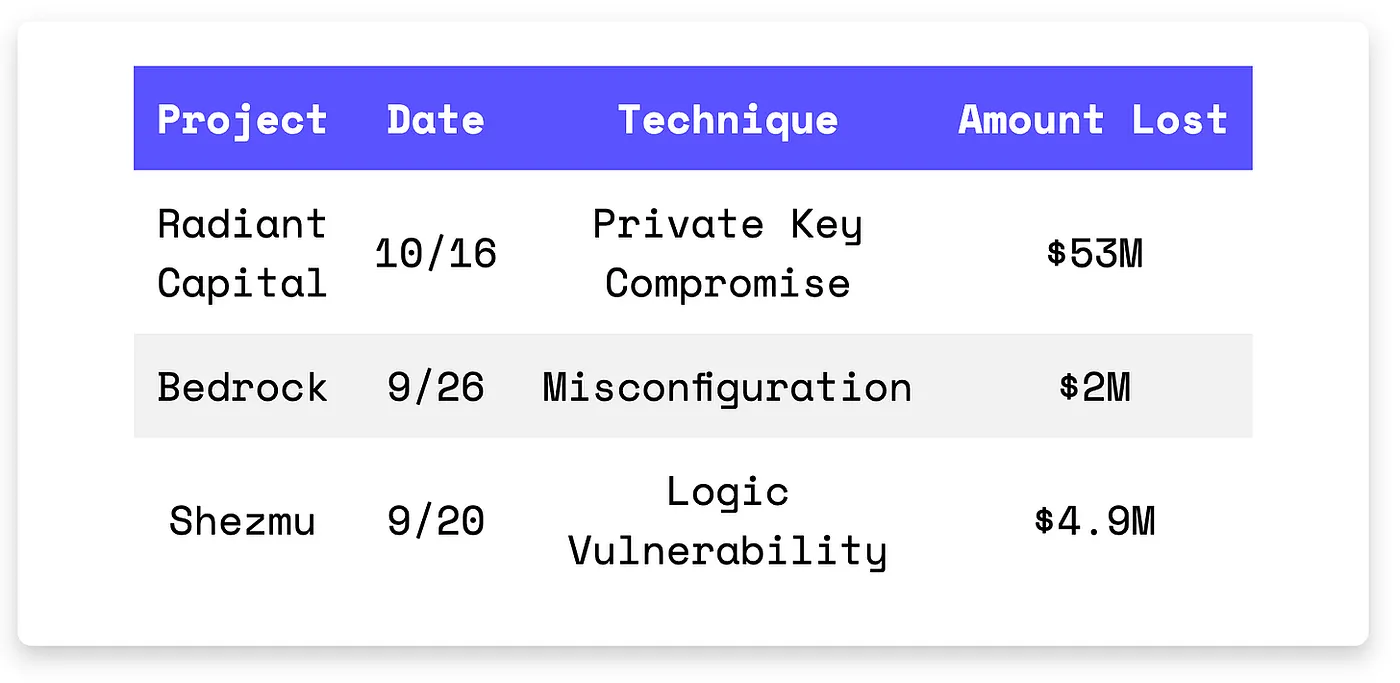
Radiant lost $53M after lax multisig thresholds exposed private keys. Bedrock mishandled native BTC logic, enabling unauthorized minting of 30.8 uniBTC. Shezmu’s vault let users mint ShezUSD without collateral, leading to a $4.9M drain.
On October 16th, the Radiant Capital exploit across multiple chains resulted in a $53M loss. The root cause of the attack was the compromise of their private keys. Although Radiant Capital’s wallet can require up to 11 signatures, the setup at the time of the exploit allowed transactions to be executed with just 3 signatures. The Radiant Capital team acknowledged the incident and confirmed that markets on Base and Mainnet are paused until further notice.
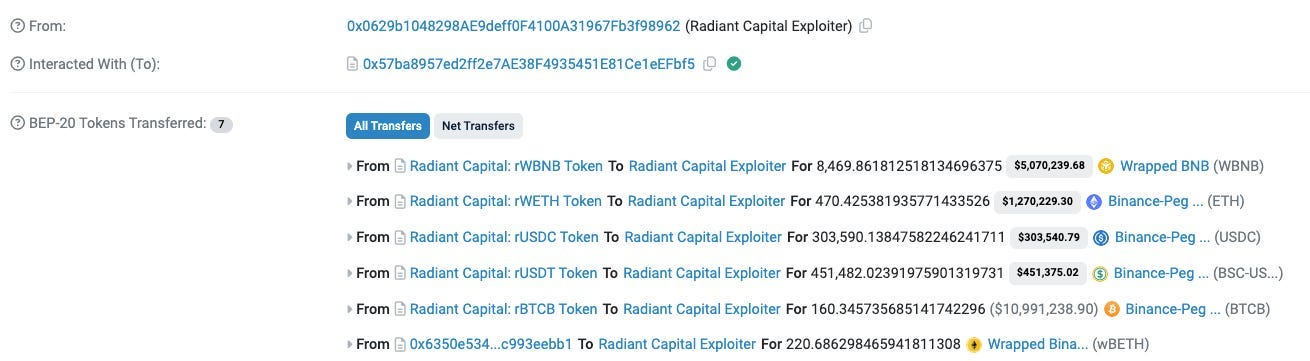
Exploited Contract (on BNB): 0x58b0bb56cfdfc5192989461dd43568bcfb2797db
Transaction Hash: 0xd97b93f633aee356d992b49193e60a571b8c466bf46aaf072368f975dc11841c
On September 26th, the Bedrock exploit on the Ethereum Mainnet resulted in a $2M loss. The root cause was a flaw in the contract’s handling of native BTC tokens on non-native chains. The mint function failed to account for the absence of native BTC registration, causing the total supply check to pass incorrectly. The attacker was able to mint 30.8 uniBTC with native tokens. Bedrock acknowledged the incident and paused all transactions.
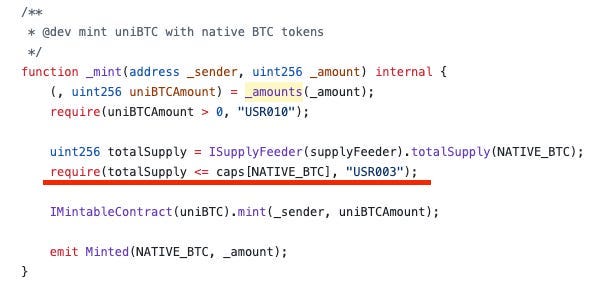
Exploited Contract: https://github.com/Bedrock-Technology/uniBTC/blob/main/contracts/contracts/Vault.sol
Transaction Hash: 0x725f0d65340c859e0f64e72ca8260220c526c3e0ccde530004160809f6177940
On September 20th, the Shezmu exploit on the Ethereum Mainnet resulted in a $4.9M loss. The root cause of the exploit was that one of Shezmu’s vault contracts allowed minting ShezUSD without providing any collateral. This vulnerability allowed the attacker to mint ShezUSD tokens and make a profit. Shezmu acknowledged the issue and recovered the stolen funds from the attacker in exchange for a 20% bounty.
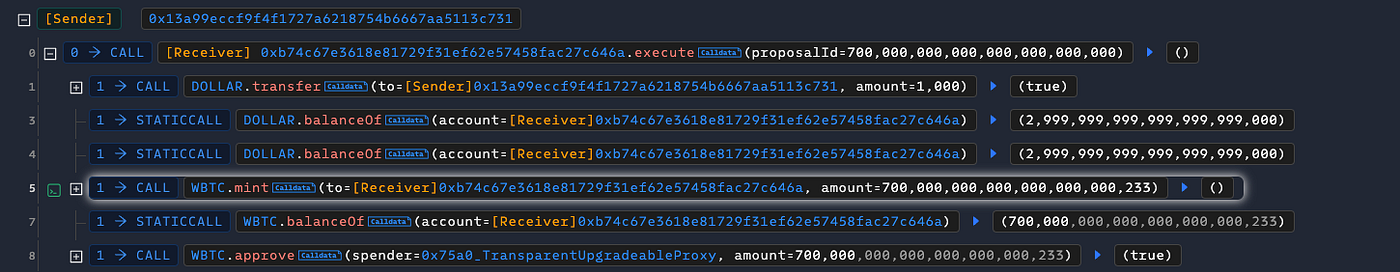
Exploited Contract: 0xEd4B3d468DEd53a322A8B8280B6f35aAE8bC499C
Transaction Hash: 0xf68a65993bbd543a03e0e4df5a4351aee91ff43794c5878c24e37df40c3fa398