
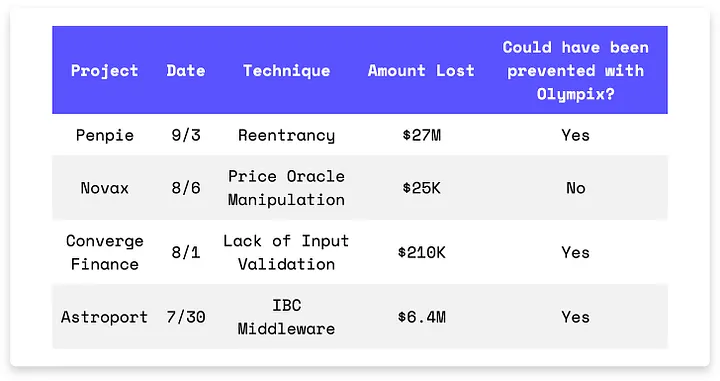
Penpie lost $27M after missing a reentrancy guard in its reward harvesting logic. Converge Finance was exploited for $210K through a malicious contract injected into its staking claims. Astroport suffered a $6.4M reentrancy attack via reintroduced IBC hook vulnerabilities. Novax lost $25K after its liquidity-based oracle was manipulated.
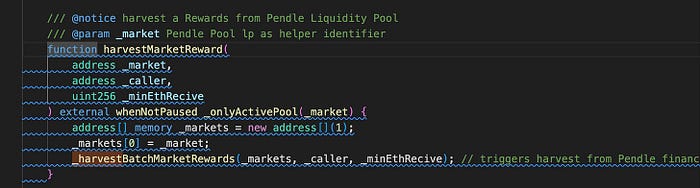
On September 3rd, the Penpie exploit on the Ethereum Mainnet resulted in a $27M loss due to a reentrancy vulnerability. The root cause of the exploit was the missing reentrancy protection in the _harvestBatchMarketRewards() function of the PendleStakingBaseUpg contract. The attacker manipulated the token balance checks used for reward distribution. By depositing additional tokens mid-process, the attacker inflated the post-reward balance, allowing them to withdraw additional rewards.

Exploit Contract: 0x61f1e52587377d398c90b36a4d387ff264e10677
Transaction Hash: 0x7e7f9548f301d3dd863eac94e6190cb742ab6aa9d7730549ff743bf84cbd21d1
On August 6th, the Novax exploit on the BNB chain resulted in a $25K loss. The root cause of the exploit was that the protocol’s price oracle could be manipulated because it calculated token prices based on liquidity. The attacker used flash loans and increased the USDT liquidity. The oracle calculated Novax token prices using the ratio of USDT to BUSD. By inflating the USDT liquidity temporarily, the attacker artificially increased the price of Novax tokens, allowing the attacker to make a profit.

Exploit Contract (on BNB): 0x55c9eebd368873494c7d06a4900e8f5674b11bd2
Transaction Hash: 0xb1ad1188d620746e2e64785307a7aacf2e8dbda4a33061a4f2fbc9721048e012
On August 1st, the Converge Finance exploit on the Ethereum Mainnet resulted in a $210K loss. The root cause of the exploit was the lack of validation in the claimContracts parameter within the claimMultipleStaking() function. The attacker injected a malicious contract into the claimContracts parameter, which allowed them to manipulate the cvgClaimable variable. This manipulation led to the minting of 58M CVG tokens.

Exploit Contract: 0x47c69e8c909ce626af73c955a5e34a20b7c71f19
Transaction Hash: 0x636be30e58acce0629b2bf975b5c3133840cd7d41ffc3b903720c528f01c65d9
On July 30th, the Astroport exploit on the Terra Network resulted in a $6.4M loss due to a reentrancy vulnerability linked to Inter-Blockchain Communication (IBC) hooks. The vulnerability, previously patched in April, was accidentally reintroduced during a June upgrade. The attacker exploited this by deploying a malicious contract and triggering IBC transfer timeouts, allowing them to repeatedly reenter the contract and drain funds. The losses included 60M ASTRO, 3.5M USDC, 5K USDT, and 2.7 BTC. Terra Network halted all transactions for emergency upgrades.

Exploit Contract (on Terra Network): terra18plp90j0zd596zt3zdsf0w9vvk5ukwlwzwkksxv9mdu8rscat9sqndk5qz
Transaction Hash: 4F260BFD0D9357859A186D1EDD9CF6CEDF4EA521D1595CB7823DE22D6084DDA0