

On February 15th, the Moonwell exploit on Base and Optimism resulted in a $1.8M loss. The root cause was a misconfigured oracle introduced through Moonwell’s MIP-X43 update. The cbETH/USD price was calculated using only the cbETH/ETH exchange rate, without multiplying by the ETH/USD feed. This caused cbETH to be priced at roughly $1.12 instead of around $2,200. Liquidation bots exploited the mispricing, leaving Moonwell with $1.8M bad debt.
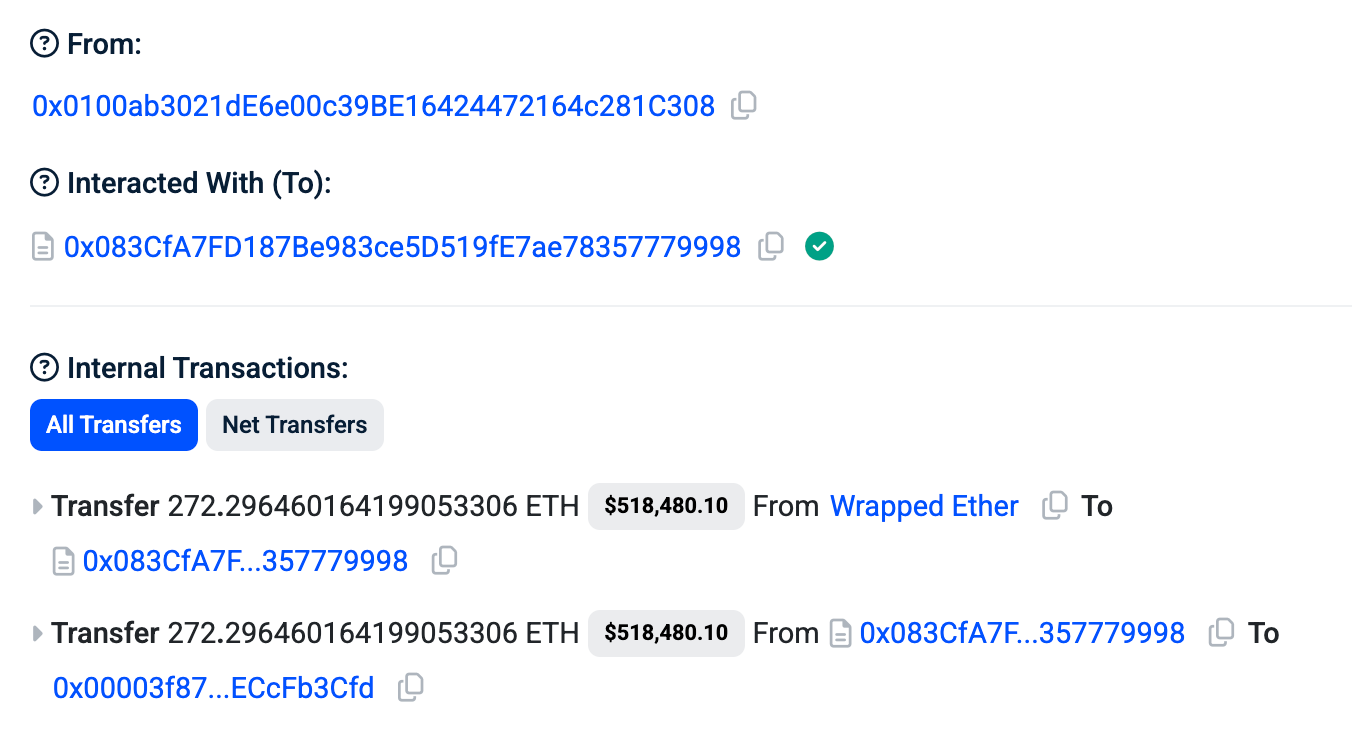
Exploited Contract (on Base): 0x2ae3f1ec7f1f5012cfeab0185bfc7aa3cf0dec22
Transaction: 0x2f4ff77c77ce2a52c80fcd59a4cac4b05f4285afe1f3b92118b0a004a325953c
On January 8th, the Truebit exploit on the Ethereum mainnet resulted in a $26.6M loss. The root cause was an integer overflow in the getPurchasePrice() function. The function computes token price via (v12 + v9) / v6, where both v12 and v9 were values close to the uint256 maximum. Their sum overflowed back to near zero, causing the division to return 0. Since the getPurchasePrice() function returned zero, the attacker was able to mint 240 million TRU tokens at no cost.
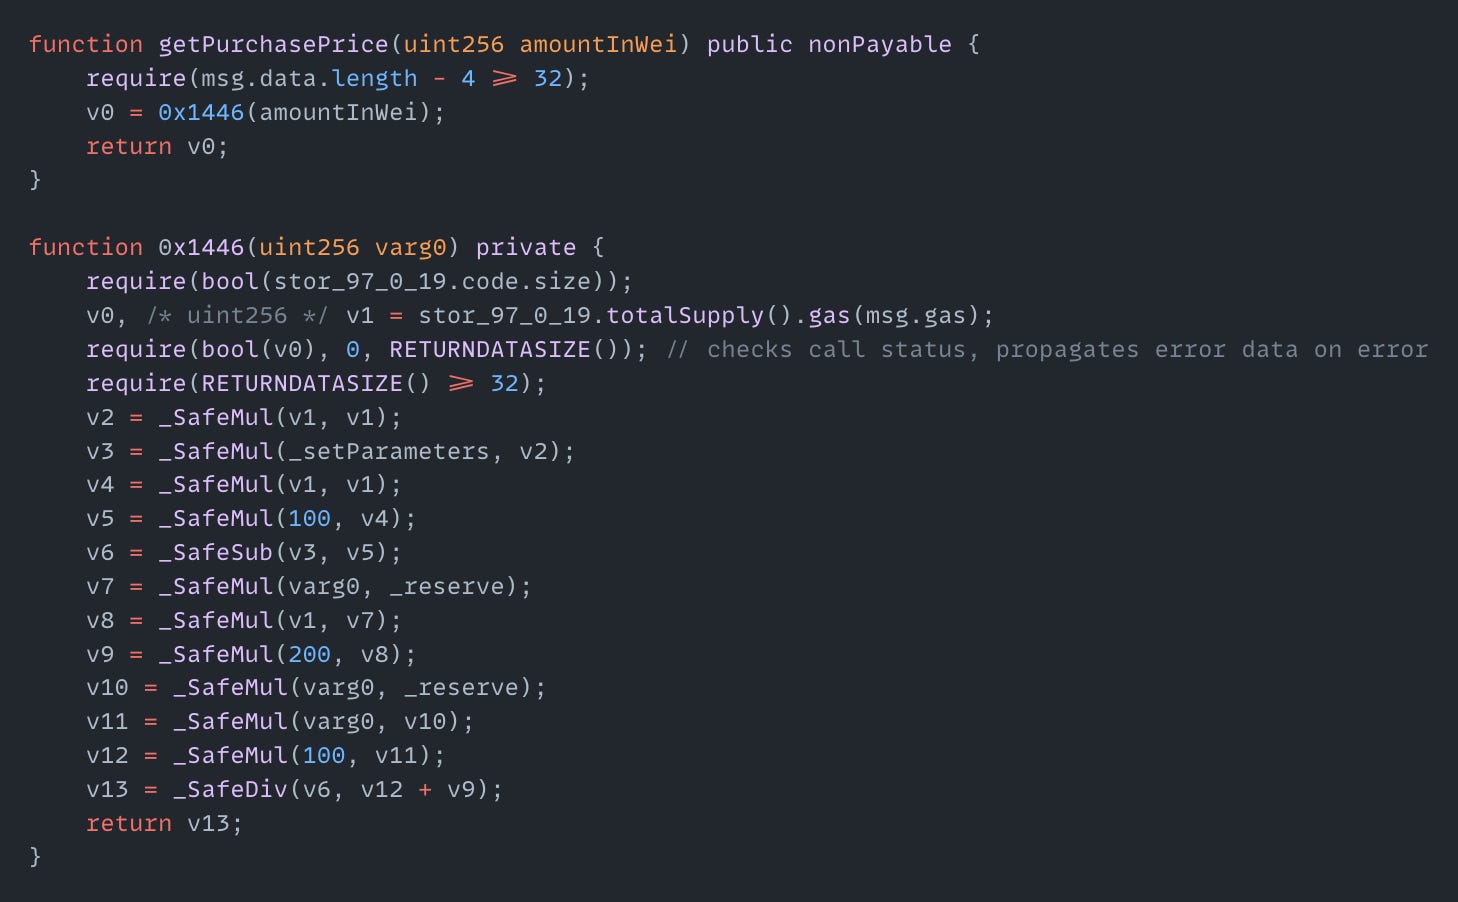
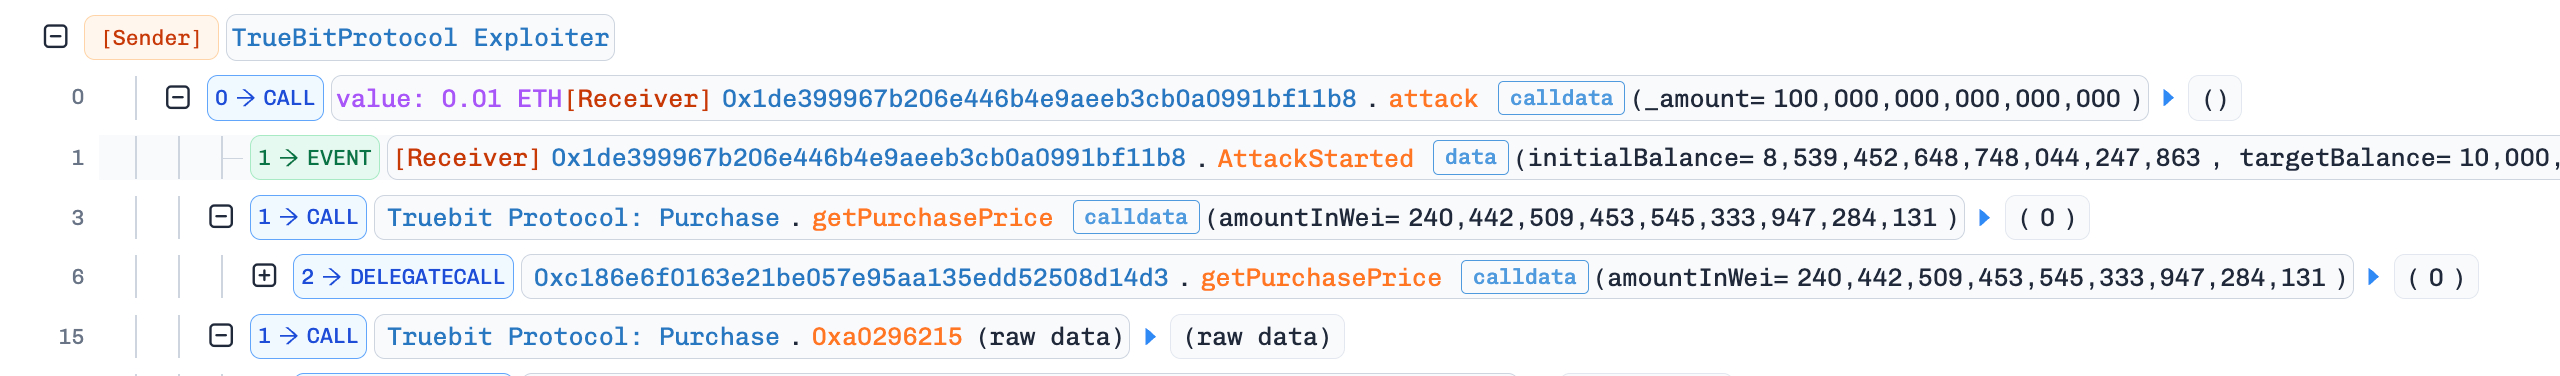
Exploited Contract: 0xc186e6f0163e21be057e95aa135edd52508d14d3
Transaction: 0xcd4755645595094a8ab984d0db7e3b4aabde72a5c87c4f176a030629c47fb014
On December 29th, the MSCST exploit on BSC resulted in a $130K loss. The root cause was a price manipulation vulnerability. The attacker flash loaned 46.8M GPC tokens and deposited them into the GPC/WBNB PancakeSwap pool, artificially manipulating the GPC price. The attacker repaid the flash loan within the same transaction and made 149 BNB in profit.
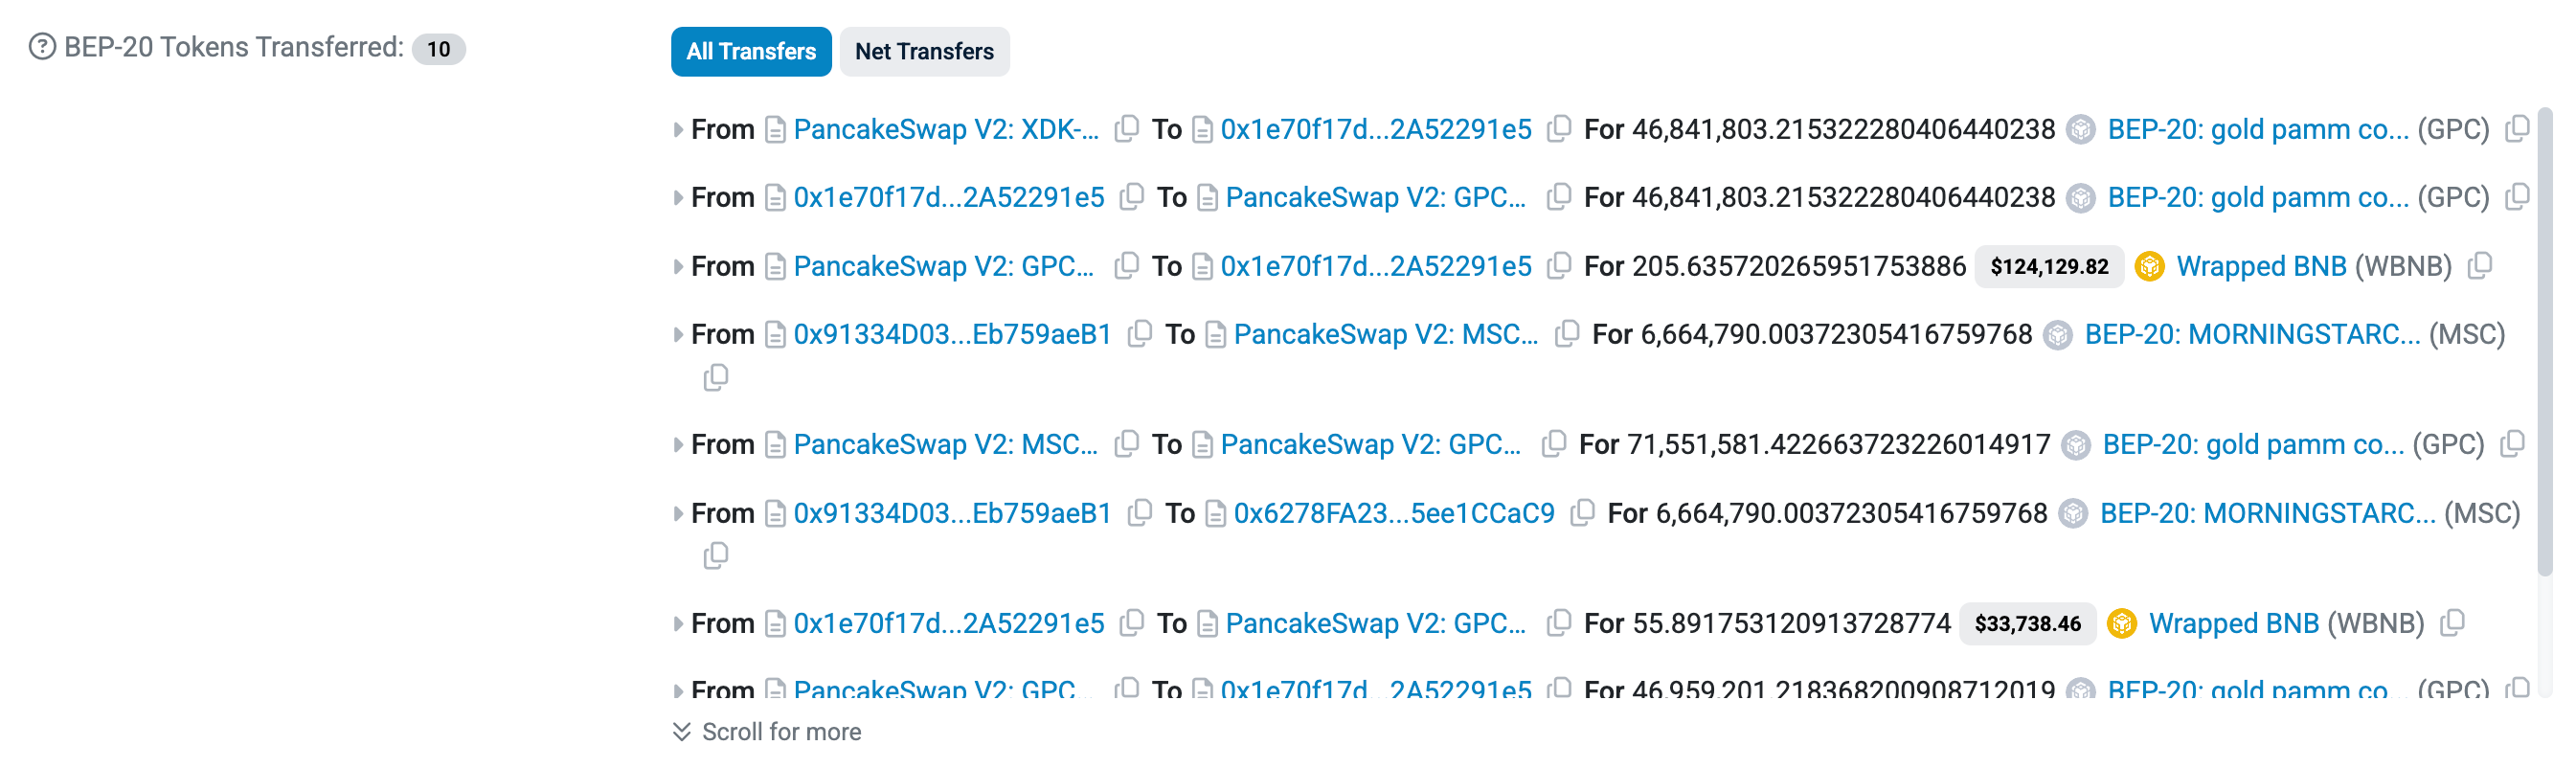
Transaction (BNB): 0x6c9ed4c2d81b6abfdf297b0cbc13585ed91f2a5e69e3545d3ea4316f50021b56