
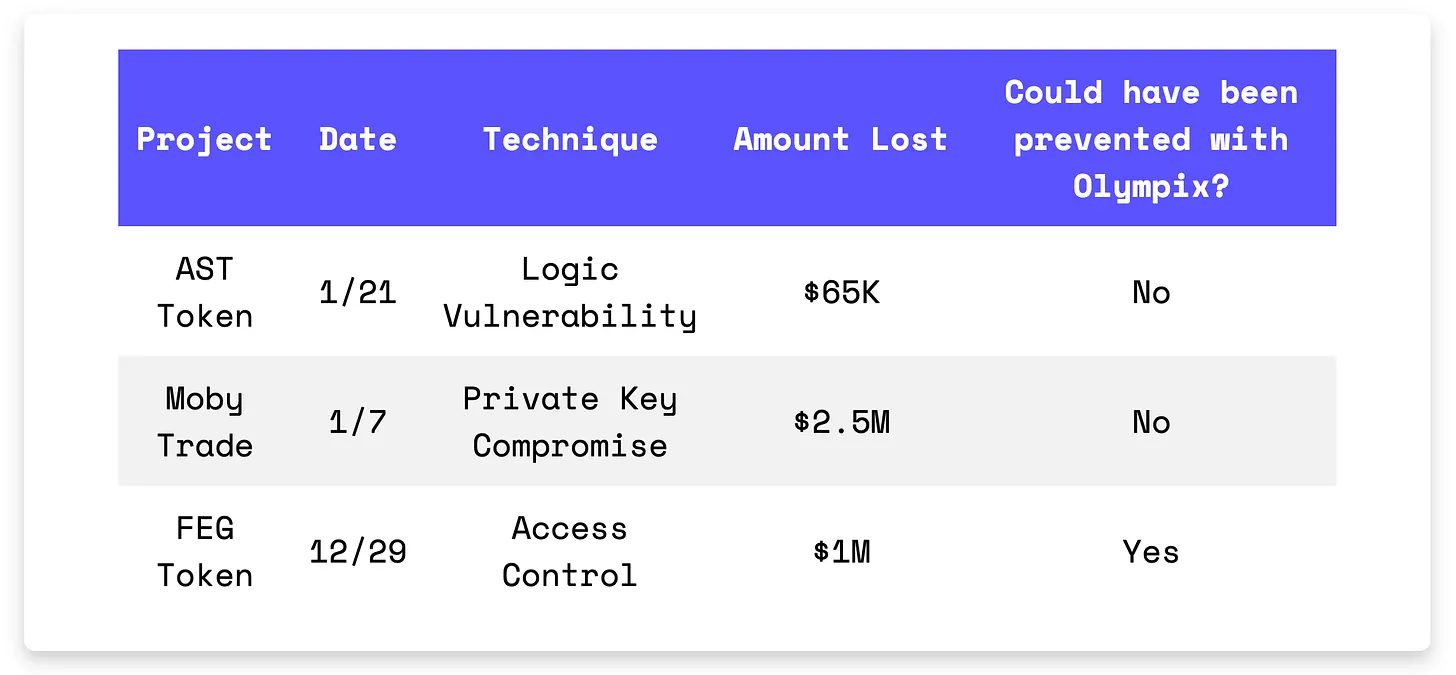
Moby Trade lost $2.5M after a private key compromise let attackers upgrade vault contracts. FEG was drained for $1M when an attacker self-whitelisted in a relayer contract with no access control. AST Token was hit for $65K through price manipulation via reserve burns in the transfer logic.
On January 21st, the AST token exploit on the Binance Smart Chain resulted in a $65K loss due to a price manipulation vulnerability. The attacker exploited the private _transfer() function which burned AST tokens from the liquidity pool. This caused the AST reserves in the pool to drop significantly, artificially inflating its price. The attacker then swapped AST tokens for USDT at the manipulated price and made a profit.
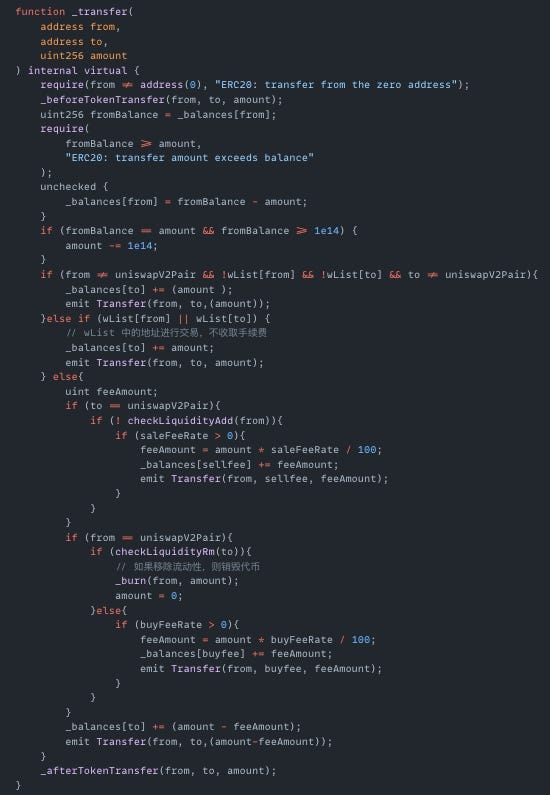
Exploited Contract (on BSC): 0xc10e0319337c7f83342424df72e73a70a29579b2
Transaction: 0x80dd9362d211722b578af72d551f0a68e0dc1b1e077805353970b2f65e793927
On January 8th, the Moby Trade exploit on the Arbitrum chain resulted in a $2.5M loss due to a private key compromise. The attacker gained control of proxy admin keys and upgraded vault contracts to withdraw assets. The attack targeted Moby Trade’s S_VAULT and M_VAULT. A white hat team from SEAL911 intervened to rescue $1.47M USDC. The Moby Trade team has acknowledged the incident and started investigations.
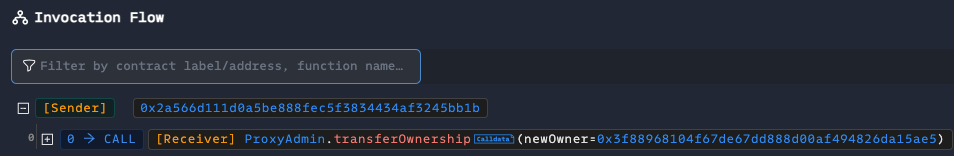
Ownership Transfer Transaction (on Arbitrum): 0x9da34da770f1e9c5d5e176578b32710d8e288587d8401582f34a9631edf9be4b
Funds Transfer Transaction: 0xfb260f58332034fe203a41b031c41b8461f469e46d5632b33b328f22aed1fb42
On December 29th, the FEG Token exploit on the Binance Smart Chain resulted in a $1M loss. The root cause of the exploit was missing access controls in the relayer’s whitelist function. The attacker added their contract to the whitelist without verification and set a withdrawable balance. The attacker withdrew the tokens without depositing any on the source chain and swapped them for BNB.
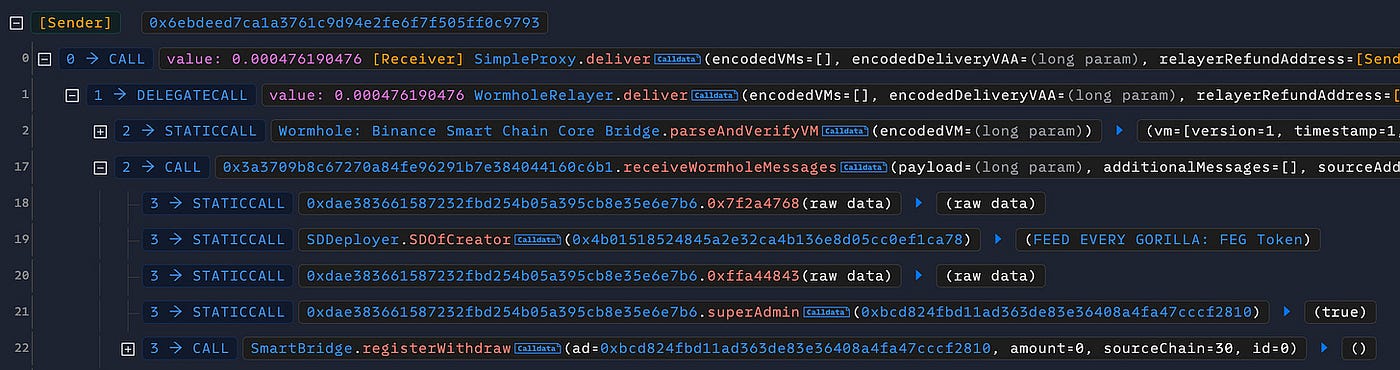
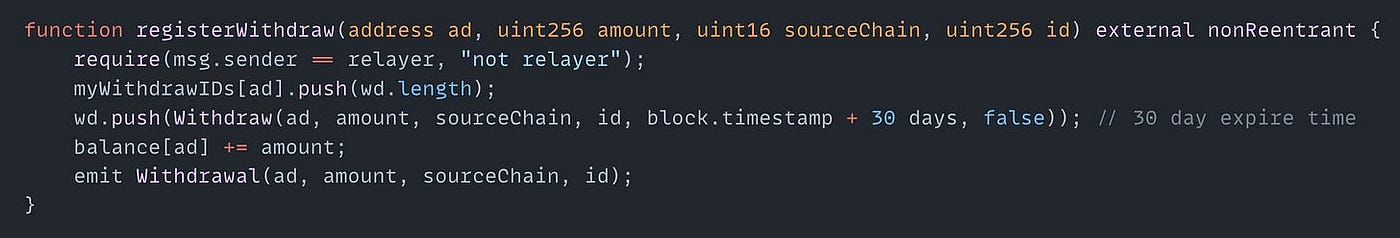
FEG Relayer Contract (unverified, on BSC): 0x3A3709b8c67270A84Fe96291B7E384044160C6b1
SmartBridge Contract (for withdrawal): 0x8d5c8D2856d518A5Edc7473a3127341492B56243
Transaction: 0x7e448bbf1566c20b6973d2cbdb49092d5c6fca90ad7f1a1fc4b102e8095899d2