
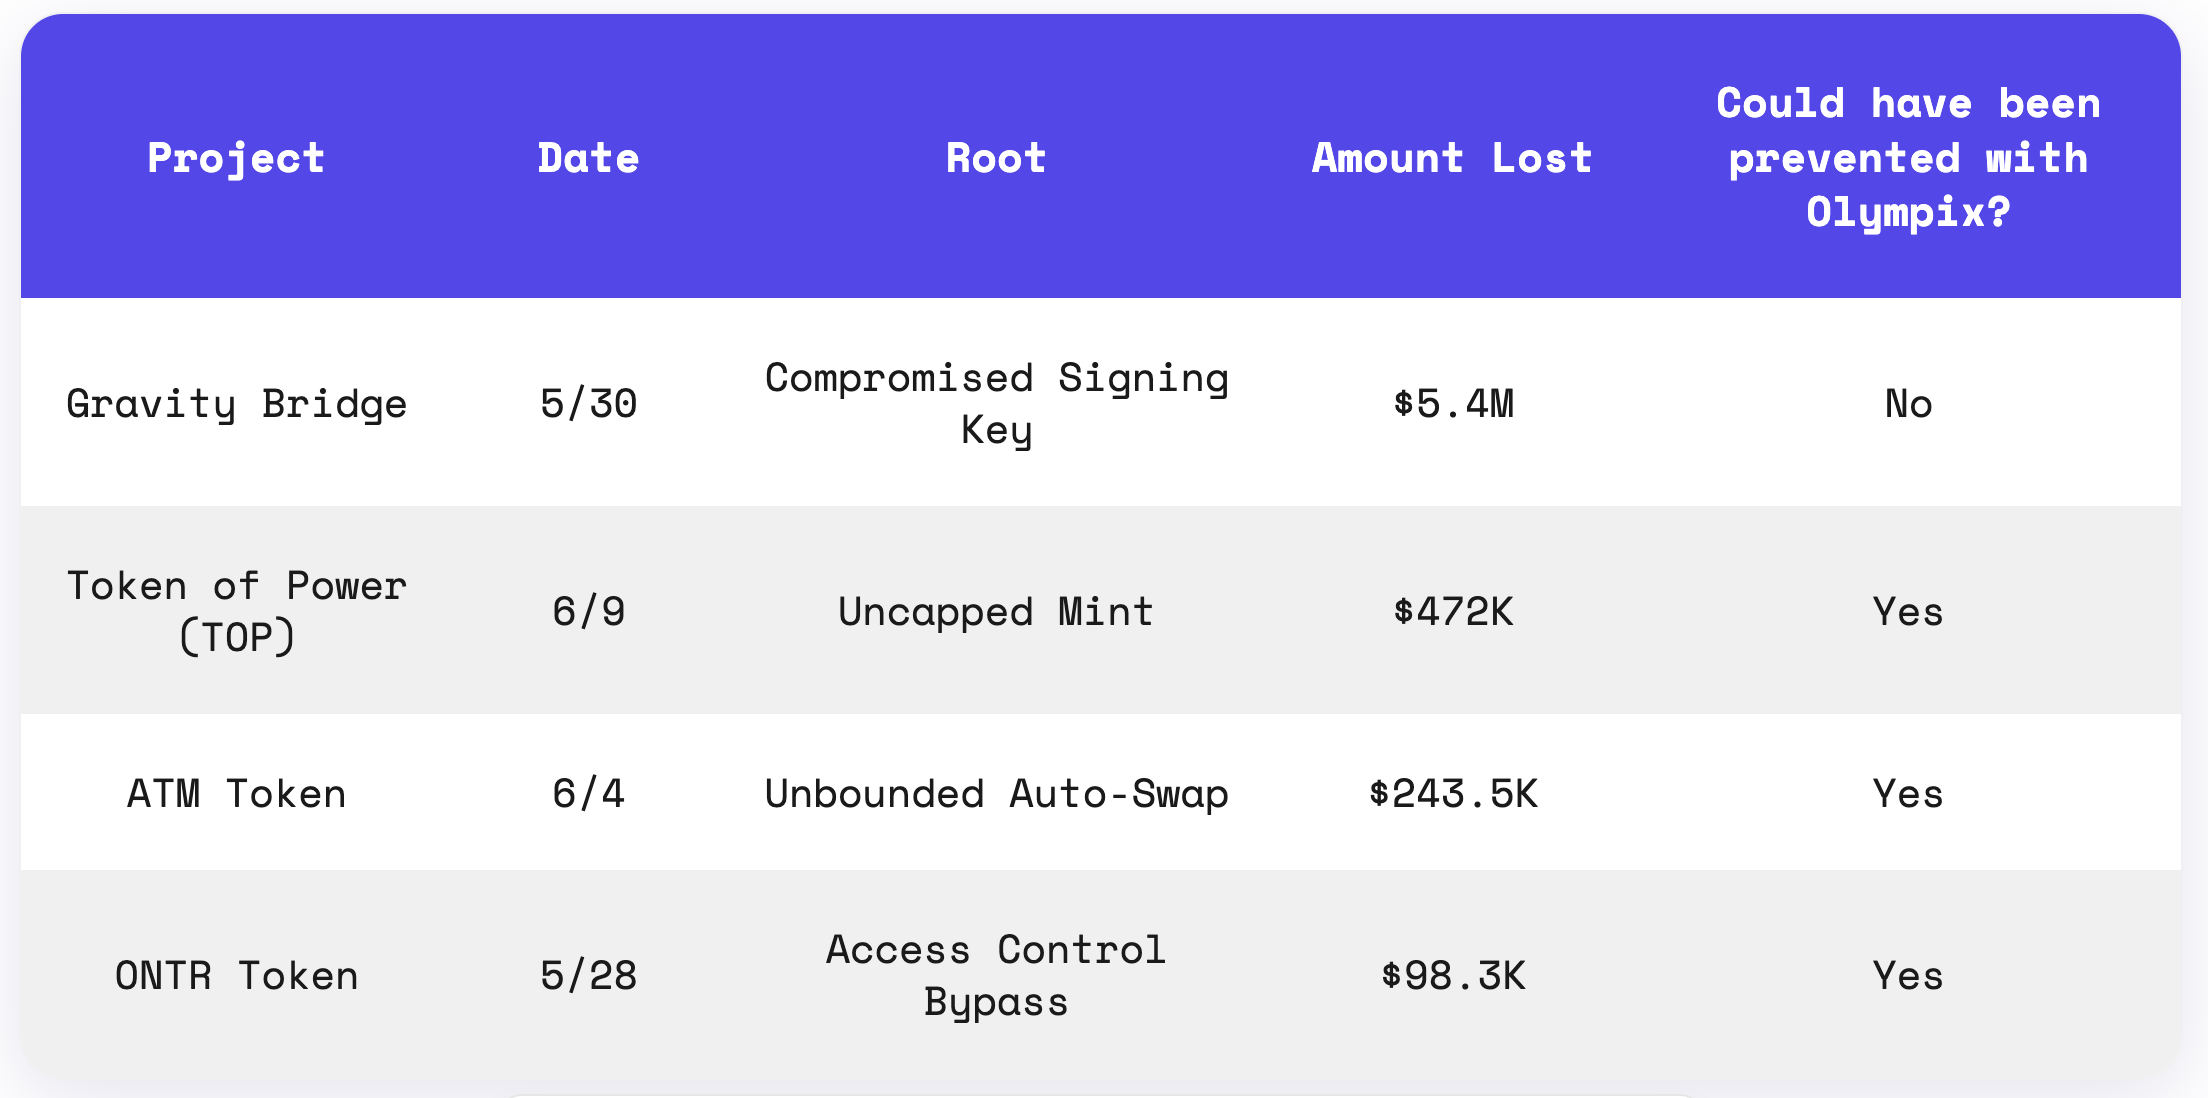
One stolen key and three code-level flaws. Gravity Bridge ($5.4M) traces to a compromised validator signing key, not a contract bug. TOP ($472K) inflated supply through an uncapped mint, ATM ($243.5K) drained liquidity through a swap buried in its transfer logic, and ONTR ($98.3K) let an attacker seize a renounced contract through a broken owner check.
On May 30th, the Gravity Bridge exploit on Ethereum mainnet resulted in a ~$5.4M loss. The root cause was not a smart contract flaw but a compromised validator signing key. Gravity Bridge locks assets on Ethereum and authorizes withdrawals based on validator signatures, so the contract treats any sufficiently signed withdrawal as legitimate. The attacker obtained the signing key and submitted forged withdrawal requests that the contract verified as valid, draining roughly $4.3M USDC, 274 WETH (~$553K), $434K USDT, and 14.16 PAXG (~$64K). The attacker laundered a portion through ChangeNow and Binance and still holds around 2,100 ETH.

Exploited Contract: 0xa4108aA1Ec4967F8b52220a4f7e94A8201F2D906
Transaction: 0xfce883a8f9a4f3479cce1368b99287973ab40451ac092f5a41e1e09eecab5044
On June 9th, the Token of Power (TOP) exploit on Ethereum drained roughly 944 ETH gross (about $1.58M), with a net loss near 281 WETH (about $472K) after backing out the attacker’s own acquisition cost. The attacker acquired a governance majority through TOP’s own Balancer V1 pool, then pushed a single governance action through to the TokenManager — which minted 10 billion TOP to the attacker, dumped for WETH and laundered through Tornado Cash.
At the center of the loss is an uncapped self-mint: the mint path in TokenManager.issue() calls generateTokens() with no max-supply check, so any holder of the minting privilege can inflate supply without bound. Olympix’s BugPoCer scan flags this directly as missing_mint_cap — the code-level flaw that made the supply inflation possible, caught by static analysis before it ever reaches mainnet.

TOP Token: 0x0EBD5eC91680d3B0CEDbb1d5BB61851154D3eDb6
Exploit Contract: 0x25c68C44A96518294f5B47D758f98309c6729A21
Attacker Wallet: 0xff8eF7bC455a57e5893232203052Ce0232b39Fa2
Exploit Tx: 0x967aa34c69b7775c718545c7f94d92e965eb5fc553c0f27f6f1a9c65c93ac156
On June 4th, the ATM token exploit on BNB Chain resulted in a ~$243.5K loss. The root cause was a flaw in the token’s custom `transferFrom()`, which embedded a DEX swap directly in the transfer path: on every transfer the function automatically converted 20% of the transferred ATM into BSC-USD through a router. The implementation did not properly bound this behavior, so the attacker repeatedly triggered transfers to invoke the swap over and over, extracting far more BSC-USD than the transfers warranted and draining roughly $243,500 from the contract.

Vulnerable Contract: 0x4fd0878ee1bbf7b1019138e8eec746e5a5d5a205
Transaction: 0x37b90a337075cd2feea93b12780abe9f953dad476e1c1418a02447aaa6dcfd86
On May 28th, the ONTR token exploit on Ethereum mainnet resulted in a ~$98.3K loss (49.4801 WETH). The root cause was an access control flaw in the `onlyOwner` modifier, which treated a renounced owner (`owner == address(0)`) as a pass-all condition rather than a lock. After the creator renounced ownership at deployment, the attacker called `transferOwnership()` to seize the supposedly locked contract, used `desertJasper()` to stage hidden balances and `glenFlash()` to execute `ashBud()`, inflating an address balance by 1e30 base units with no change to `totalSupply` and no mint logs. The attacker then sold the fabricated tokens into the ONTR/WETH PancakeSwap pair and drained real WETH from the pool.

Vulnerable Token: 0xf074865358b0dd039beee075831f8a2ae6b1f3f3
Transaction: 0x98f80eff0ce609606bb73cef3edfbb4c1d415ffc7676fec16f4d980c54903621
Attacker EOA: 0xE806B37A9F965bd9D54AaDf9560C78957550b760
Attacker contract: 0xd7a33e89abc1ac5b2497d9589c81784a2bc52491
Victim Pair: 0xd46d89f4675bc96328fbdeb443842cdb5fcd83fd