

Two protocols forgot slippage protection. One lost control of a private key.
DRLVaultV3 trusted manipulated prices. Sharwa let swaps go through unchecked. 402Bridge handed over its bridge to an attacker. These are rookie-level failures with multi-chain impact.
On November 10th, the DRLVaultV3 exploit on the Ethereum mainnet resulted in a $98K loss. The root cause of the exploit was a logic error that failed to provide slippage protection. The attacker first borrowed USDC from Morpho Blue and purchased large amounts of WETH, artificially inflating WETH’s price in the pool. The attacker then triggered the vault’s swapToWETH() function which calculated the amountOutMinimum with a 0.5% slippage tolerance. Because the slippage protection referenced the already-manipulated price instead of a true market price, it failed to prevent the manipulated trade. The vault swapped its USDC for WETH at the inflated price.
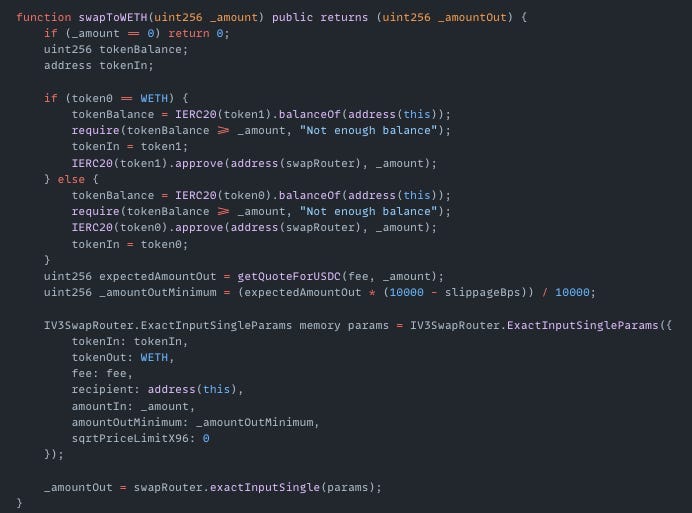
Exploited Contract: 0x6A06707ab339BEE00C6663db17DdB422301ff5e8
Transaction: 0xe3eab35b288c086afa9b86a97ab93c7bb61d21b1951a156d2a8f6f5d5715c475
On October 27th, the 402Bridge exploit on Base chain resulted in a $18K loss due to a private key compromise. The attacker was able to transfer the ownership of 402Bridge’s bridge contract and drained USDC from accounts that had previously granted spending permissions. The stolen funds were converted to ETH and bridged to Arbitrum. The domain 402bridge.fun had been registered just two days before the attack and was shut down immediately after.
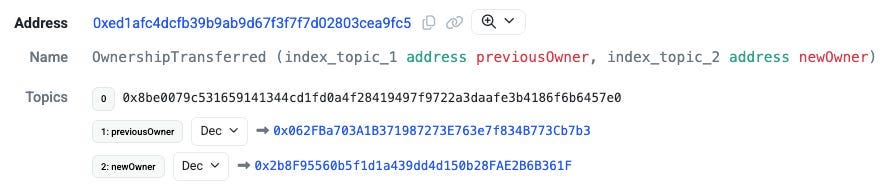
Exploited Contract (on Base): 0xed1afc4dcfb39b9ab9d67f3f7f7d02803cea9fc5
Transaction: 0x089a6336425c6ee6d8954923763cbaeef1173ce44b5c0ab853c85863726e46e2
On October 20th, the Sharwa Finance exploit on the Arbitrum chain resulted in a $146K loss across two attacks. The root cause was that the Sharwa Finance contract was missing slippage protection for swaps. The attacker first deposited USDC collateral, added liquidity to bypass lending limits, and opened a long WBTC position with borrowed USDC. Using a flash loan, the attacker sold WBTC on Uniswap to decrease the price. The attacker repurchased WBTC at the manipulated price, repaid the flash loan, and made a profit.

Exploited Contract (on Arbitrum): 0x5c479762c8fe57b6d874893a4b4932b40f612580
Transaction 1: 0x9f8b4841f805ec50cc6632068f759216d85633fbbe34afde86b97bbc41c23ead
Transaction 2: 0xb0bf77475818b2501e78f0927f4131e52c6efd45bc4978992cbbe218a57e6f7f