

DeltaPrime lost $4.8M after failing to validate debt repayment in swapDebtParaSwap(), letting attackers drain collateral without settling loans. Ramses Exchange was hit for $93K after its FeeDistributor contract failed to limit reward claims per token ID. Morpho Protocol’s $230K loss came from a 12-decimal misconfig in its PAXG/USDC oracle, grossly inflating collateral value.
On November 11th, the DeltaPrime exploit on Arbitrum and Avalanche chains resulted in a $4.8M loss. The root cause of the exploit was a flaw in the swapDebtParaSwap() function. The function failed to ensure that borrowed tokens were properly repaid, allowing _repayAmount to remain 0. The attacker initiated the exploit with a 59.9 ETH flash loan, used it as collateral to borrow 1.18 WBTC, and transferred the borrowed WBTC to a malicious contract via a swap. Since no repayment occurred, the attacker retained their original collateral while profiting from the borrowed tokens.

Exploited Contract (on Arbitrum): 0xca60c5d2ee1f9c79c92a9d5831dc22ccc291b5f5
Transaction Hash: 0x26405f8da2058592090a73c66a369960867976a84f975f41acb01280b88dc2f6
On October 24th, the Ramses Exchange exploit on Arbitrum resulted in a $93K loss. The root cause of the exploit was a flaw in the FeeDistributer contract’s reward distribution logic. The attacker claimed rewards multiple times using different token IDs, bypassing reward limits. This was possible because the private _getReward() function failed to properly track rewards for each token ID, specifically in the tokenTotalSupplyByPeriod and veWithdrawnTokenAmountByPeriod values.

Exploited Contract (on Arbitrum): 0x3606230b62e64ace5829f00c9c3b6c5bd96ccaec
Transaction Hash: 0xb91c4e0debaf0feb1f20c979eebc1282c8024ae299ef5903591badcf1f4938bb
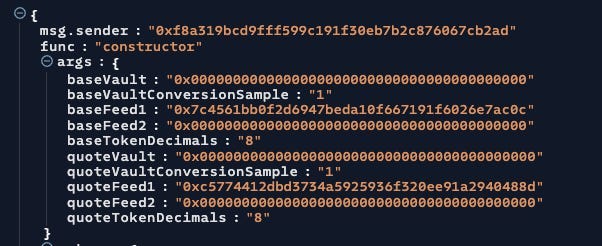
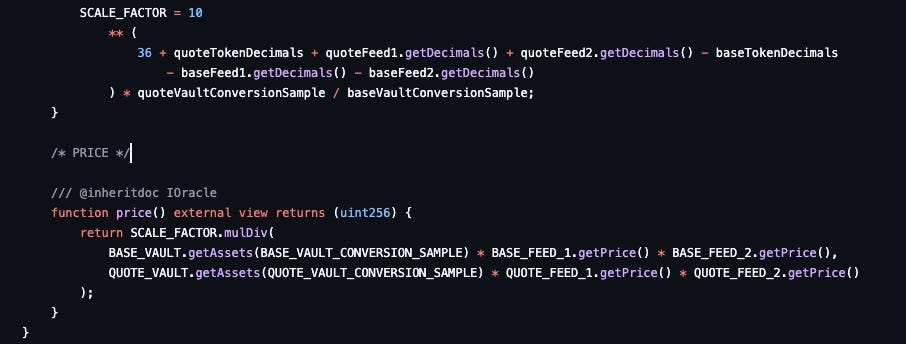
On October 13th, the Morpho Protocol exploit on the Ethereum mainnet resulted in a $230K loss. The attack exploited the PAXG/USDC market due to a misconfiguration in the Oracle Price setup. The deployer mistakenly set both tokens to 8 decimals instead of accounting for USDC’s 6 decimals and PAXG’s 18 decimals. This caused a 12-decimal inflation, overvaluing PAXG by a factor of 10¹². The attacker exploited this by supplying $350 worth of PAXG to borrow 230,000 USDC.
Exploited Contract: 0xdd1778f71a4a1c6a0efebd8ae9f8848634ce1101
Transaction Hash: 0x256979ae169abb7fbbbbc14188742f4b9debf48b48ad5b5207cadcc99ccb493b
MorphoChainlinkOracleV2 Repository: https://github.com/morpho-org/morpho-blue-oracles/blob/main/src/morpho-chainlink/MorphoChainlinkOracleV2.sol