

From leaked keys to inverted require() to broken whitelist logic—these three exploits show that access control isn’t a checklist, it’s your protocol’s trust boundary. If it fails, everything else is noise.
On August 14th, the BtcTurk exploit on multiple chains resulted in a $51.7M loss due to a private key leak. The attacker was able to drain hot-wallets for more than 90 assets across Ethereum, Avalanche, Arbitrum, Base, Optimism, Mantle, and Polygon. BtcTurk acknowledged the incident and paused all deposits and withdrawals. It was their second private key compromise in 14 months.
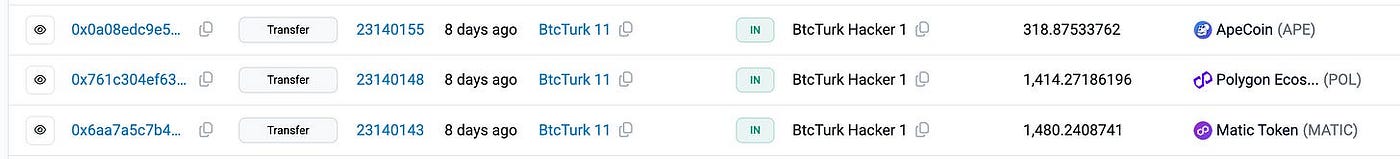
Exploited Contract (one of the hot wallets): 0xde2faca4bbc0aca08ff04d387c39b6f6325bf82a
Transaction: 0xb191ec12f7e579b29840429940ca9a5049cc5cdf6c6904e607992323e6276931
On July 28th, the SuperRare exploit on the Ethereum mainnet resulted in a $680K loss due to an access control vulnerability. The root cause was in the updateMerkleRoot() function in the RareStakingV1 contract where the access check was inverted. It prevented the owner from updating the Merkle root but allowed any external account to do so. The attacker called this function to install a malicious Merkle root under their control. With that root in place, drained 11,907,875 RARE tokens.
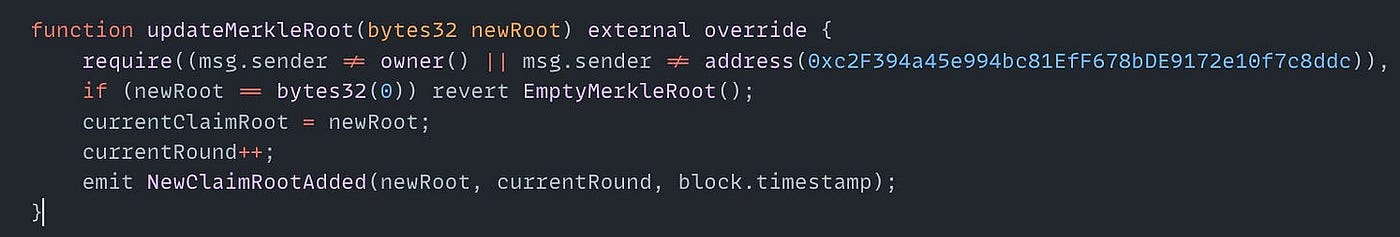
Exploited Contract: 0xffb512b9176d527c5d32189c3e310ed4ab2bb9ec
Transaction: 0xd813751bfb98a51912b8394b5856ae4515be6a9c6e5583e06b41d9255ba6e3c1
On July 17th, the WETC Token exploit on the BNB Chain resulted in a $100K loss. The root cause of the exploit was in the private _transfer() function where if either ‘from’ or ‘to’ address is whitelisted, the code calls super._transfer and does not return. It then continues into the DEX path and runs transferBuy/transferSell, moving tokens a second time. The attacker sent WETC to the pair to create balance over reserves, then called skim to send that excess to a whitelisted address. The bug doubled each skim payout and allowed the attacker to make a profit.
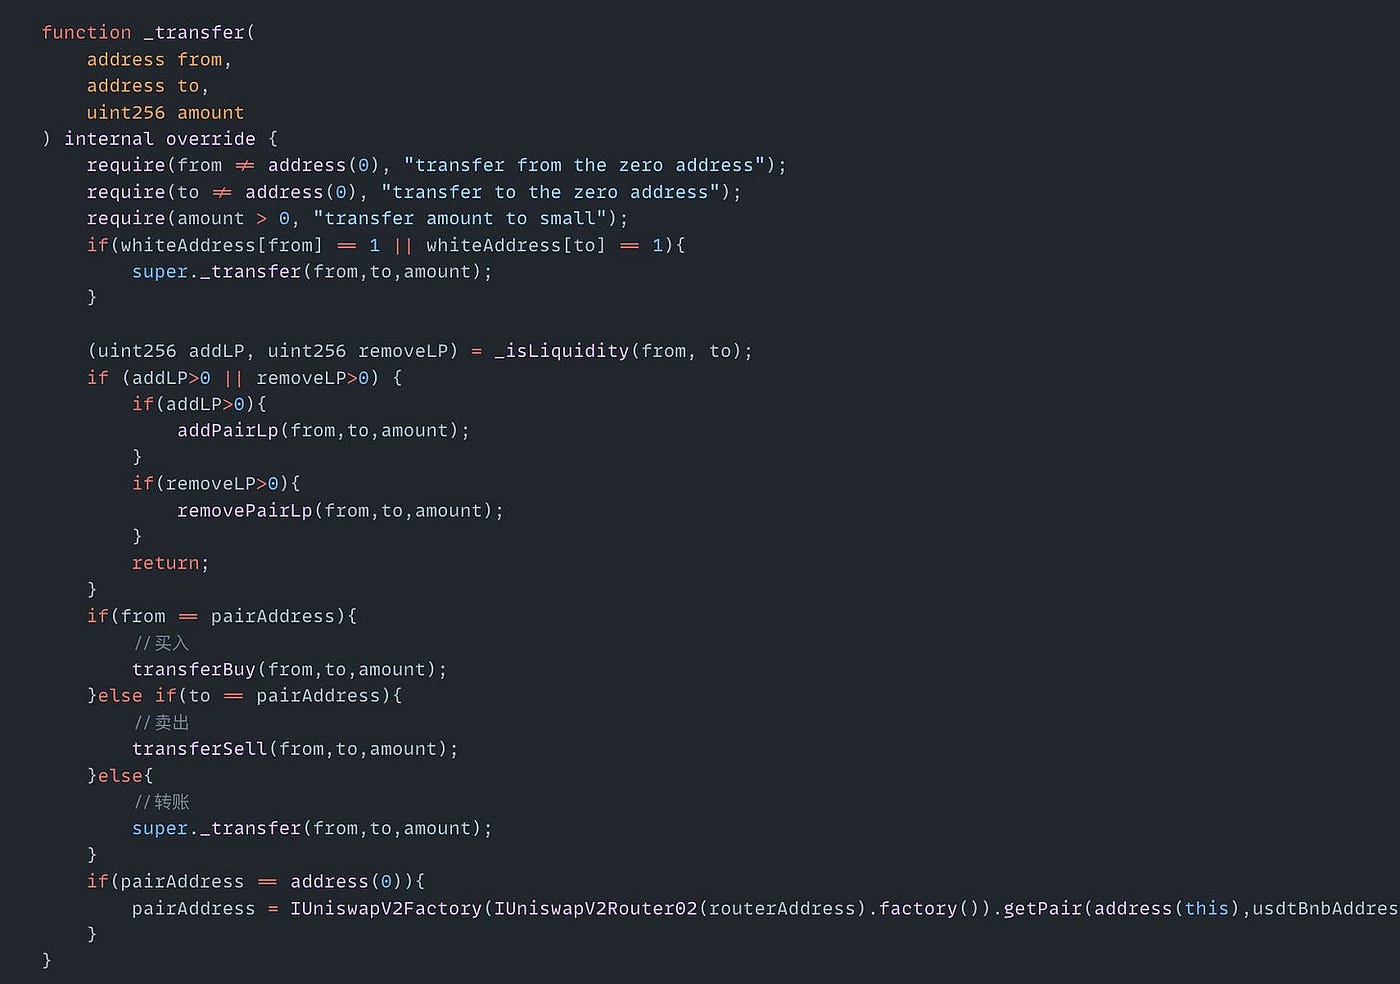
Exploited Contract (on BSC): 0xe7f12b72bfd6e83c237318b89512b418e7f6d7a7
Transaction: 0x2b6b411adf6c452825e48b97857375ff82b9487064b2f3d5bc2ca7a5ed08d615