
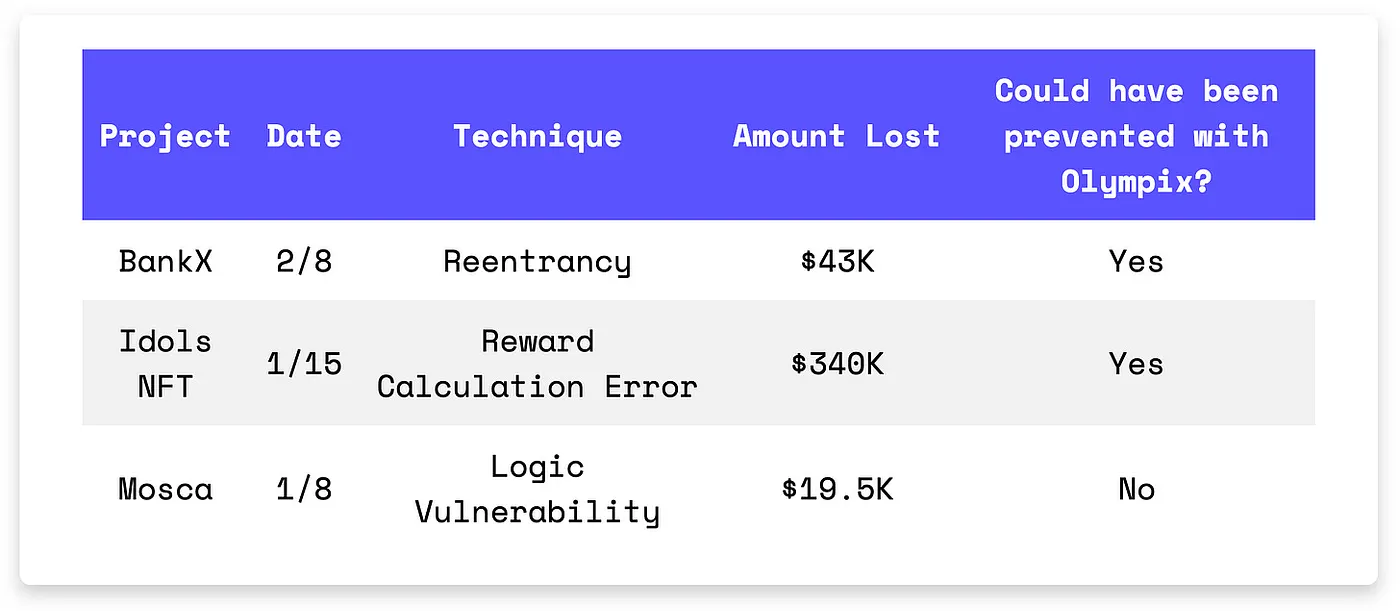
BankX lost $43K from a reentrancy flaw that let attackers burn tokens mid-swap and game the price. Idols NFT leaked $340K due to a double reward logic triggered by same-address transfers. Mosca’s flawed state reset let attackers drain rewards by preserving USDT and USDC balances between cycles.
On February 8, the BankX hack on the Binance Smart Chain led to a $43K loss. The root cause of the exploit was that the swapXSDForETH() function of the Router contract was missing reentrancy safeguards. The attacker initiated a swap, sending XSD tokens to the pool for ETH. The function made an external call to IXSDWETHpool.swap before updating the state. This allowed the attacker to call the function repeatedly. Each call triggered burnpoolXSD, burning excess XSD tokens. The reduced supply inflated the token price. The attacker then sold the XSD at the higher manipulated price for profit.
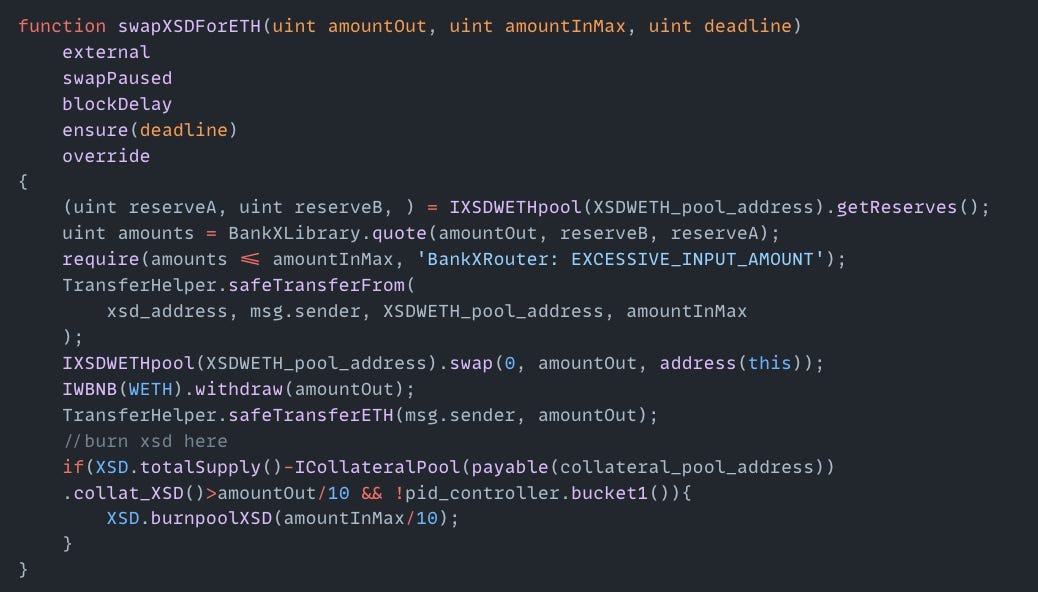
Exploited Contract (on BSC): 0xaadae9117df8b5d584378a41a105cc4862a16e99
Transaction: 0xe808330b8ddc2f7c6164743c210c9e1975de87c1949c6353d98f2d39e4dde182
On January 15th, the Idols NFT exploit on the Ethereum mainnet resulted in a $340K loss due to a flaw in the _beforeTokenTransfer() function. The attacker transferred NFTs to themselves in repeated transfers (same ‘from’ and ‘to’ address). Each transfer triggered reward payments twice: once for the sender, then again for the receiver. The function then erased the sender’s reward history after the first payment, making the second payment calculate rewards as if none were claimed. This allowed the attacker to collect rewards twice per transfer.


Exploited Contract: 0x439cac149b935ae1d726569800972e1669d17094
Transaction: 0xa8289dbe3e49e9c5decaabd3777d9ad60a7b06863539b4948dd17e58a65f3e15
On January 8th, the Mosca exploit on the Binance Smart Chain resulted in a $19.5K loss. The root cause of the exploit was a logic vulnerability in the exitProgram() function which calculates rewards in withdrawAll() function by summing user.balance, user.balanceUSDT, and user.balanceUSDC, then transfers the total. However, exitProgram() only clears user.balance, leaving USDT and USDC balances unchanged. Using flash loans, the attacker triggered the buy() function to inflate their rewards. By repeatedly calling join() and exitProgram(), the attacker withdrew the full reward amount each time, including the nonzero USDT and USDC balances.
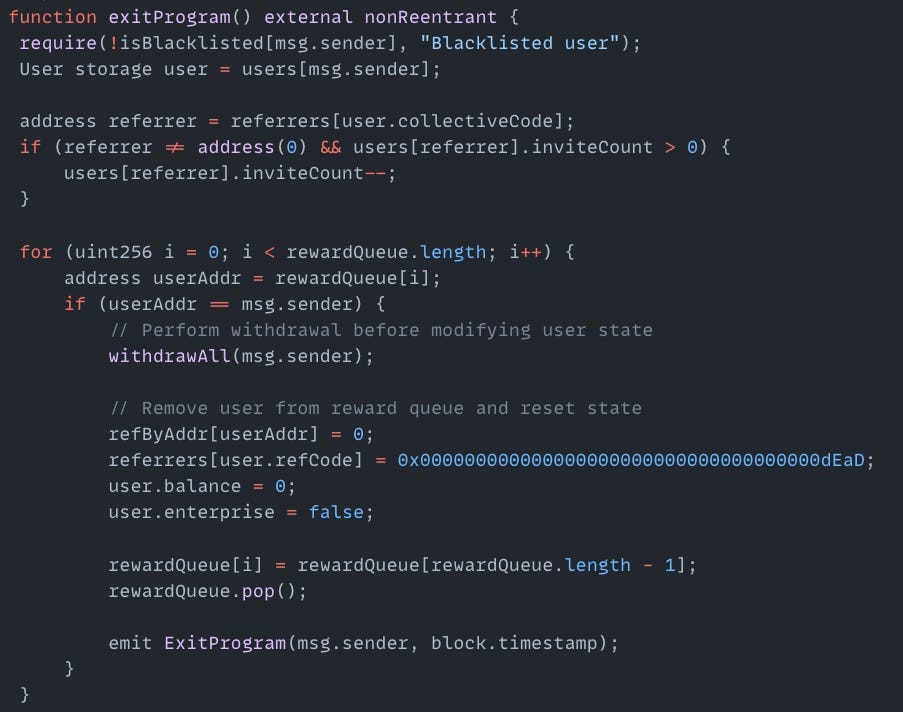
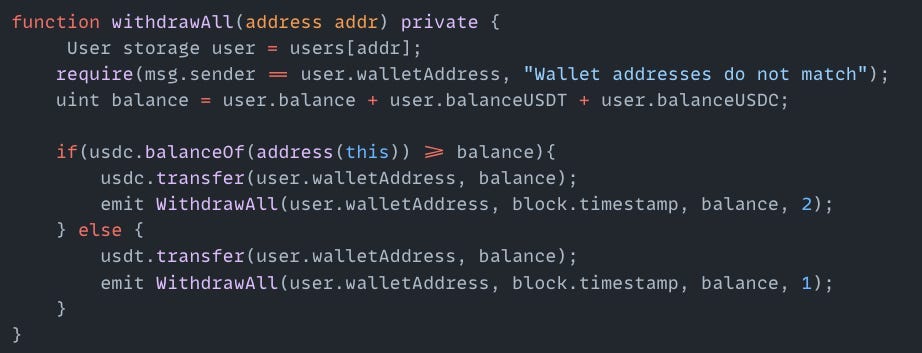
Exploited Contract (on BSC): 0x1962b3356122d6a56f978e112d14f5e23a25037d
Transaction: 0x4e5bb7e3f552f5ee6ee97db9a9fcf07287aae9a1974e24999690855741121aff