
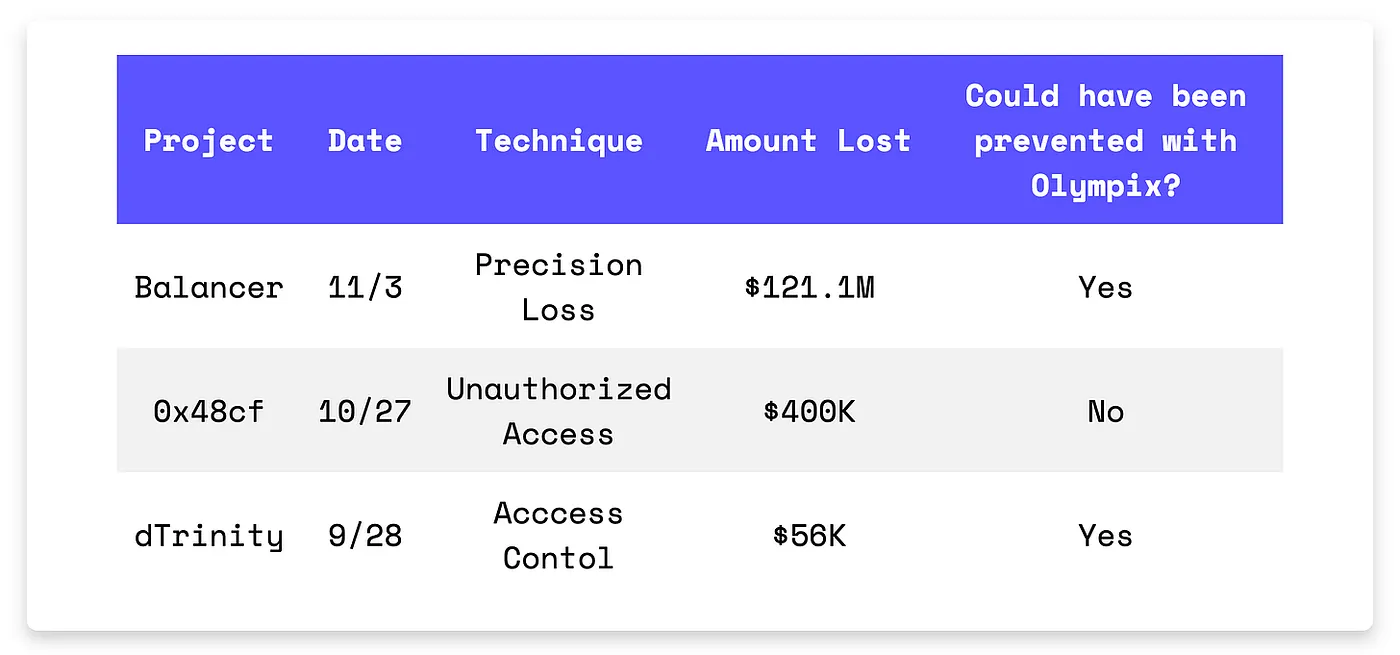
One rounding flaw. One upgrade path. One unchecked function.
Balancer’s precision bug let 17 wei drain $121M. 0x48cf handed out an upgrade slot with no validation. dTrinity skipped a simple auth check.
These aren’t edge cases. They’re basics. And they’re still costing teams millions.
On November 3rd, the Balancer exploit across multiple chains resulted in a $121.1M loss. The root cause of the expoit was in the Composable Stable Pool’s _swapGivenOut() function, which upscaled swap amounts using the _upscale() function that rounded down instead of up. The attacker swapped precisely 17 wei of osETH, causing the upscaling calculation to lose 5.8% precision due to rounding. The attacker exploited this by repeatedly swapping BPT tokens for underlying assets like WETH and osETH and made a profit.
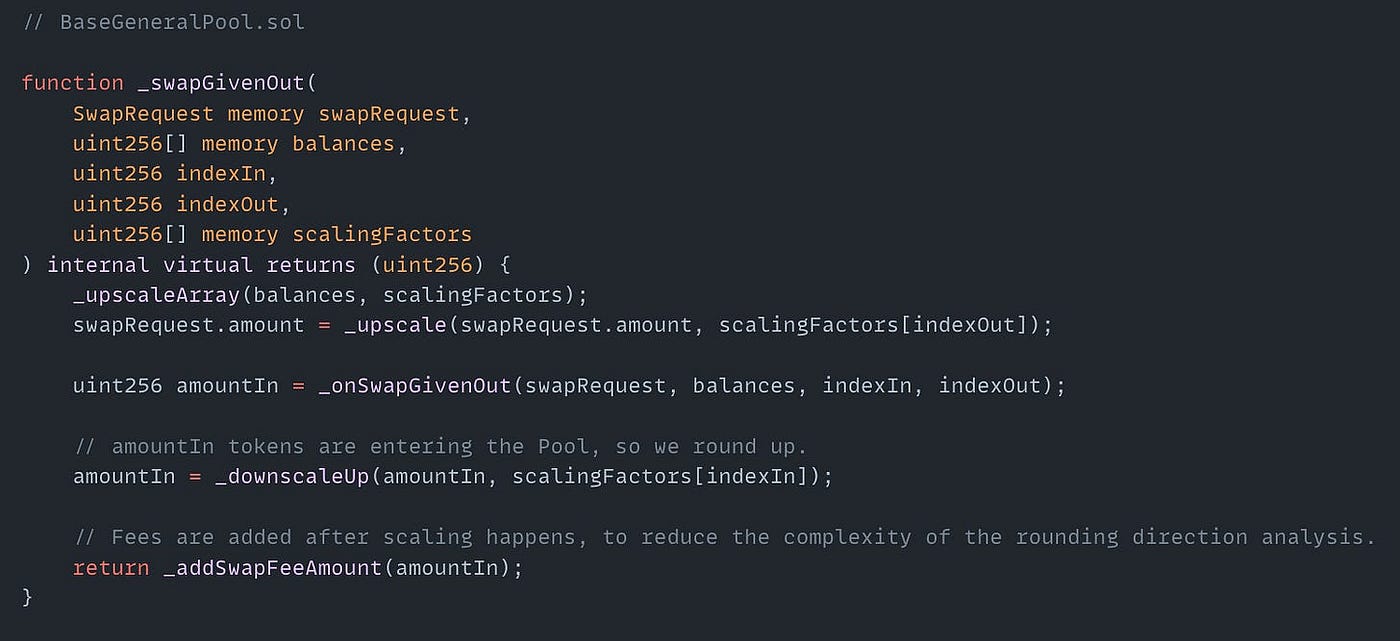
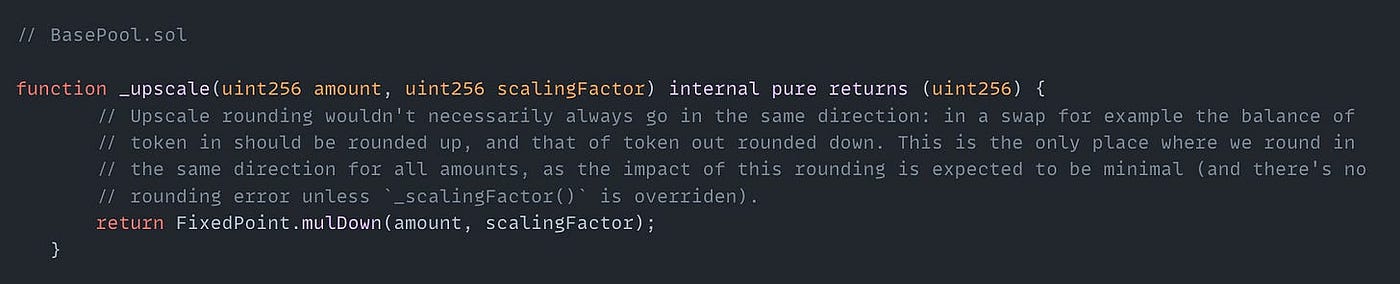
Exploited Contract: 0xdacf5fa19b1f720111609043ac67a9818262850c
Transaction: 0x6ed07db1a9fe5c0794d44cd36081d6a6df103fab868cdd75d581e3bd23bc9742
On October 27th, the 0x48cf exploit across Ethereum and Arbitrum resulted in a $400K loss. The root cause of the exploit was an unauthorized access attack where the attacker upgraded the victim’s contract to a malicious implementation containing a backdoor function. This backdoor contained a withdrawal function specifically designed to drain 481M Capital DAO Starter (CDS) tokens.
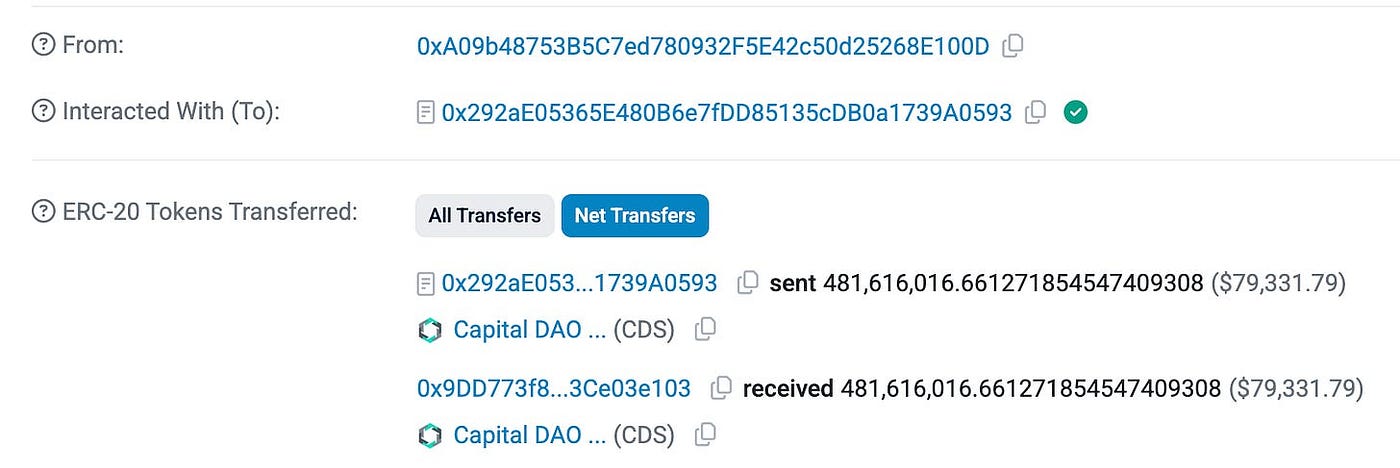
Exploited Contract: 0x48cfac26a7418057467582d73d5a5c807234f460
Transaction: 0xbadab26cbbc08e26d3b8d34f3c4da798934dc7f6396ea61f99a86648a9c73da9
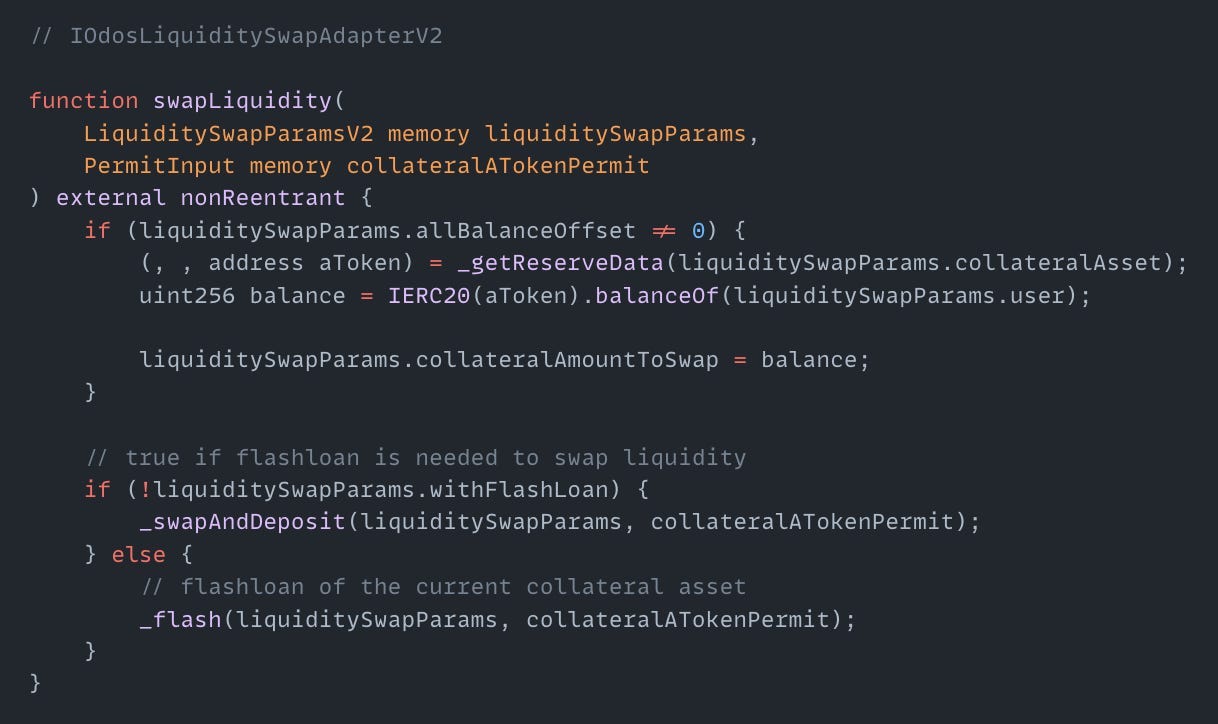
On September 28th, the dTrinity exploit on Sonic resulted in a $56K loss. affecting three team members. The root cause of the exploit was a missing authorization check in the swapLiquidity() function of the IOdosLiquiditySwapAdapter contract. The attacker called the swap function using victims’ addresses who had previously approved the adapter contract. This let the attacker withdraw victims’ collateral deposits (aTokens) without permission. The attacker used malicious swap routes that sent the collateral to attacker-controlled addresses while returning minimal amounts to pass validation. Three team members lost funds because they had approved the adapter during testing.
Exploited Contract (on Sonic): 0x9ee939ddc8eaaac72d3cae793b12a09d92624e4a
Transaction: 0xa6aef05387f5b86b1fd563256fc9223f3c22f74292d66ac796d3f08fd311d940