

AlexLab’s Clarity contract failed to catch a bad deployment, leading to an $8.4M drain. LNDFi hired a DPRK-linked dev who walked off with $1.3M via backdoored pool logic. MBU’s deposit math applied 18 decimals twice, letting an attacker mint tokens worth $2.2M. Three high-stakes misses, one common theme: no second layer of defense.
On June 6, the AlexLab exploit on Stacks resulted in a $8.4M loss due an access control vulnerability. The attacker exploited AlexLab’s self-listing feature in the create2() function. The self-listing-helper-v3a contract erroneously approved a malicious token because it failed to invalidate a failed contract deployment. The approval of the malicious token allowed the attacker to drain funds from the liquidity pools. The official AlexLab post mortem claims that the root cause was a limitation in the Clarity smart contract language which fails to verify if a transaction fails.
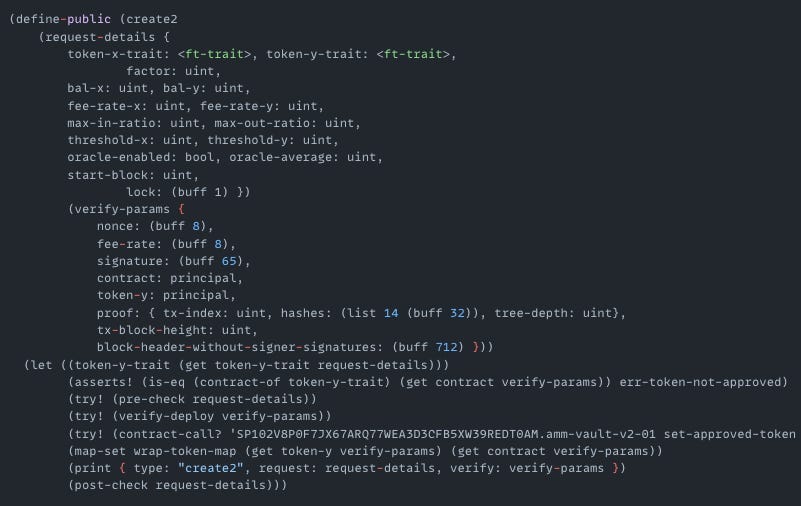
Exploited Contract (on Stacks): SP1E0XBN9T4B10E9QMR7XMFJPMA19D77WY3KP2QKC.self-listing-helper-v3a
Transaction: 0xfb4822786771285238e082f46bee1203d9ccb9cedfd1b3e6e574a4908d53474f
On May 9th, the LNDFi exploit on Sonic resulted in a $1.3M loss due to a compromised deployer wallet. The LNDFi hired an undercover A DPRK-linked developer who gained access to admin keys and initiated unauthorized transactions. The attacker modified smart contracts to bypass pool access controls, allowing any Pool Admin to call restricted functions. Using this backdoor, they drained the pools via the transferUnderlyingTo function.

Exploited Contract (on Sonic): 0xaa8cc9afe14f3a2b200ca25382e7c87cd883a527
Transaction: 0xd52f317b548bd0f67d32d35404d046e4e60f5af23dac8a502495a8714780bffe
On May 11th, the MBU token exploit on BNB Chain resulted in a $2.2M loss. The root cause of the exploit is a vulnerability in the deposit() function that mishandled decimal calculations. By sending 0.001 BNB, the attacker was able to mint MBU tokens 10¹⁸ times larger than it should have. The attacker exploited the 0x371b() (called by deposit()) function which applied the 18-decimal scale twice without correcting it.
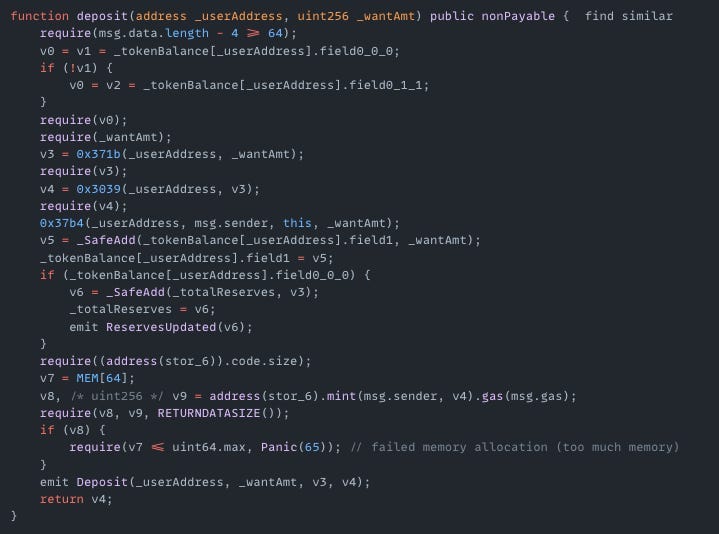
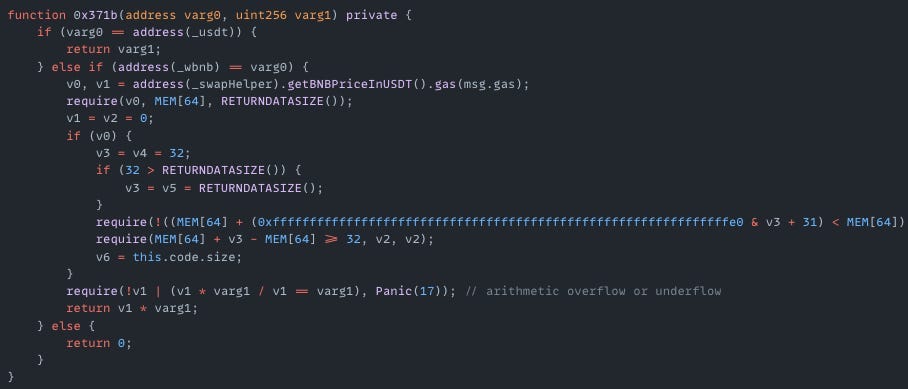
Exploited Contract (on BNB): 0x637d8ce897bb653cb83ba436cdf76bbe158f05b1
Transaction: 0x2a65254b41b42f39331a0bcc9f893518d6b106e80d9a476b8ca3816325f4a150