
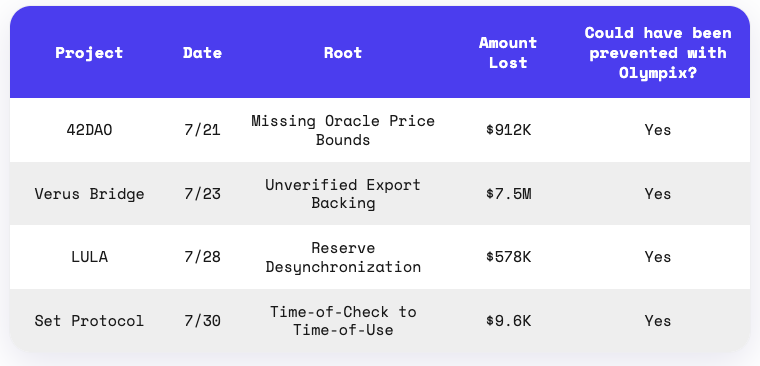
Four exploits this week, $9M gone — and every dollar of it was preventable.
There's a common thread worth naming: in all four, the code performed a check that was real, and then acted on something the check didn't actually cover. A proof was verified but the value behind it wasn't. A price was written but never bounded. A balance was moved but the pool's accounting was rewritten around it. A quote was read but never re-read once someone else had a turn. Every check passed. None of them were sufficient.
Audits confirm the checks that exist. Invariant testing asks whether those checks are enough to hold the property you actually care about — payout never exceeds backing, price never moves more than it should, reserves always reflect real balances. Those are assertable before a line reaches mainnet.
That's the whole idea behind Olympix: catch the insufficient check in the dev loop, so it stays a line in a report instead of a headline.
On July 21st, the 42DAO exploit on BNB Chain drained about $912K through an oracle-price and liquidation flaw in its Maker-style CDP system. The root cause was two compounding code-level gaps. The Spotter's poke() wrote an abnormally low BTCB price into the Vat with no price-deviation check, no max-drawdown limit, and no minimum-price floor, and the Dog's bark() then liquidated multiple BTCB vaults off that spot with no liquidation delay and no oracle validation.
In a single transaction, the attacker pushed the low BTCB price through the Spotter and instantly liquidated the BTCB vaults at the fake price, profiting from the arbitrage. No key or governance compromise, the contracts trusted a price and executed liquidations they should have guarded. This is a Maker-style fork deployed without the deviation checks and liquidation delays the pattern needs.
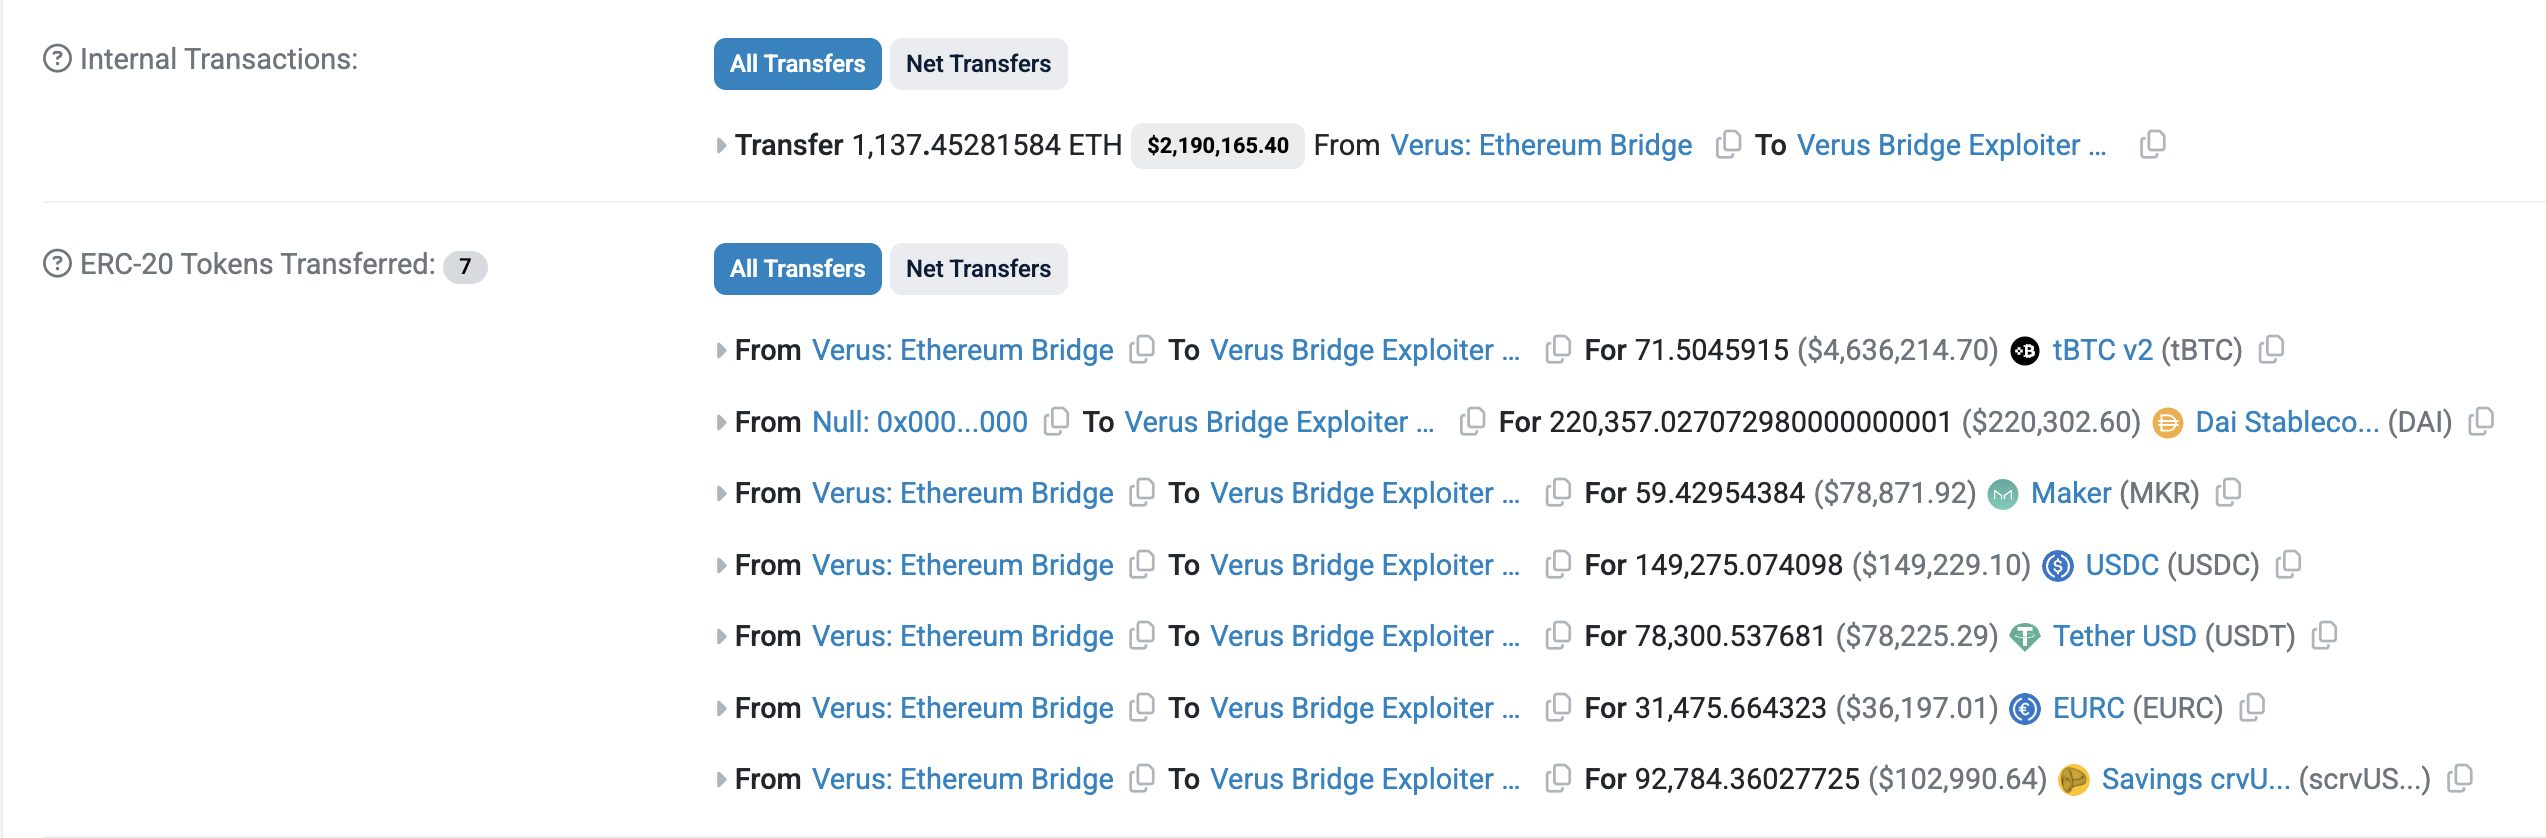
Attacker EOA: 0xbda71b58cec0b1c20a8f87ccd52fa0679747855c
Victim Bridge: 0x71518580f36feceffe0721f06ba4703218cd7f63
Vulnerable Contract: 0x54e03a1682fd0bb065b669f6296f97028dcfd4ce
Fund Receiver: 0xcfd0a20703cd11e0b9f665e1c3f1ef989c142d54
On July 21st, the 42DAO exploit on BNB Chain drained about $912K through an oracle-price and liquidation flaw in its Maker-style CDP system. The root cause was two compounding code-level gaps. The Spotter's poke() wrote an abnormally low BTCB price into the Vat with no price-deviation check, no max-drawdown limit, and no minimum-price floor, and the Dog's bark() then liquidated multiple BTCB vaults off that spot with no liquidation delay and no oracle validation.
In a single transaction, the attacker pushed the low BTCB price through the Spotter and instantly liquidated the BTCB vaults at the fake price, profiting from the arbitrage. No key or governance compromise, the contracts trusted a price and executed liquidations they should have guarded. This is a Maker-style fork deployed without the deviation checks and liquidation delays the pattern needs.
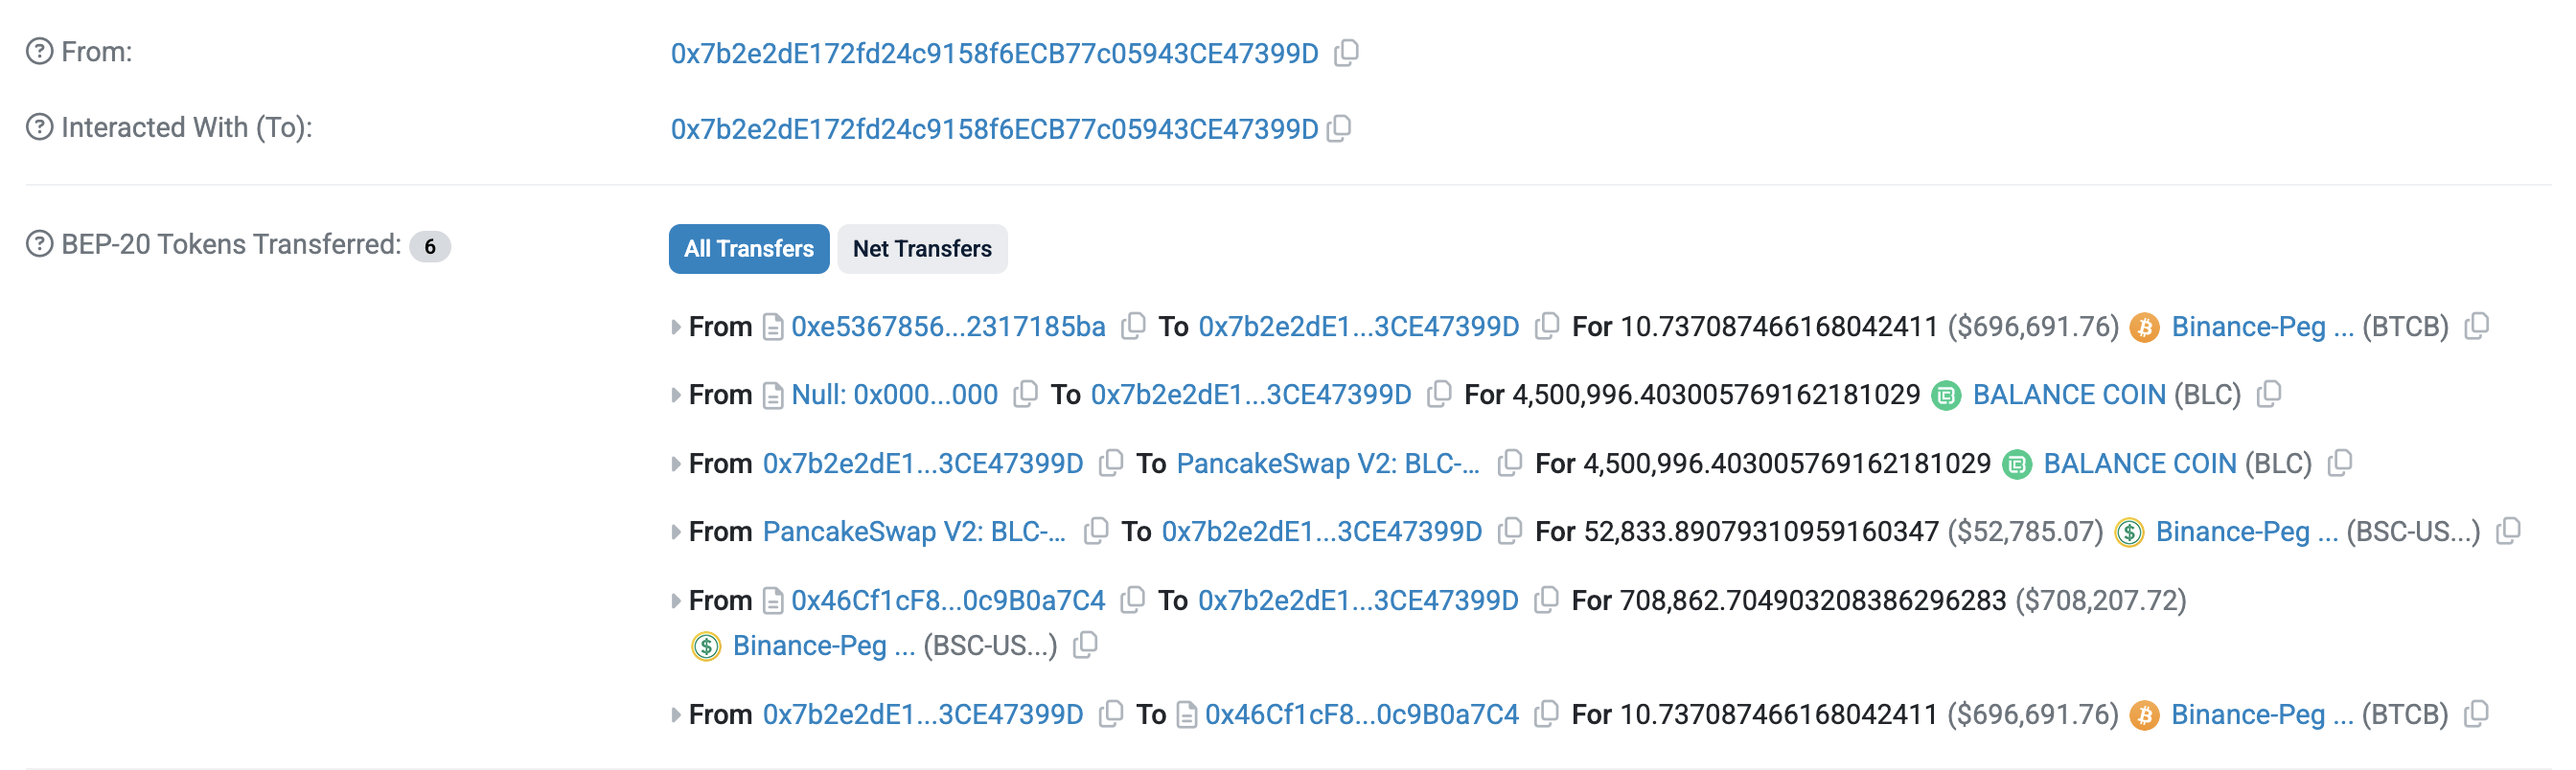
Exploit tx: 0xe7abe6416e386332b41d63cf5f16903251dc178942cd79bf080fe61058587628
On July 28th, the LULA token exploit on BSC drained about $578K from the PancakeSwap V2 pair through a reserve-manipulation flaw in the token's own contract. The root cause was a privileged `recycle()` function that let the Rental contract transfer LULA directly out of the pair using an internal `_basicTransfer()`, which only adjusts balances and emits a Transfer event while bypassing the checks a standard transfer applies, and then call `sync()`, forcing the pair's reserves to match the manipulated balances.
The attacker first swapped a large amount of USDT to LULA to inflate the USDT reserve, repeatedly triggered `recycle()` to shrink the LULA reserve, then swapped a small amount of LULA back to drain the pool at the skewed rate. Helper contracts deployed 12 days earlier accumulated referral and team rewards, and a Lista DAO flash loan of roughly $231.5M WBNB plus $4.4M BSC-USD, routed through Aave and Venus, amplified the swap size. This is the same reserve-manipulation pattern as OLPC/LABUBU: a privileged token-side function that pulls tokens from the pair and syncs, rewriting reserves to drain the opposite side.
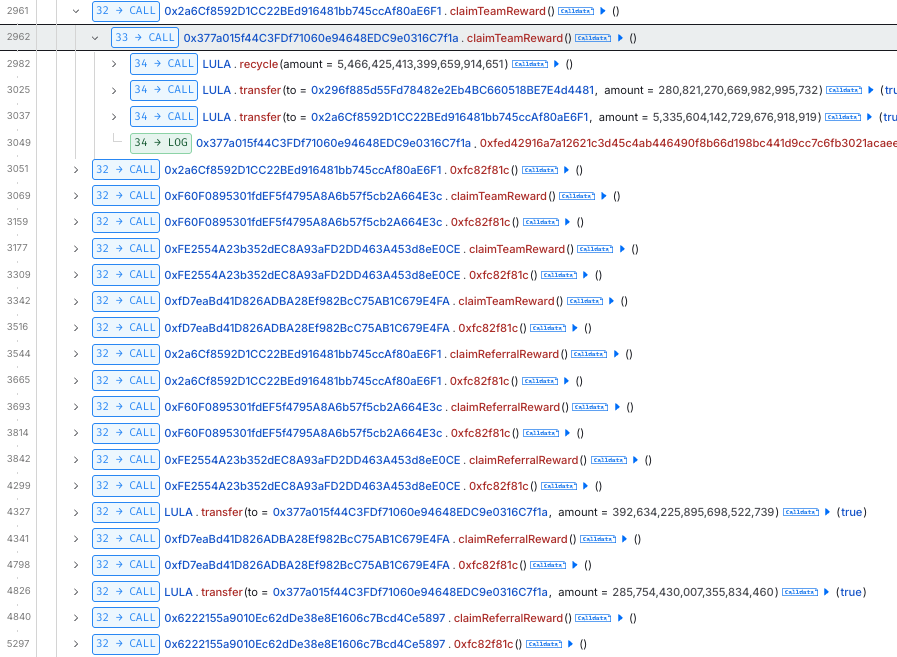
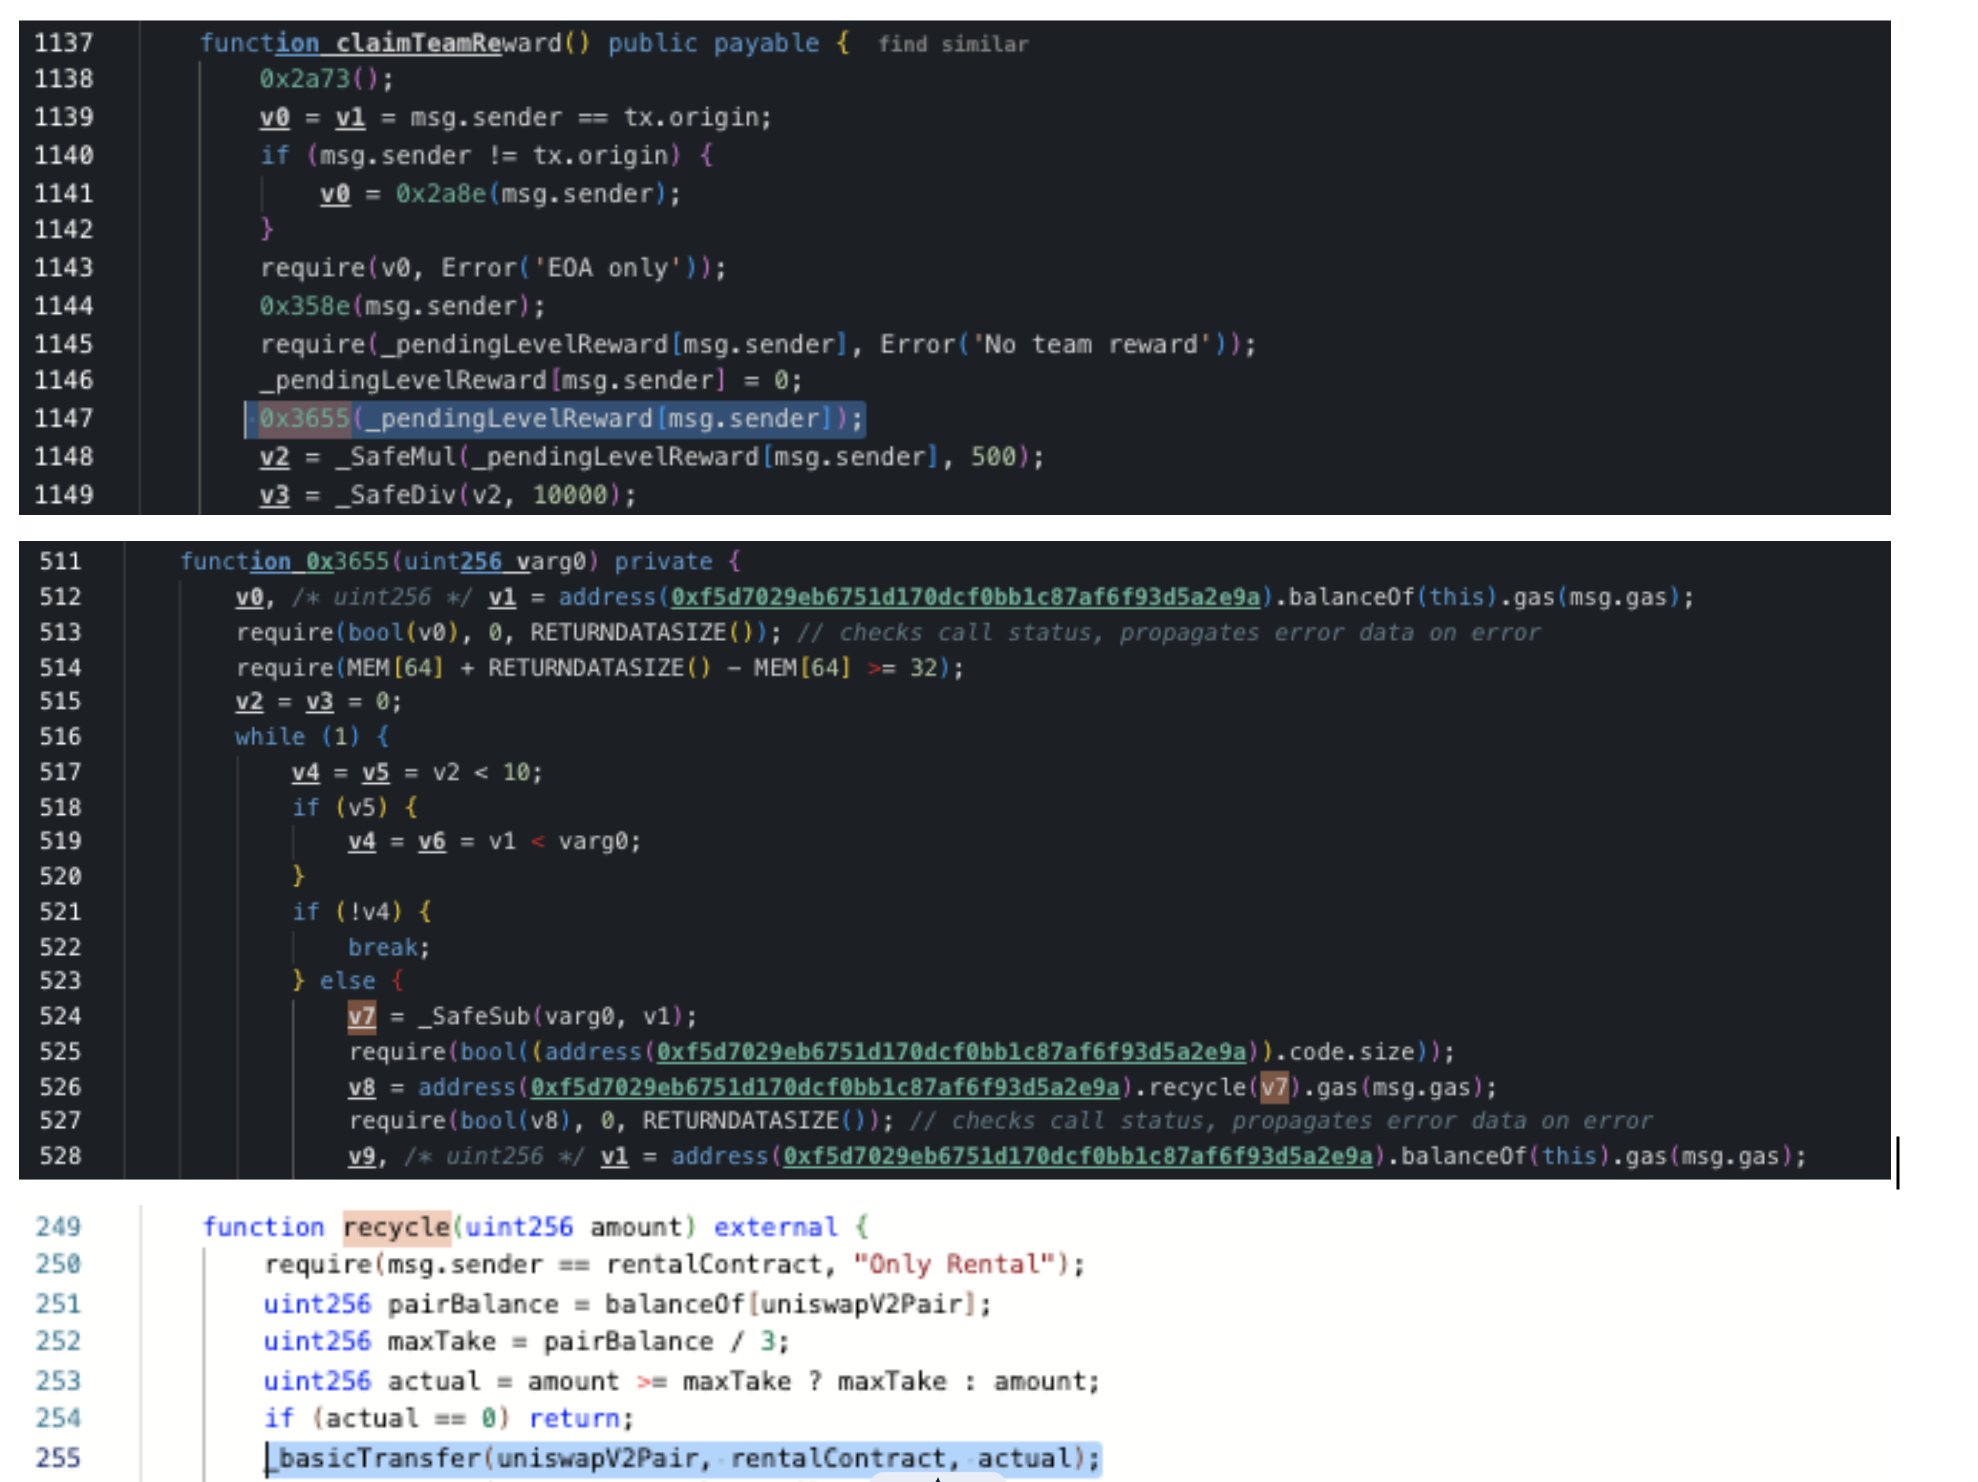
Vulnerable contract (LULA token): 0x72ad494fda63d2b91b9d7290737e8ef1194a0c47
Exploit (drain) tx: 0xa219ab9d57e520e5235b15a8801f4ebac8cc45551be0430ce4e49caea0411d7c
On July 30th, the Set Protocol exploit on Ethereum drained about $9.6K through a TOCTOU flaw in Index Coop's ExchangeIssuance function. The root cause was that `issueSetForExactToken` read a SetToken's components and units to quote the issuance but never locked that state before using it for transfers.
The attacker created their own malicious SetToken (BHSET) with a manager, hook, and valuer they controlled, issued it with a small amount of WETH, then used a pre-issue hook to inflate the SetToken's `positionMultiplier` roughly 93.66x via a NAV `issue`/`redeem` with a fake valuation. When `BasicIssuanceModule.issue` then read the now-inflated units and pulled them from `ExchangeIssuance` via `transferFrom`, it transferred far more than it should have, draining real assets. The value checked at read time had been changed before it was used. No key or governance compromise, the malicious SetToken and manager are attacker-supplied inputs exploiting ExchangeIssuance's missing state lock, not the flaw itself.
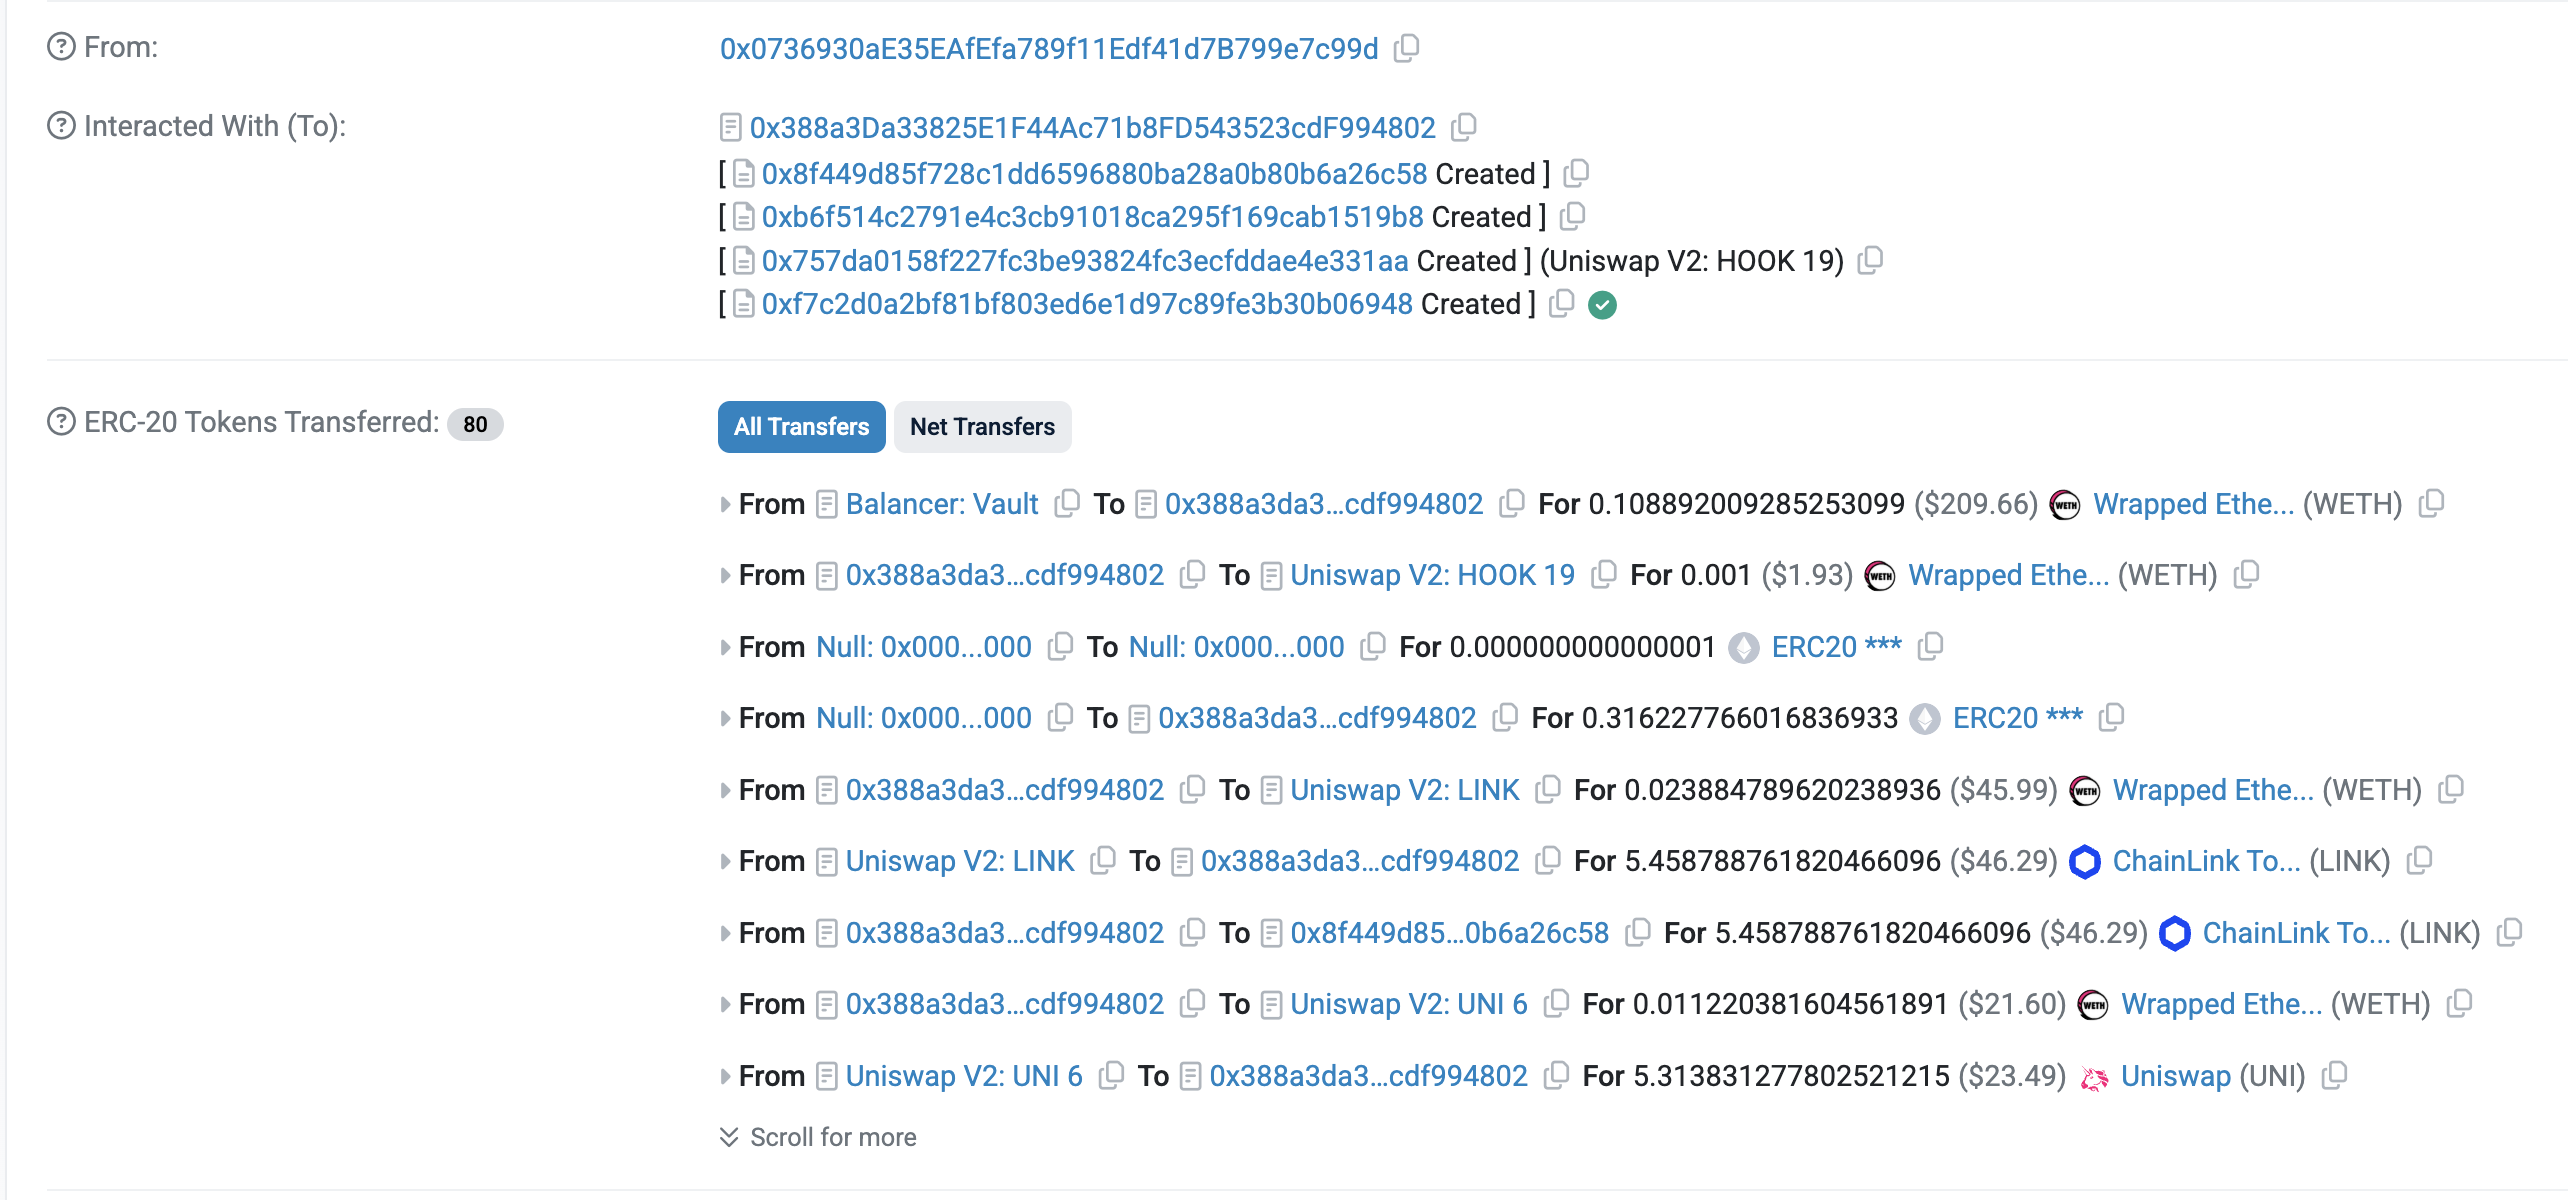
Attacker EOA: 0x0736930ae35eafefa789f11edf41d7b799e7c99d
Victim contract (ExchangeIssuance): 0xc8c85a3b4d03fb3451e7248ff94f780c92f884fd
Exploit tx: 0x7f45428df558fba1d19ab115effef8ecd1e6e05b491f02202b0815e47b8d658b