
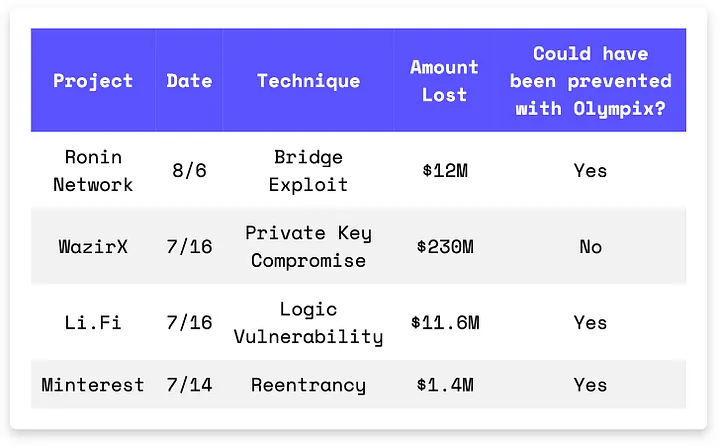
Four major protocols were gutted by basic failures: Ronin left a critical variable uninitialized, WazirX lost $230M to a key compromise and contract upgrade exploit, Li.Fi passed user input into a low-level call, and Minterest’s mUSDY market reentered itself to zero. All preventable. All devastating.
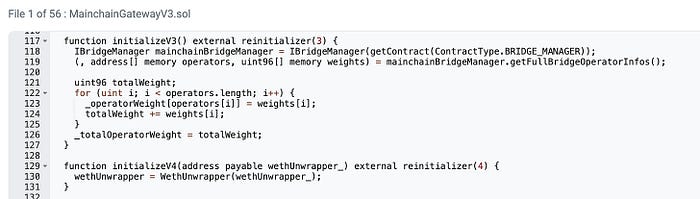
On August 6th, the Ronin Network exploit on the Ethereum mainnet resulted in a $12M loss. The root cause was a misconfiguration during the latest contract upgrade. The _totalOperatorWeight variable was left uninitialized and it defaulted to zero. This allowed the attacker to meet the minimum vote weight condition without requiring a signature, enabling them to withdraw assets. The Ronin team has since recovered the stolen ETH and is working to reclaim the USDC, offering a $500K bug bounty.
Exploit Contract: 0xfc274ec92bbb1a1472884558d1b5caac6f8220ee
Transaction Hash: 0xbce5b8548db486c561948e8a177c8ccaa72810f972cee3909ea50af015a60ad8
On July 18th, WazirX exploit on the Ethereum mainnet resulted in a $230M loss. The root cause was the compromise of one of WazirX’s self-custody multi-sig wallets. Attackers upgraded the wallet to a malicious contract, enabling unauthorized fund transfers. They exploited a delegate call, which altered the wallet’s implementation to point to their malicious contract, allowing them to drain funds.

Exploit Contract: 0x27fd43babfbe83a81d14665b1a6fb8030a60c9b4
Transaction Hash: 0xe3dba30431bcd1d8b9189460cb973ff0addf332ea423c5b2349ba57e536f0495
On July 16th, the Li.Fi exploit on the Ethereum mainnet resulted in an $11.6M loss. The root cause was a flaw in the depositToGasZipERC20() function within the GasZipFacet.sol contract, which allowed user-controlled data to be passed directly to a low-level call, enabling unauthorized function execution. The Li.Fi team acknowledged the exploit, halted all transactions, and issued warnings to their users.


Exploit Contract: 0xf28a352377663ca134bd27b582b1a9a4dad7e534
Transaction Hash: 0xd82fe84e63b1aa52e1ce540582ee0895ba4a71ec5e7a632a3faa1aff3e763873
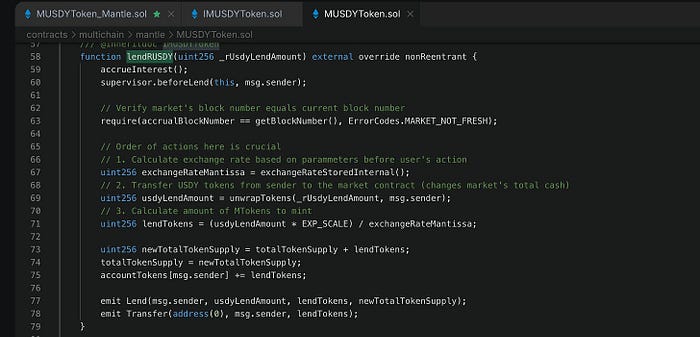
On July 14th, the Minterest exploit on the Mantle Network resulted in a $1.4M loss. The root cause was a reentrancy vulnerability in the mUSDY token smart contract. The attacker used a flash loan to manipulate exchange rates in the mUSDY market by reentering the lendRUSDY() function. By repeatedly borrowing and redeeming USDY tokens, the attacker profited and transferred the stolen funds to Ethereum via the Stargate bridge.
Exploit Contract (on Mantle): 0x14727171E92800ACFE7c4ccFa4F9E572614ff033
Transaction Hash: 0xb3c4c313a8d3e2843c9e6e313b199d7339211cdc70c2eca9f4d88b1e155fd6bd